APIsec Azure Entra SSO Configuration
This guide outlines the process for deploying your APIsec SaaS application to the Microsoft Entra application gallery with SAML authentication, with two groups configured for access control.
Prerequisites
- Azure Entra ID tenant with administrative access
- APIsec login with “ADMIN” user role
Implementation Steps
1. Group Provisioning
Open Microsoft Entra ID
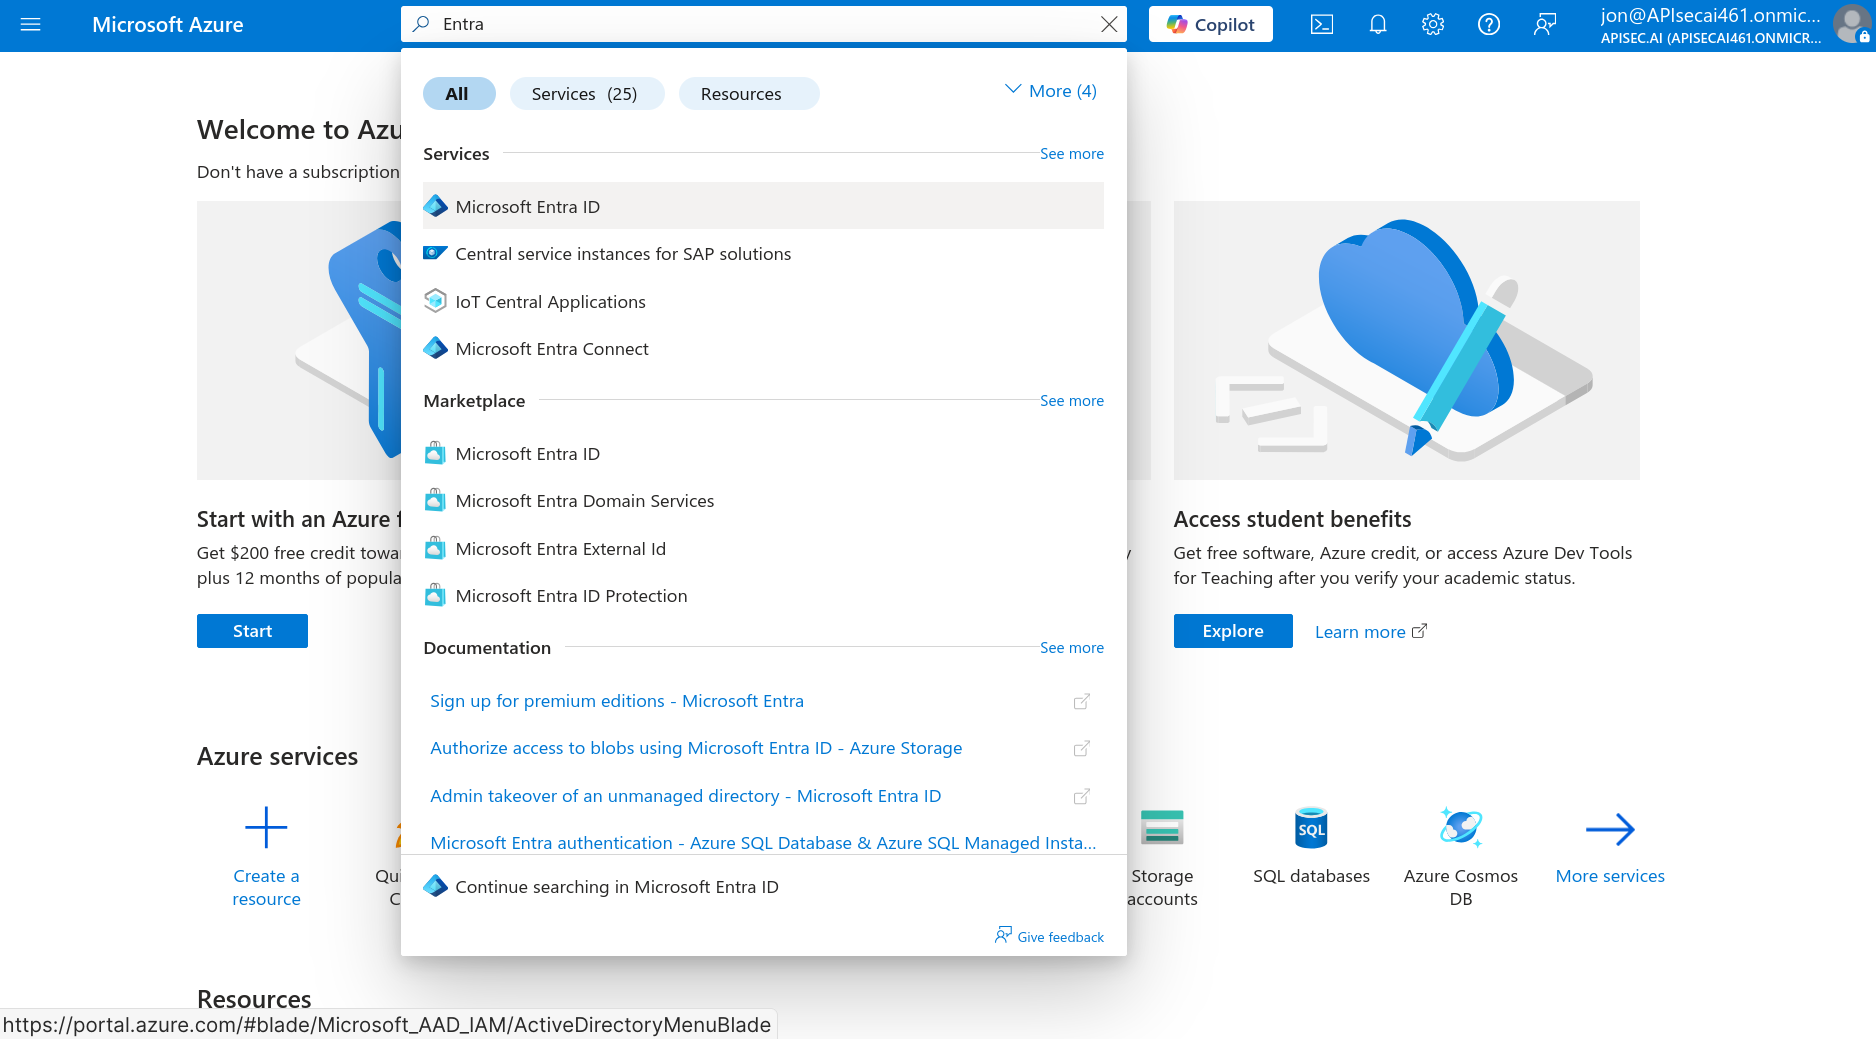
Navigate to Manage > Groups
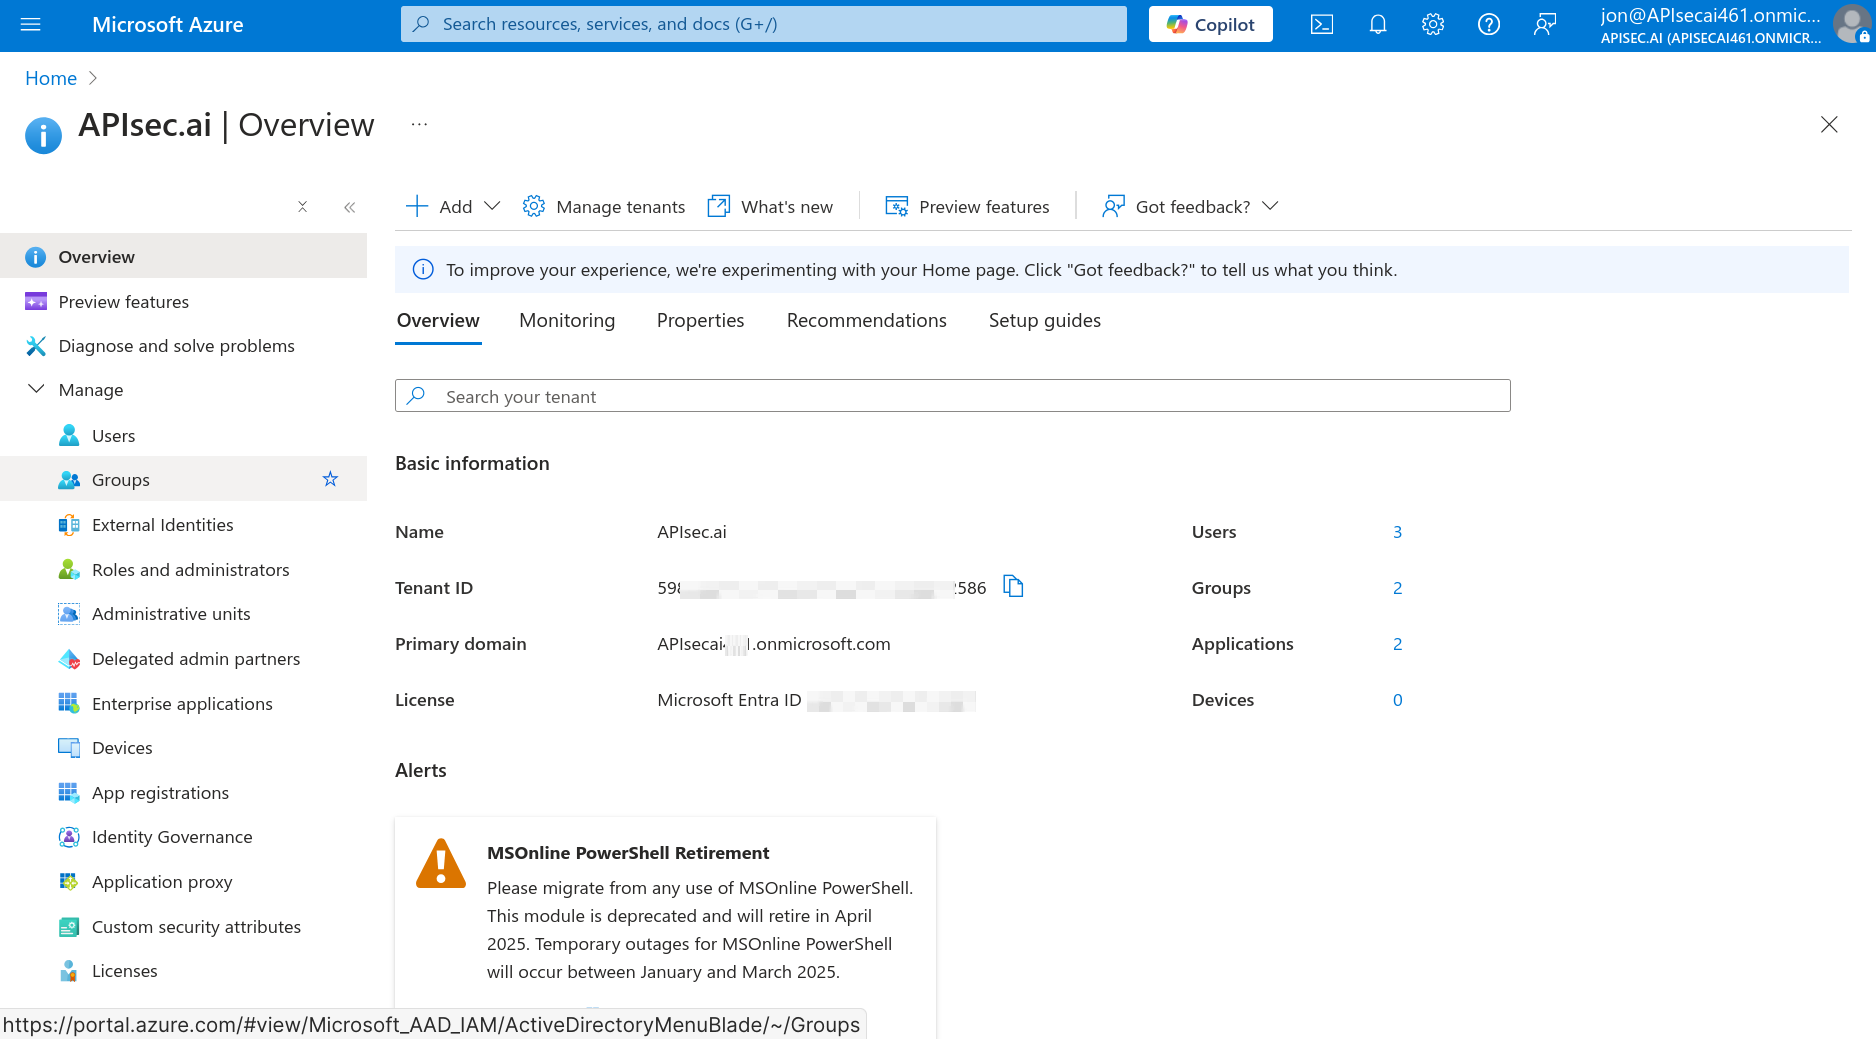
Select "New group"
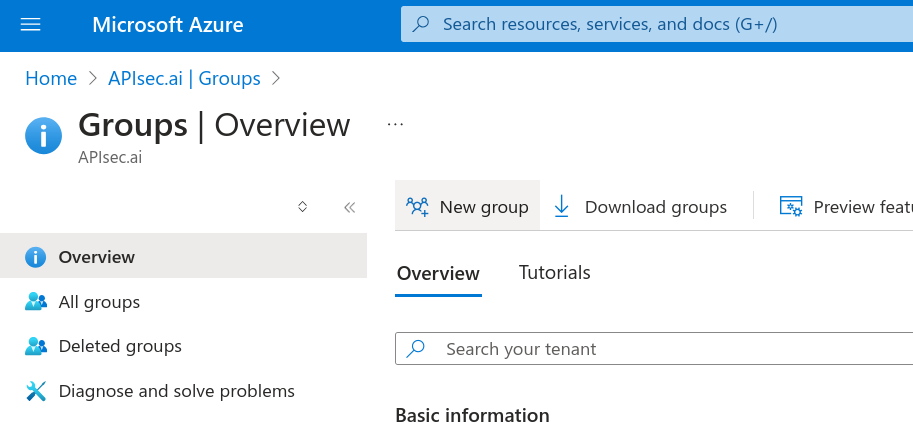
Basic information
-
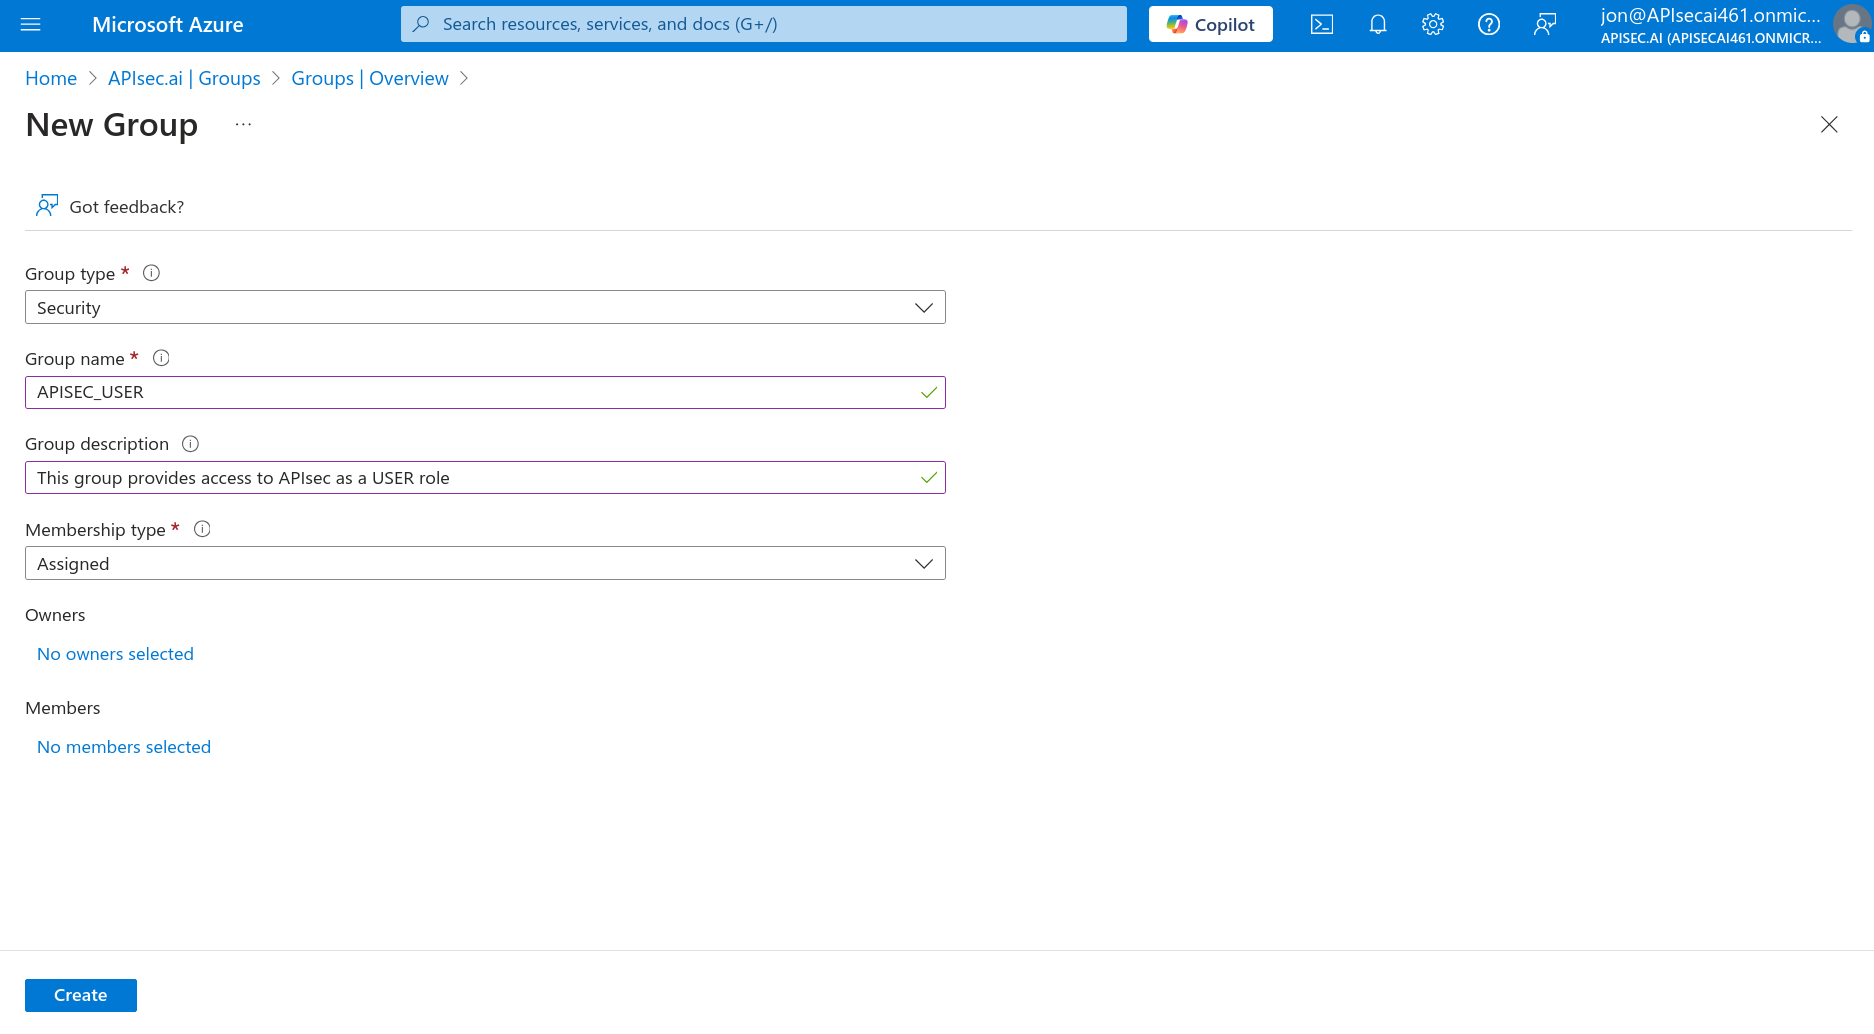
Create first security group for the APIsec application USER role
- Group type: Security
- Group name: APISEC_USER
- Group description: This group provides access to APIsec as a USER role
- Membership type: Assigned
-
Create second security group for the APIsec application ADMIN role
- Group type: Security
- Group name: APISEC_ADMIN
- Group description: This group provides access to APIsec as an ADMIN role
- Membership type: Assigned
-
Create third security group for the APIsec application VIEWER role
- Group type: Security
- Group name: APISEC_VIEWER
- Group description: Users with read-only (viewer) access in APIsec.
- Membership type: Assigned
-
Create fourth security group for the APIsec application GLOBAL VIEWER role
- Group type: Security
- Group name: APISEC_GLOBAL_VIEWER
- Group description: Users with read-only (viewer) access across all applications in APIsec.
- Membership type: Assigned
Note: APISEC_GLOBAL_VIEWER is optional
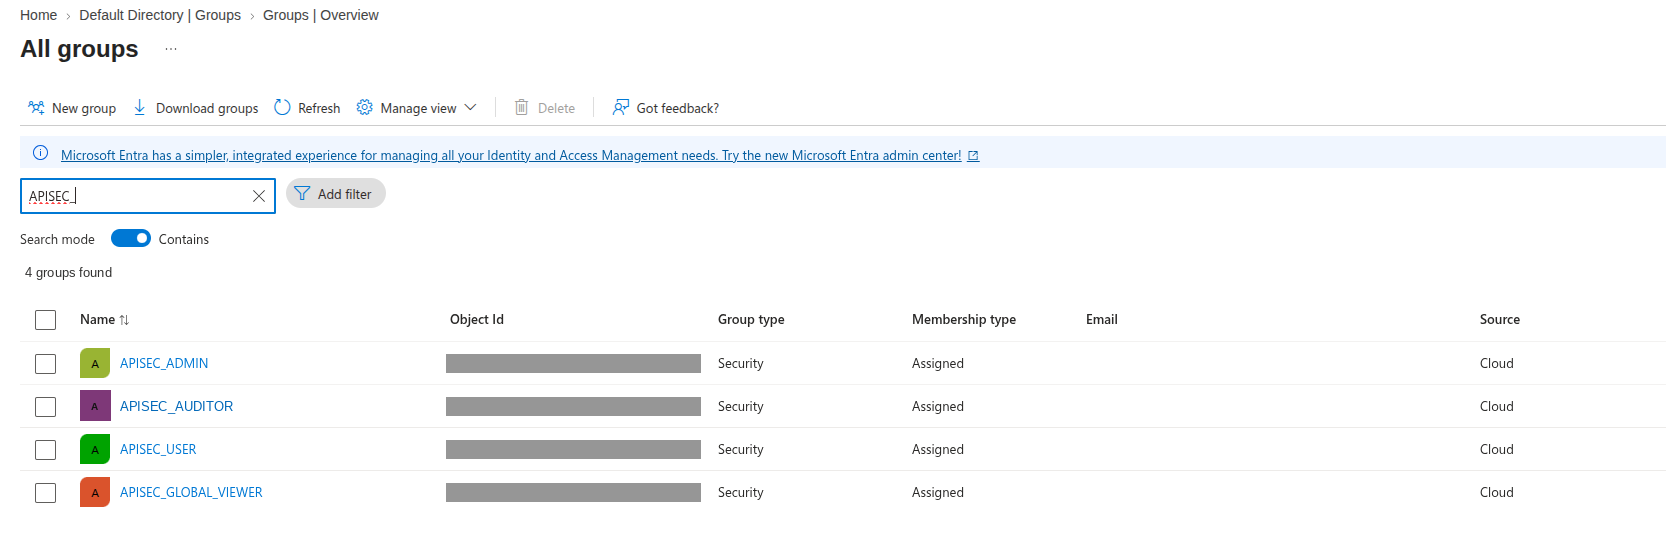
Any member added to one of these groups gains access to your APIsec application with the corresponding role: ADMIN, USER, VIEWER, or GLOBAL VIEWER.
2. Application Registration
Return to Microsoft Entra ID, and register the application Select "Enterprise applications" from the menu
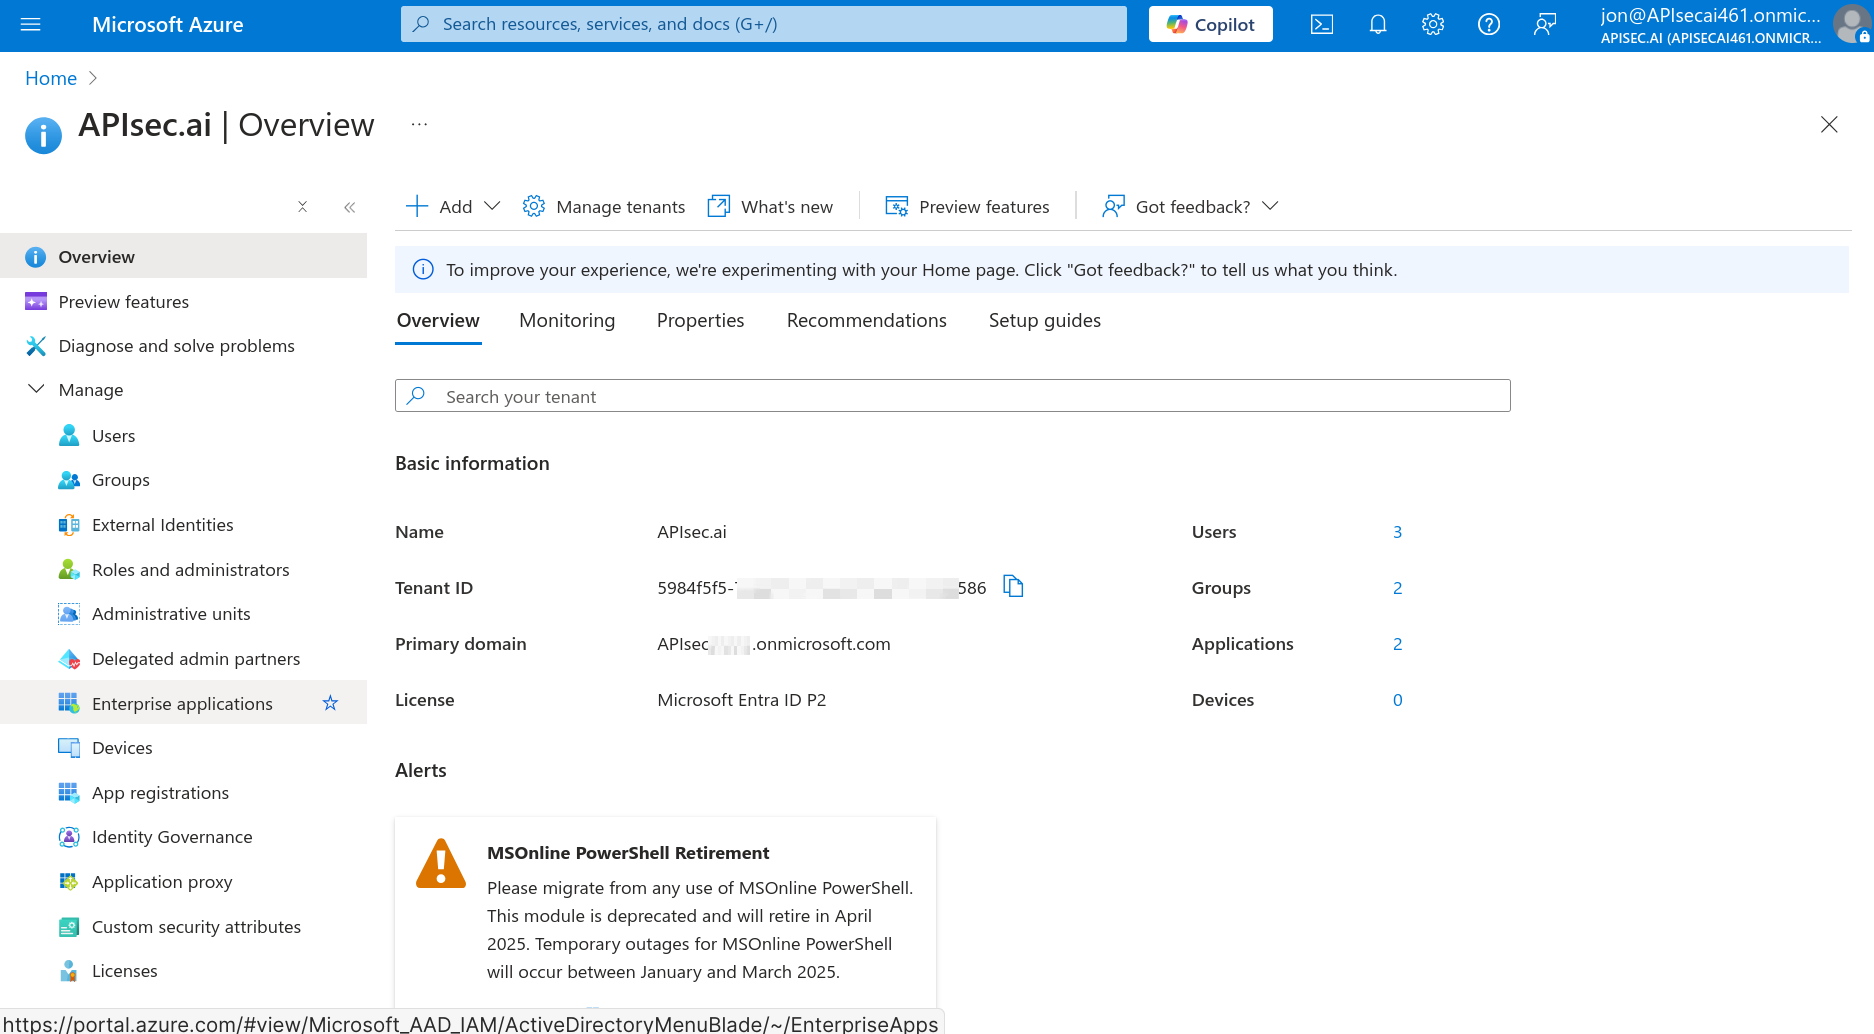
Basic information.
Create a "New application"
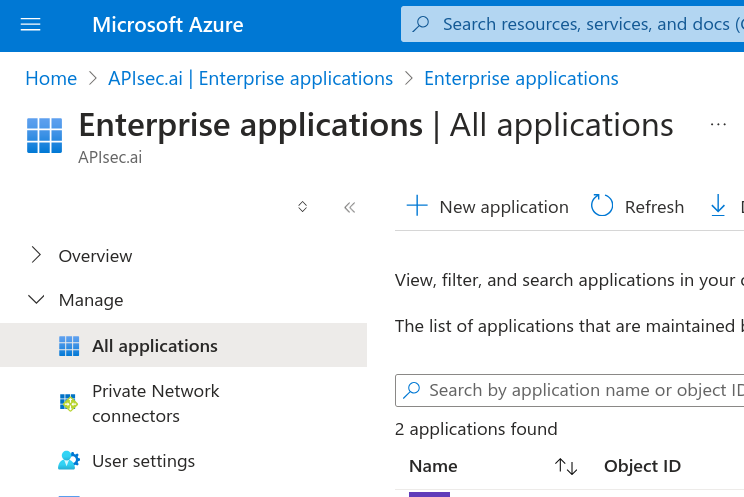
Select "Create your own application"
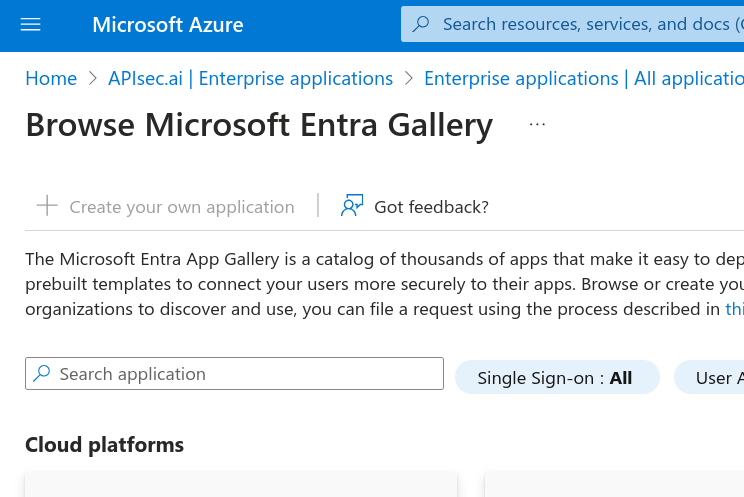
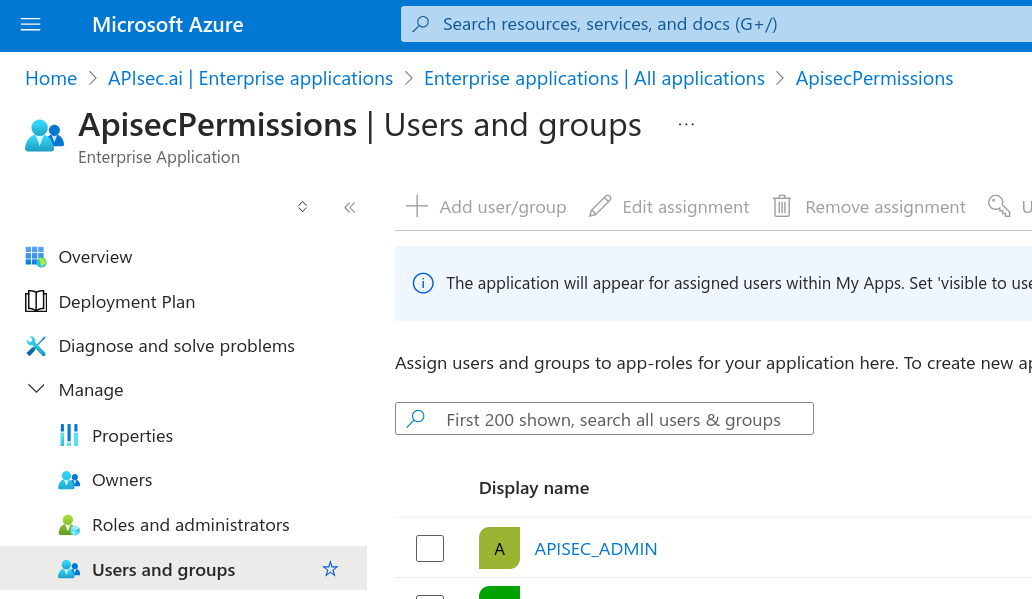
Name the application as appropriate for your organization, e.g. APIsecAccess The radio button for "Integrate any other application you don’t find in the gallery (Non-gallery)" should be selected Click the blue "Create" Configure basic properties and redirect URIs From the left navigation, select Manage then open Users and groups
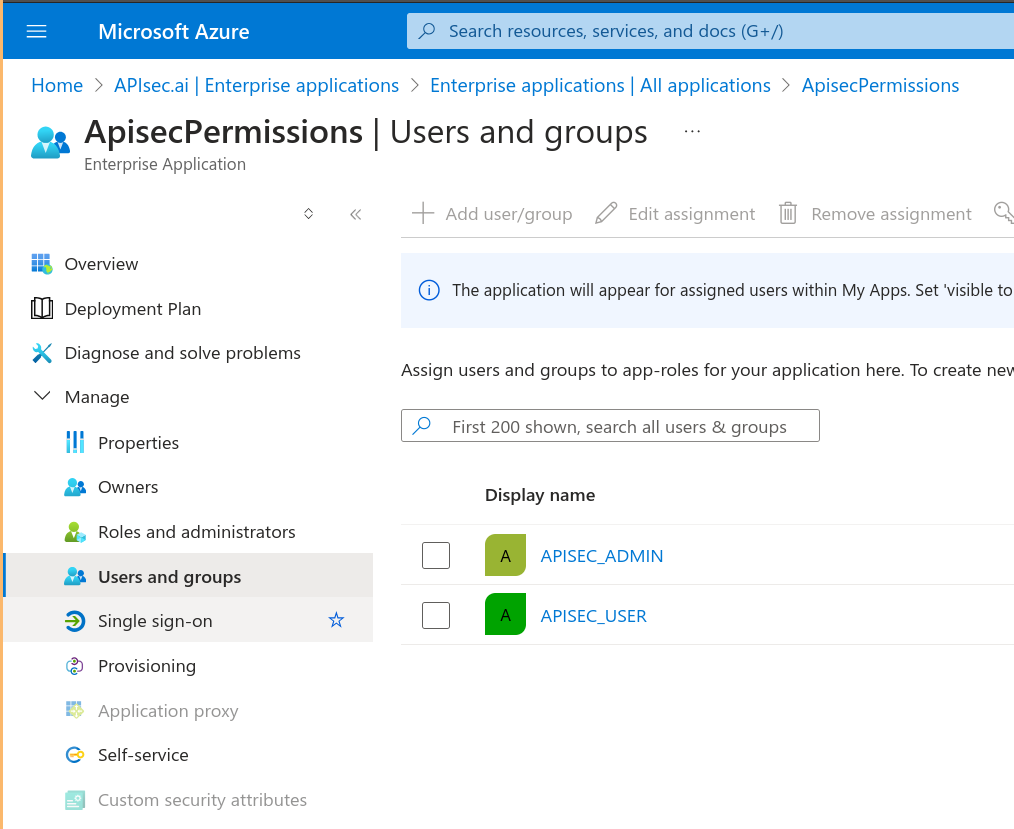
Select Add user/group
In Add Assignment
Search for APISEC* (the two groups created above)
Check the boxes for APISEC_ADMIN, and APISEC_USER
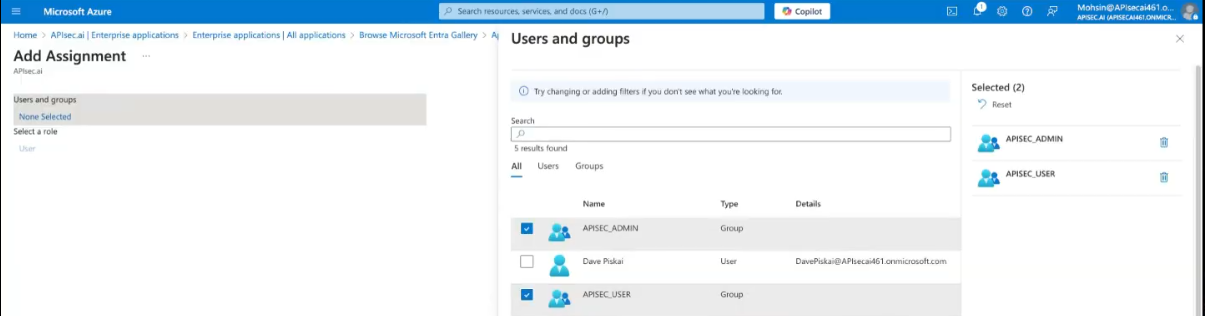
Select and then "Assign"
These two groups are now assigned to the enterprise application
3. Single sign-on Configuration
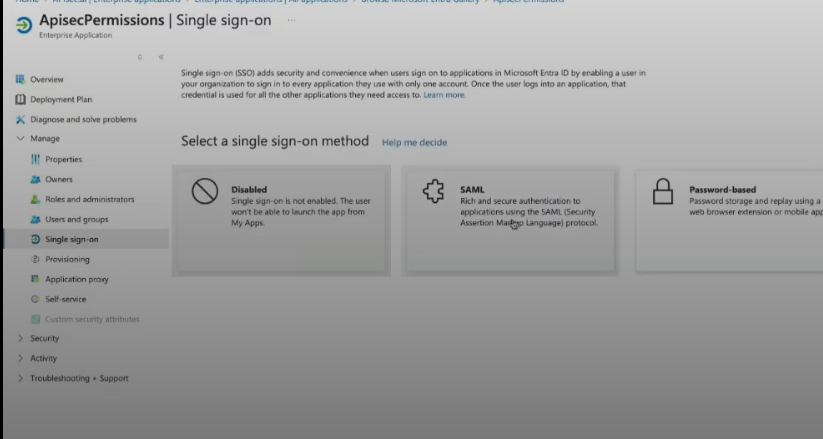
In the Enterprise Application, select the Single sign-on menu item from the Manage menu.
Select the large SAML button (single sign-on method)
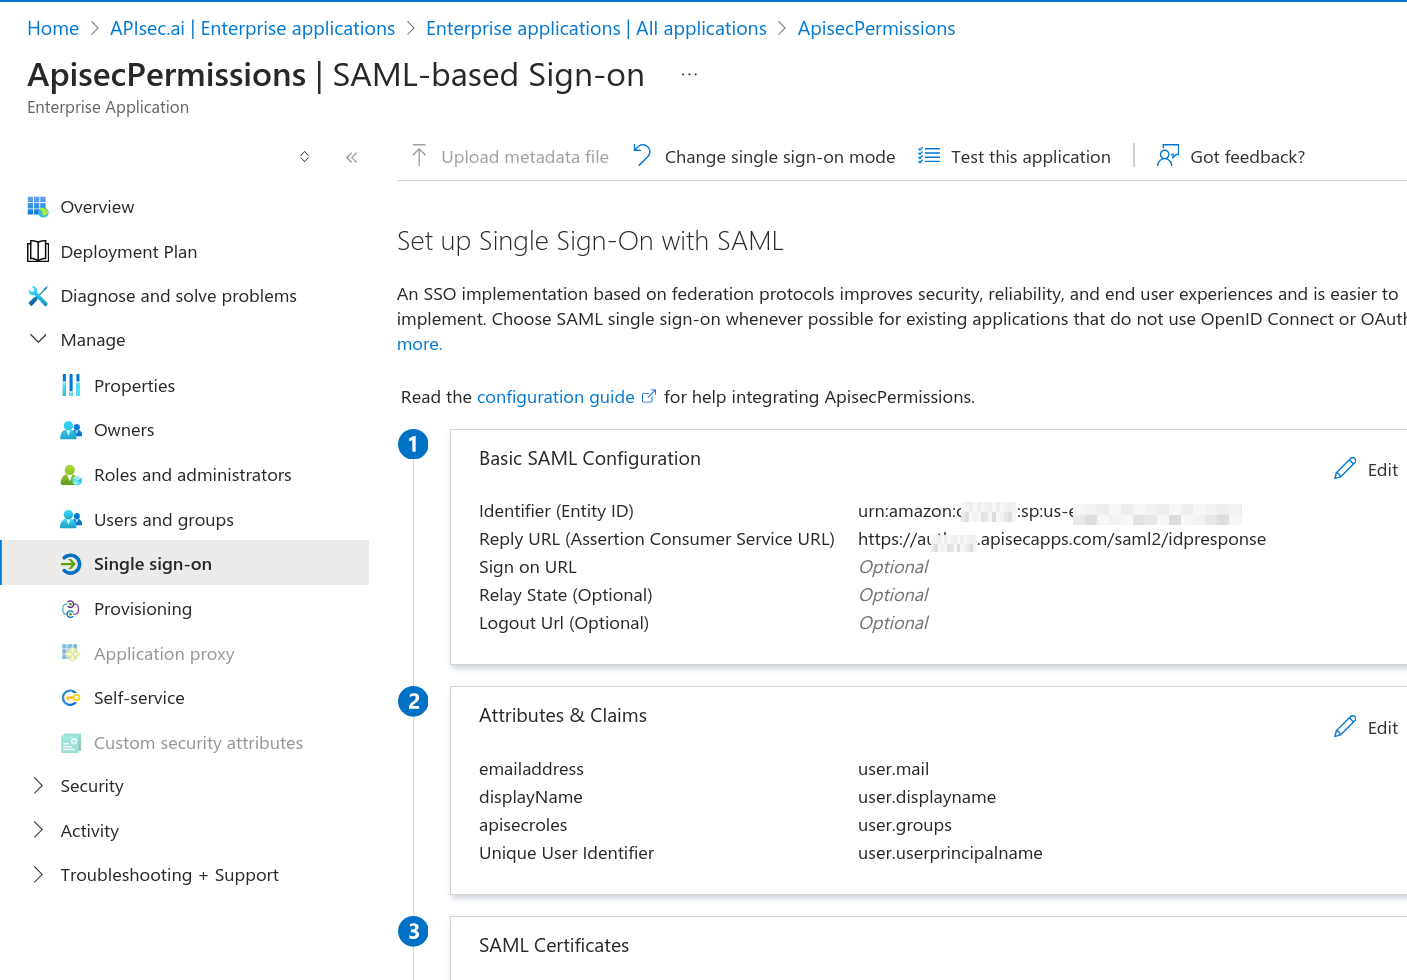
Configure the identifiers and reply URLs step by step in the "Set up Single Sign-On with SAML"
4. APISec Login with SSO and configure
-
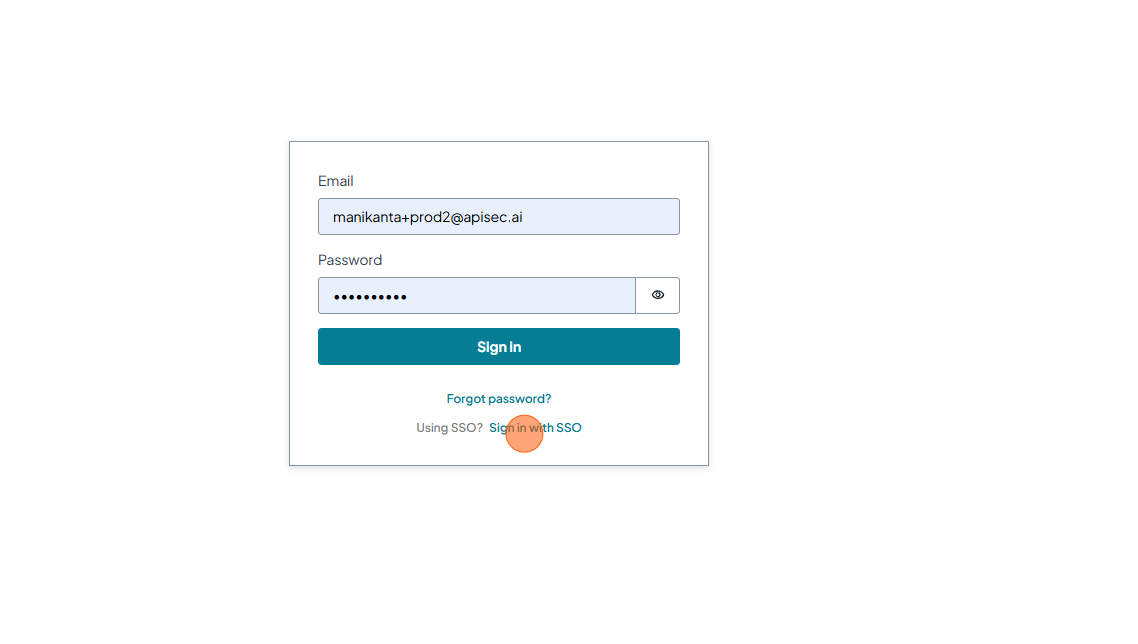
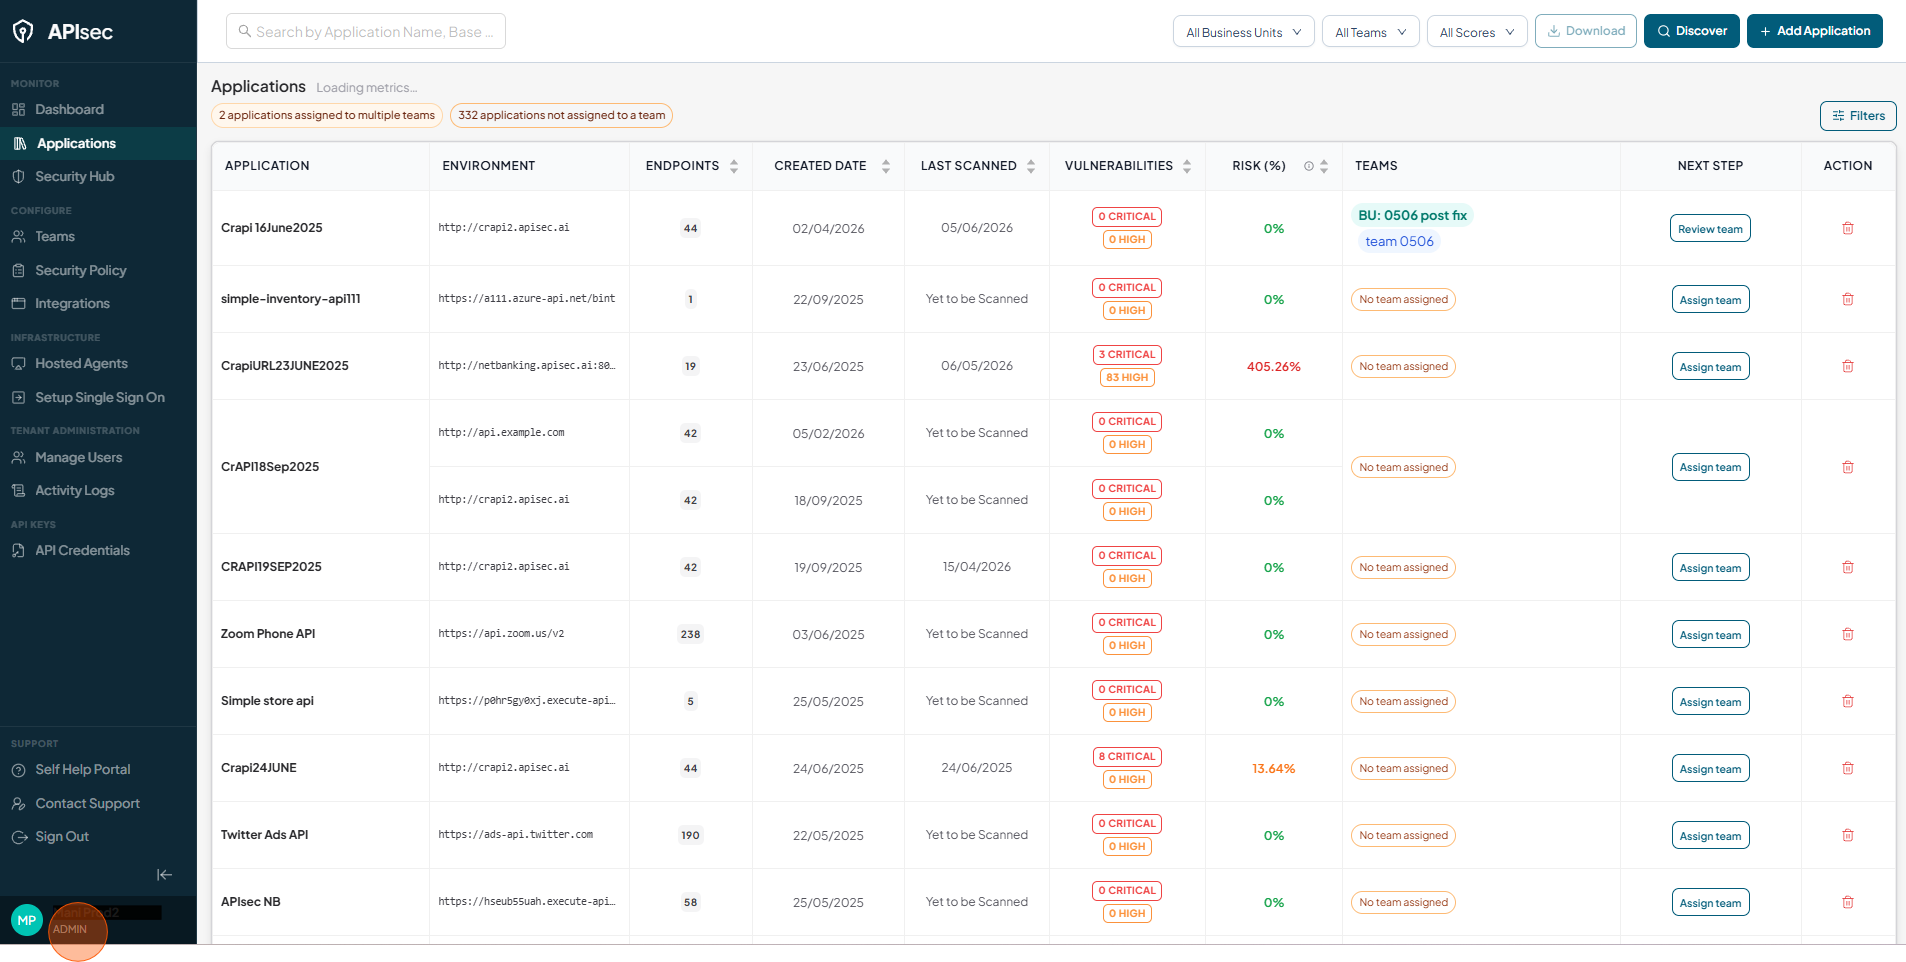
Login to APIsec as a tenant ADMIN (first login may require new password)
-
Verify the user is ADMIN
-
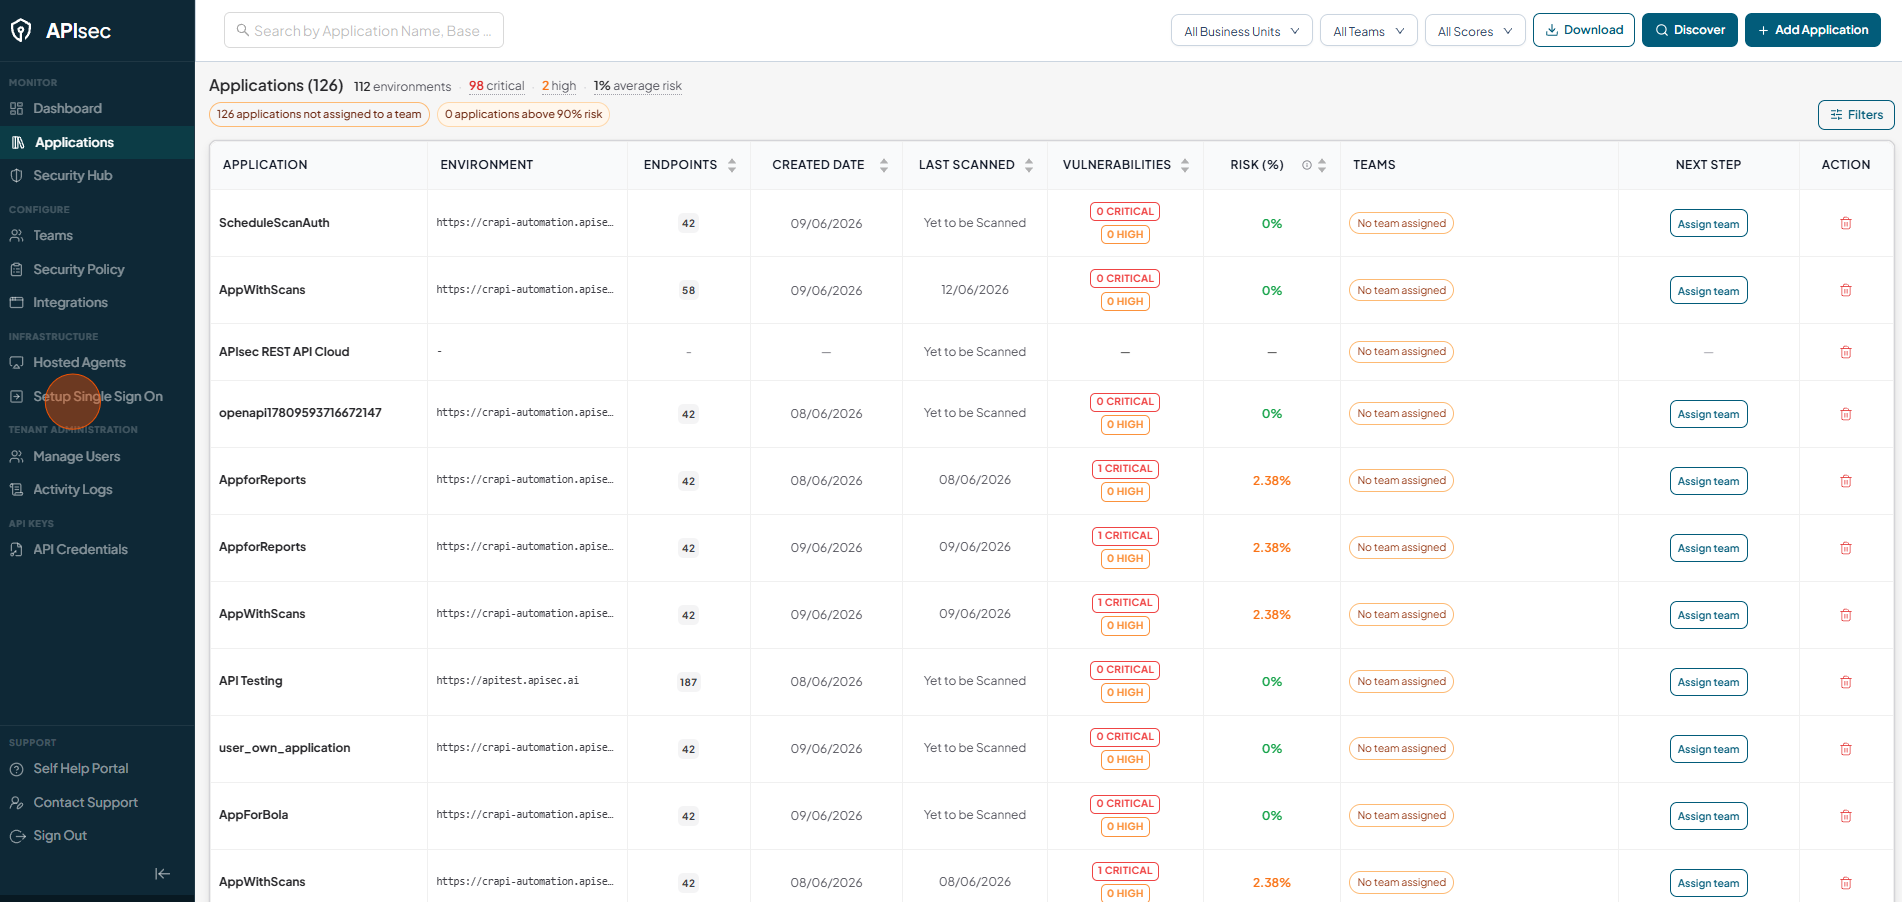
Click Setup Single Sign On
-
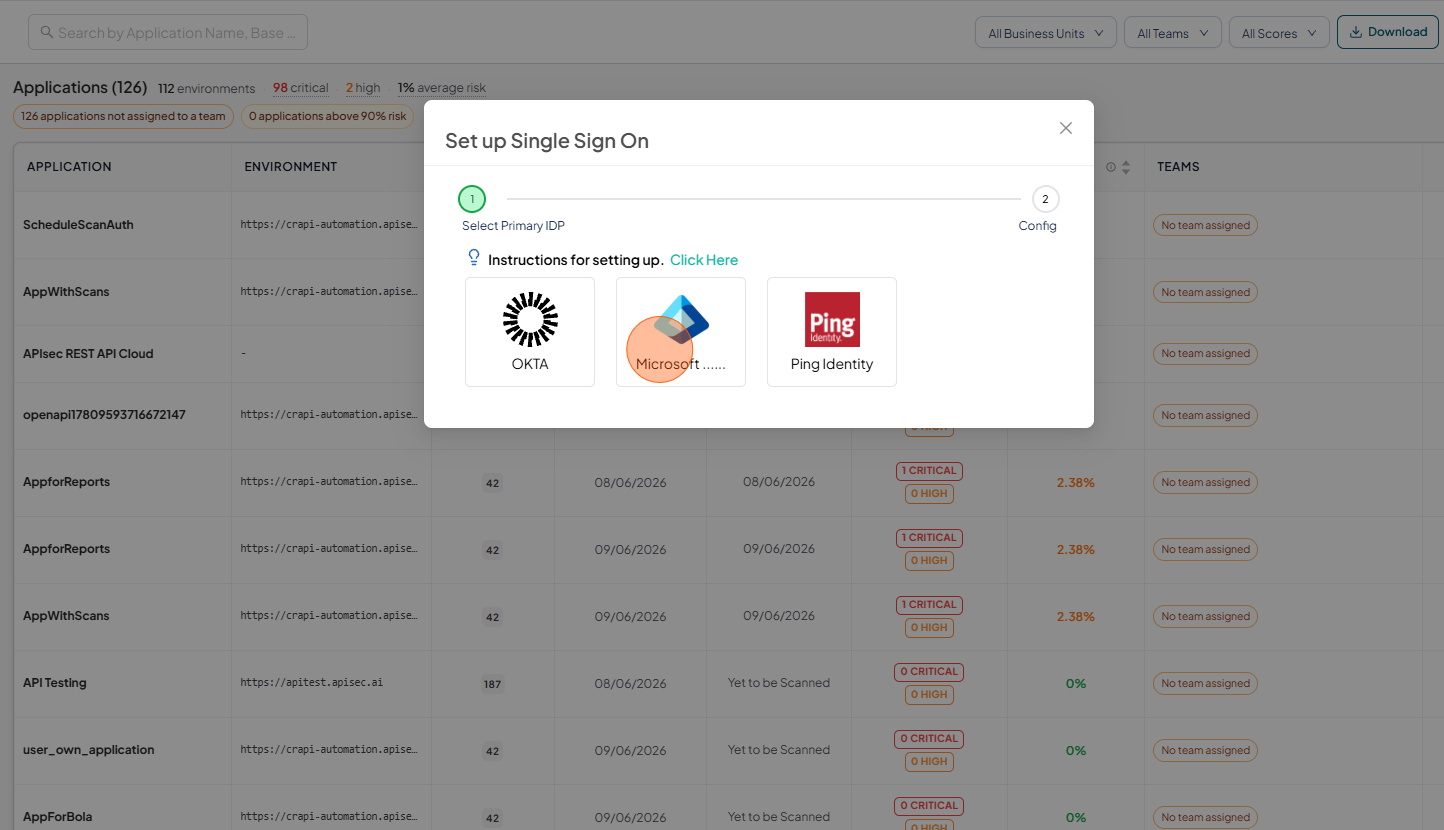
Select Microsoft Entra ID
Copy the Single SignOn Url and the Audience URI
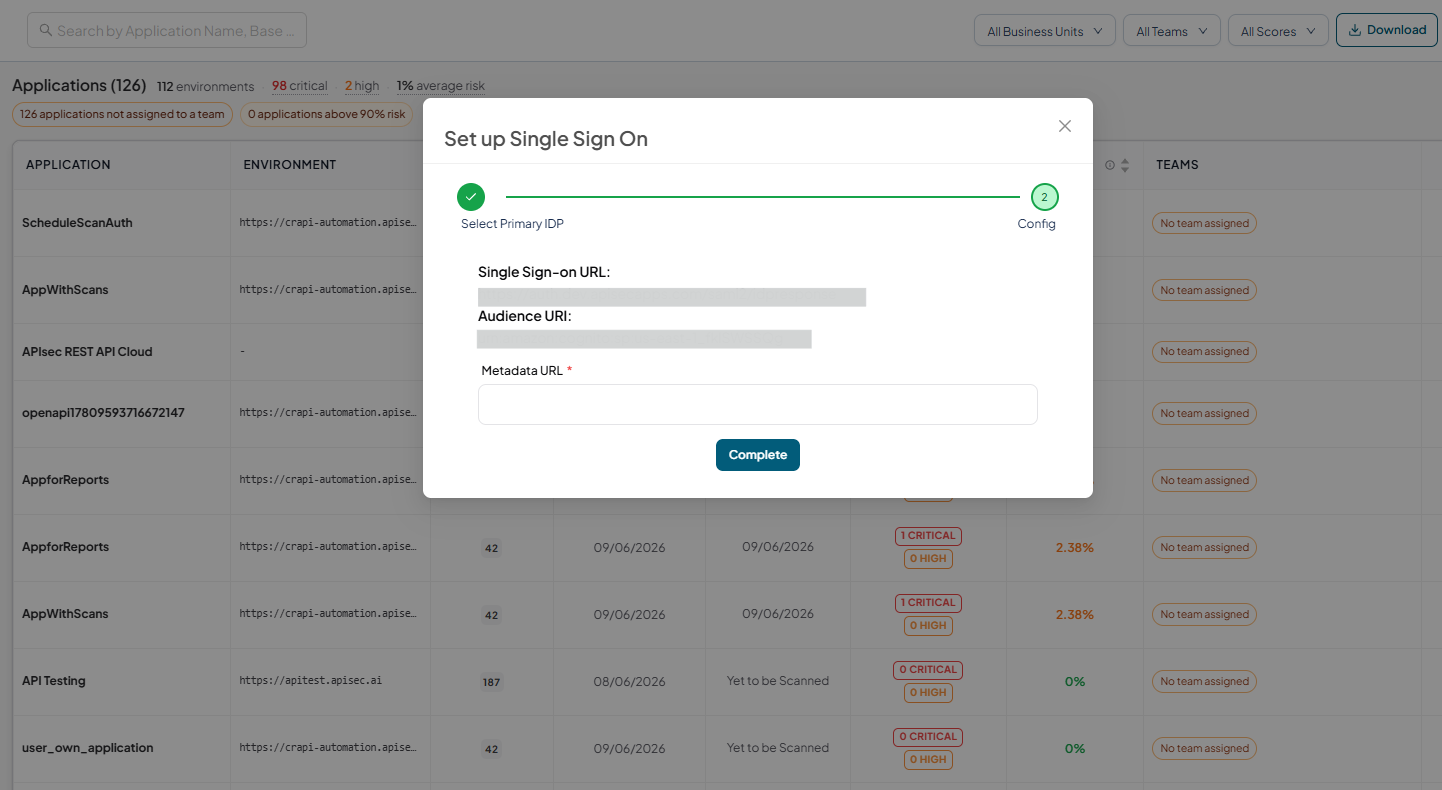
Audience URI: is your Microsoft, Basic SAML Configuration, Identifier (Entity ID)
Take the value from your APIsec SSO setup screen — it is specific to your tenant.
In Entra, Choose "Edit" (Step 1. Basic SAML Configuration) in the Azure portal
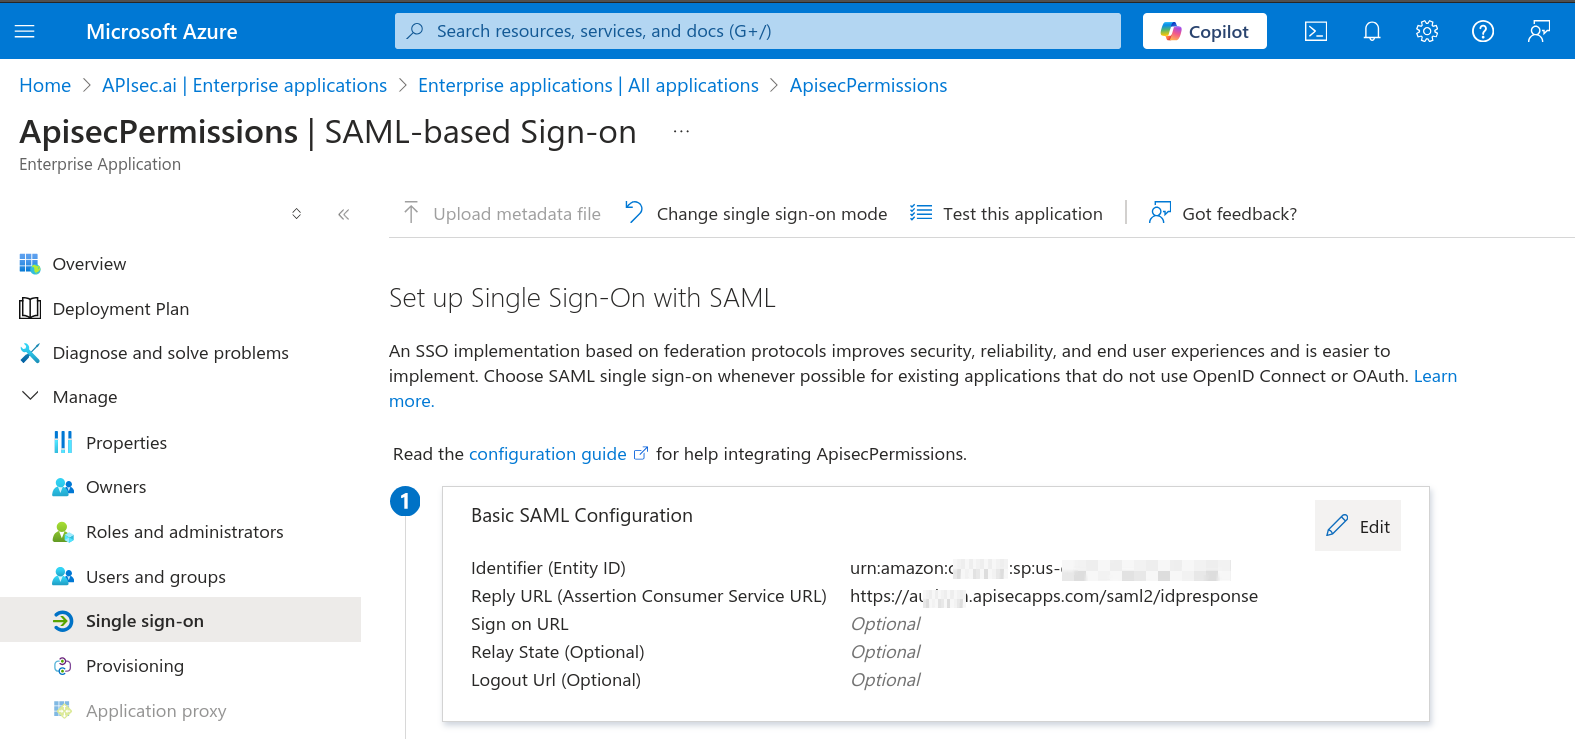
Click Add identifier and paste the Audience URI
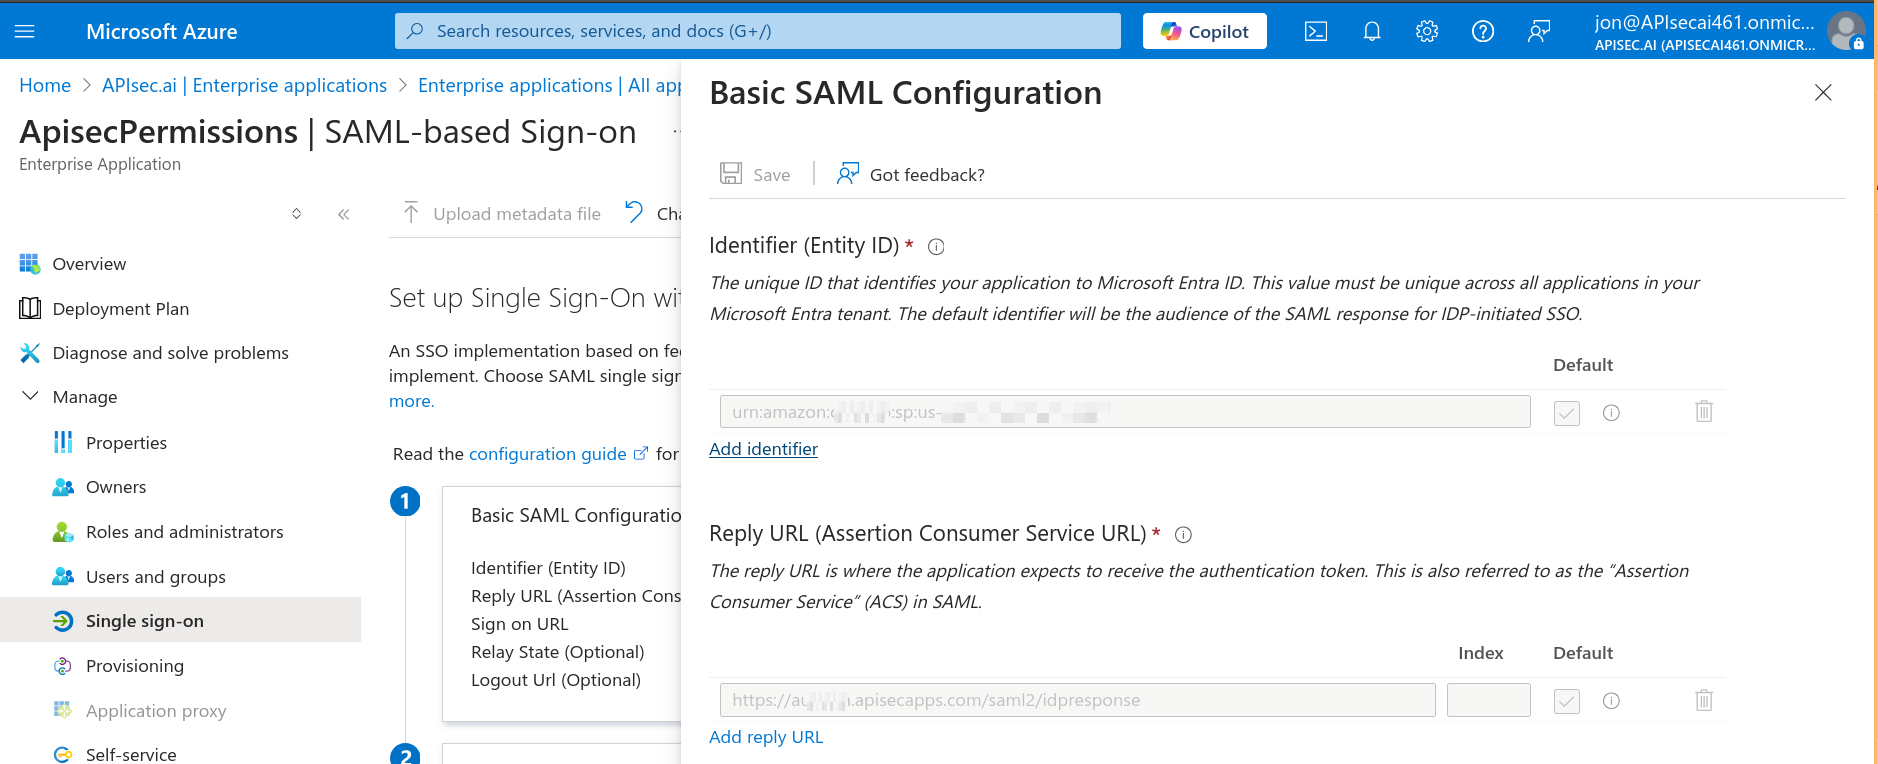
Single SignOn Url: is your Microsoft, Basic SAML Configuration, Reply URL (Assertion Consumer Service URL)
Take the value from your APIsec SSO setup screen. It is a different value from the Audience URI — do not reuse one for the other.
In Azure Enterprise Application, Basic SAML Configuration
Click "Add reply URL"
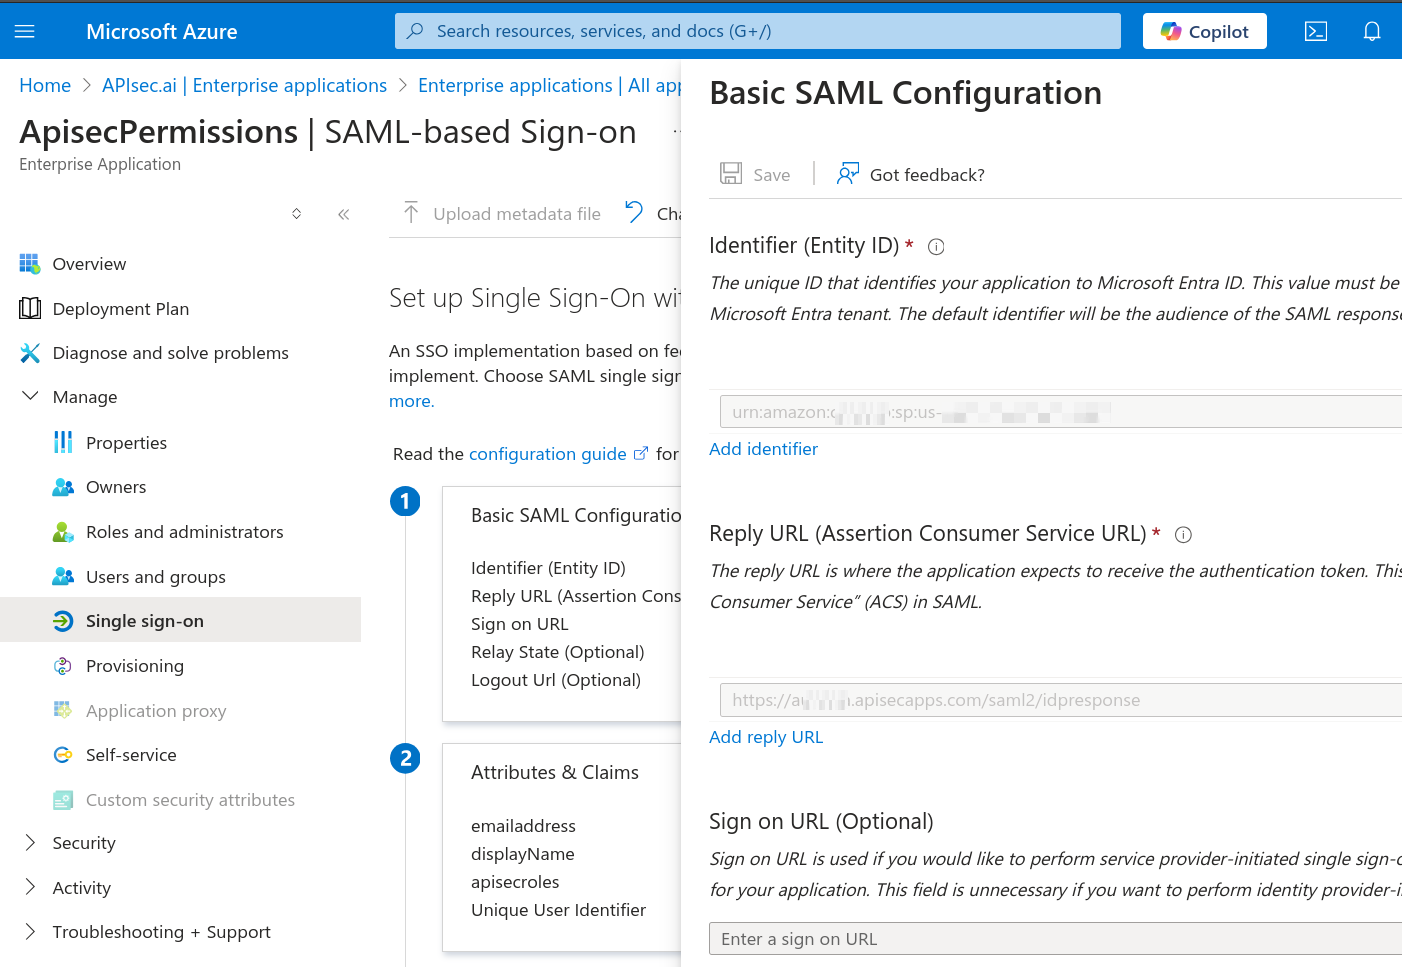
Step 1: Paste your APIsec "Single SignOn Url" as the Entra ID "Reply URL (Assertion Consumer Service URL)", then click "Save".
Step 2: Edit Attributes & Claims in Entra under "Set up Single Sign-On with SAML"
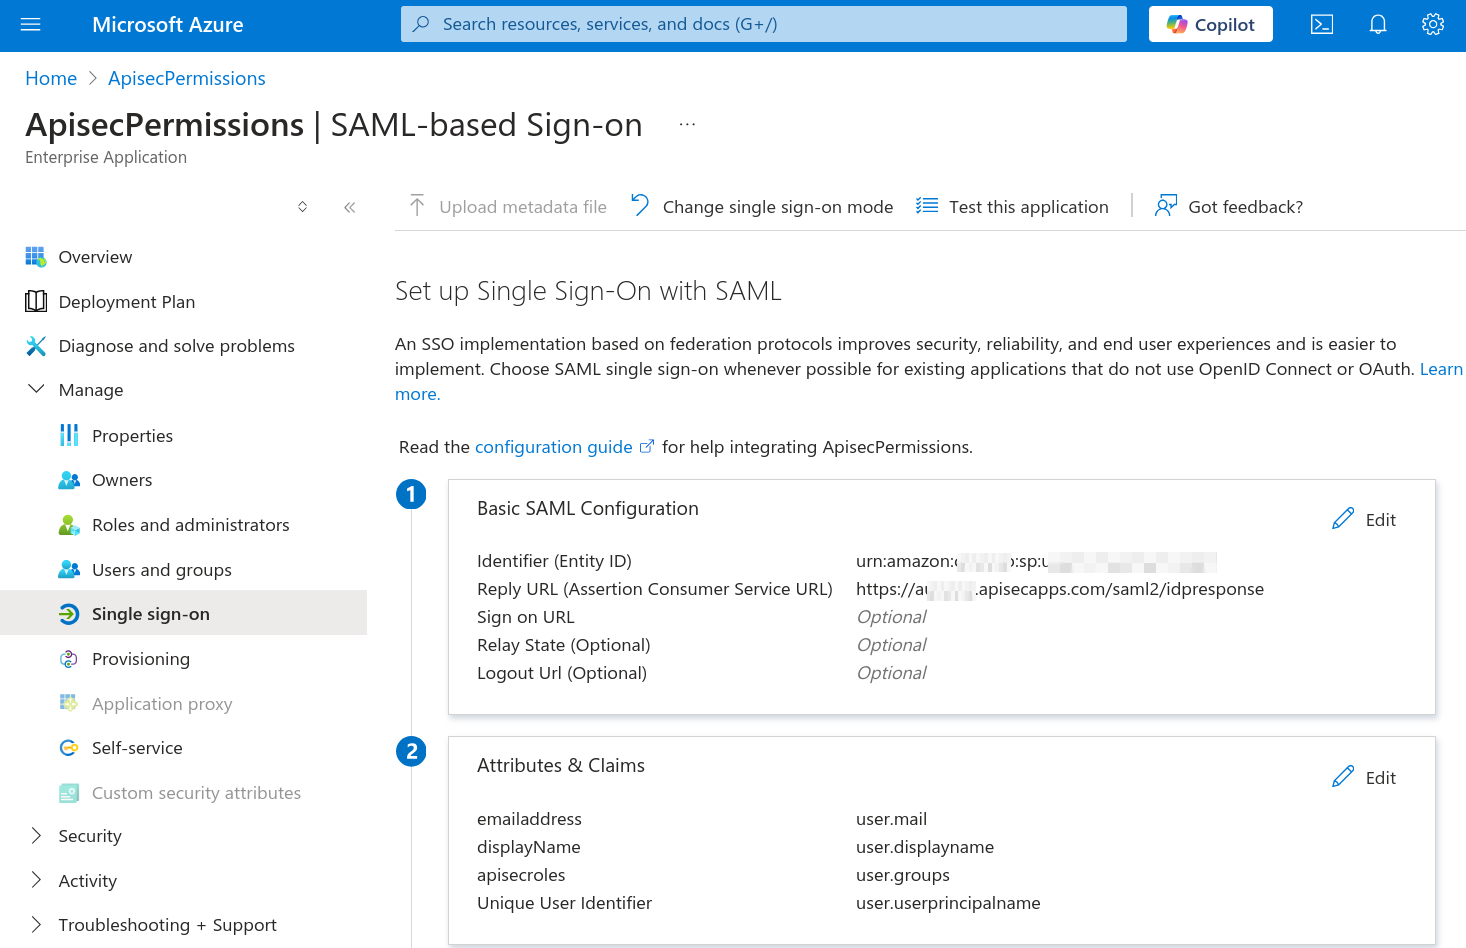
The required claims are:
- user.userprincipalname
- user.groups
- user.displayname
- user.mail
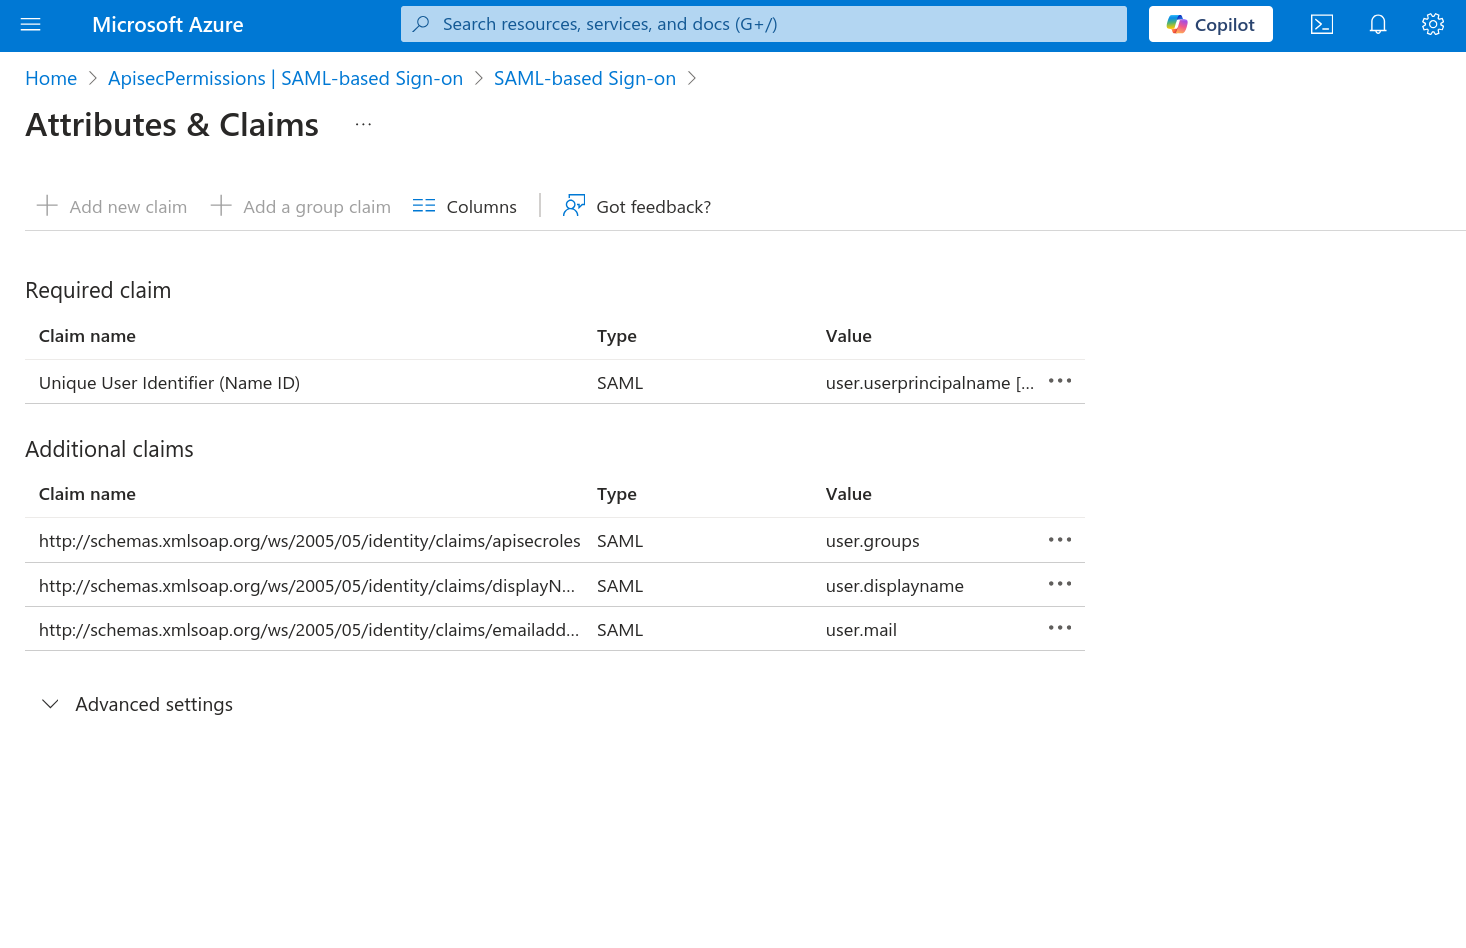
Click Add new claim
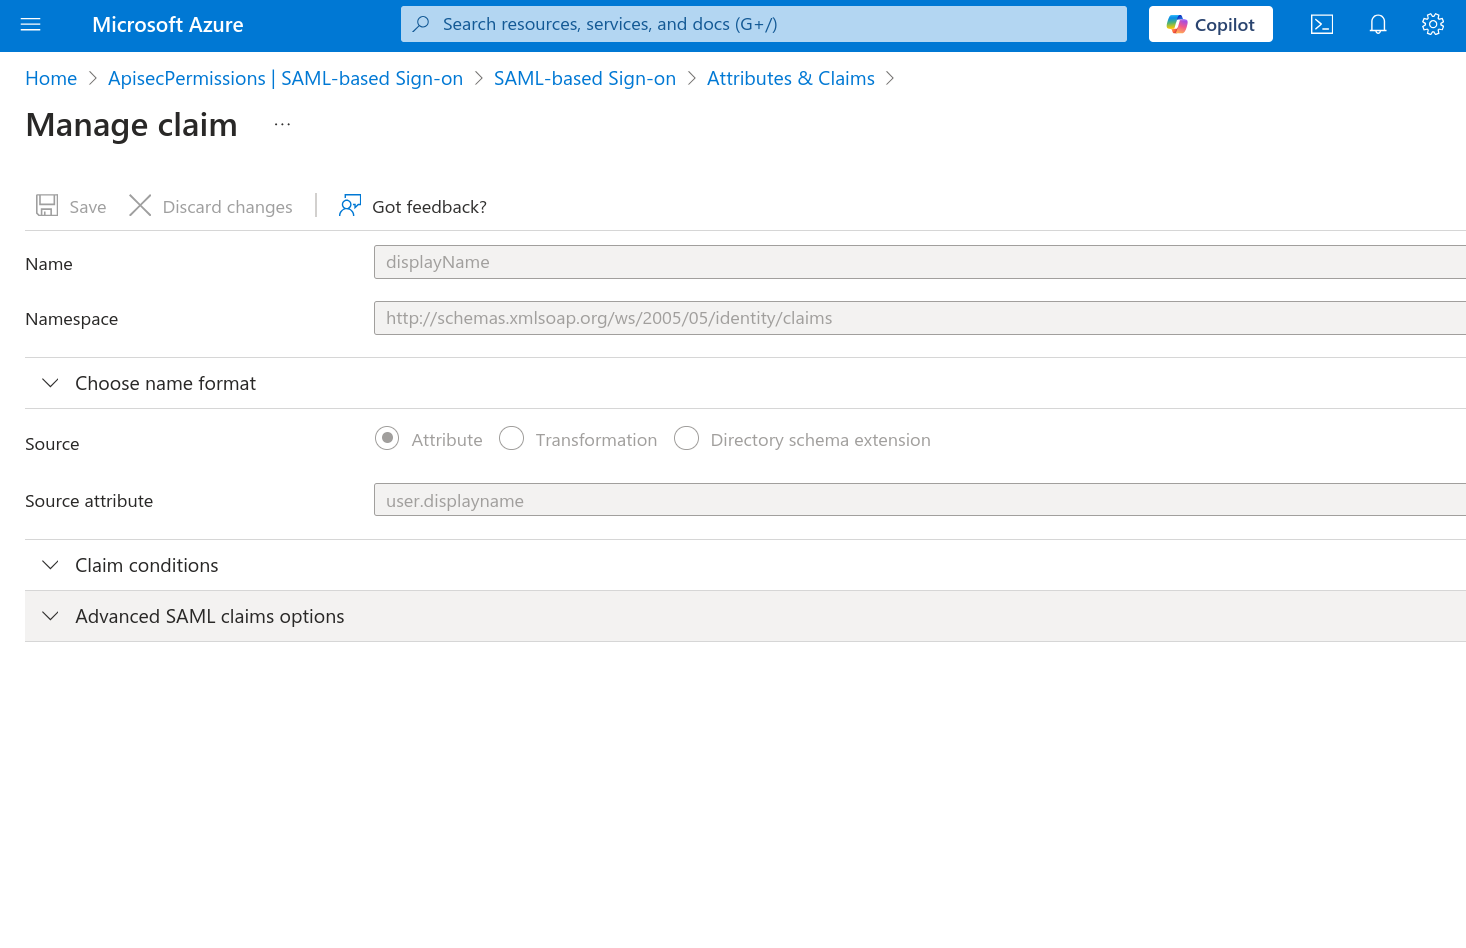
Name is displayName
Use the Namespace for claims:
http://schemas.xmlsoap.org/ws/2005/05/identity/claims
For Source, the radio button "Attribute" will allow you to select "user.displayname"
Click "Save"
Repeat for email: Click "Add new claim"
Name is "emailaddress"
Use the (same) Namespace for claims:
http://schemas.xmlsoap.org/ws/2005/05/identity/claims
The Source is Attribute "user.primaryauthoritativeemail"
Click "Save"
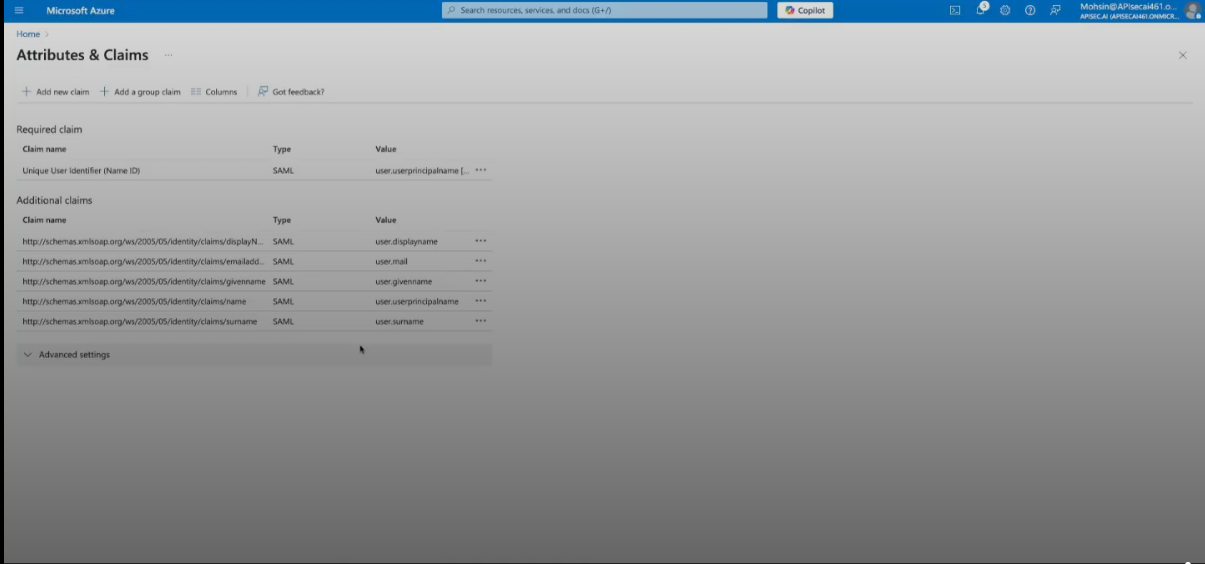
Delete any additional unnecessary "Additional claims" including surname, givenname. Keep only the Required claim UUID and the Additional claims user.groups, user.displayname, and user.mail.
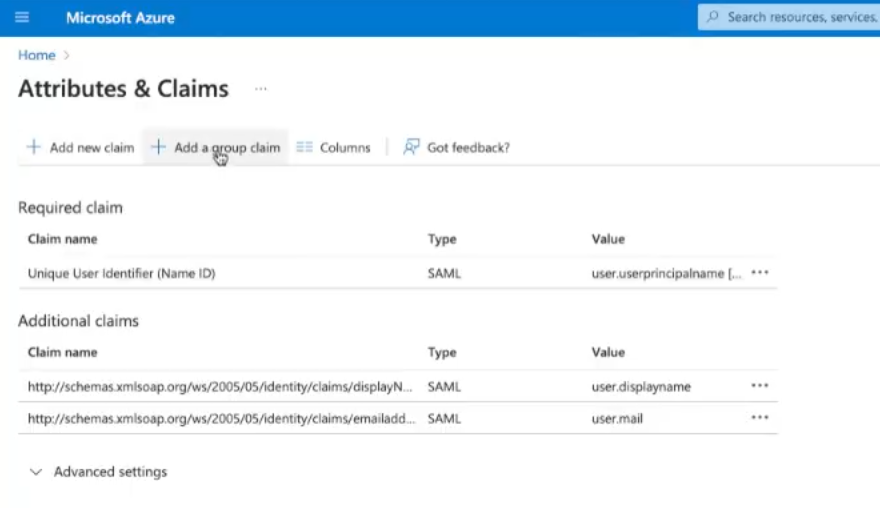
Select "Add a group claim"
The "Group Claims" configuration will open.
Choose "Groups assigned to the application"
Select Source attribute "Cloud-only group display names"
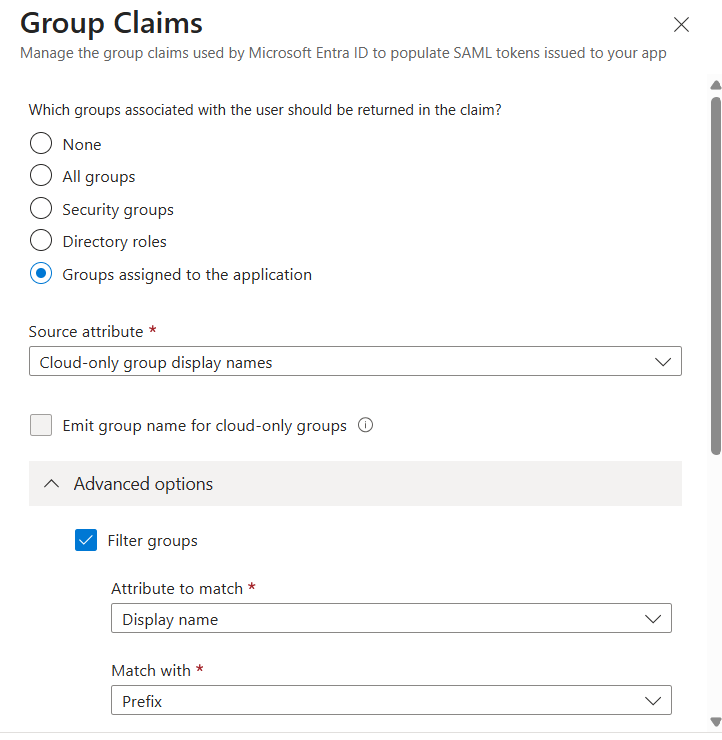
Select "Advanced options" and check "Filter groups"
Attribute to match: "Display name"
Match with String "APISEC" (should match the Group names created above)
Check "Customize the name of the group claim"
Use Name (required): "apisecroles"
Use the (same) Namespace for all claims:
http://schemas.xmlsoap.org/ws/2005/05/identity/claims
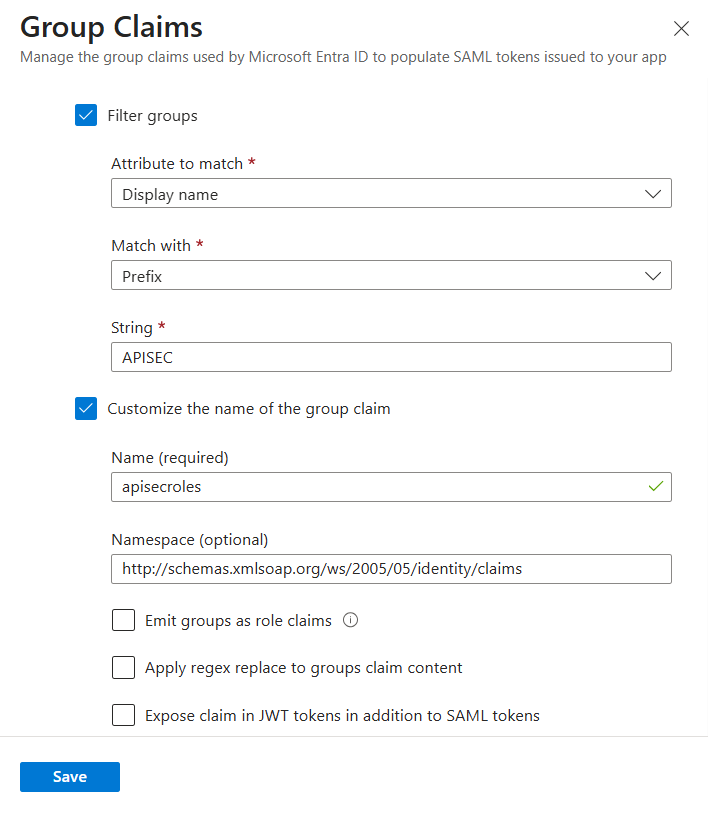
Click "Save"
The completed SAML Configuration will have these attributes and claims
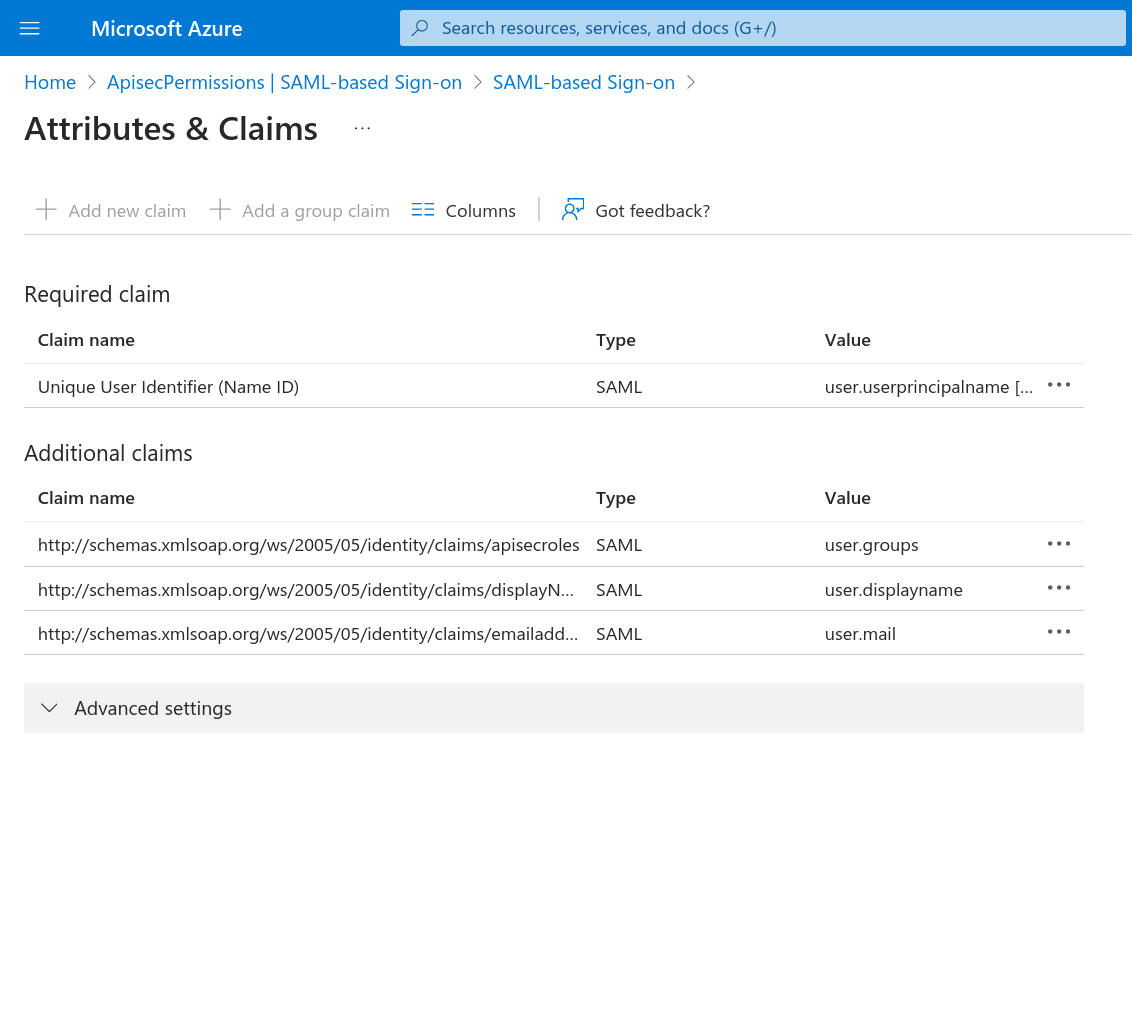
Return to your Enterprise Applications
Select your APIsec application, select Manage, and click "Single sign-on"
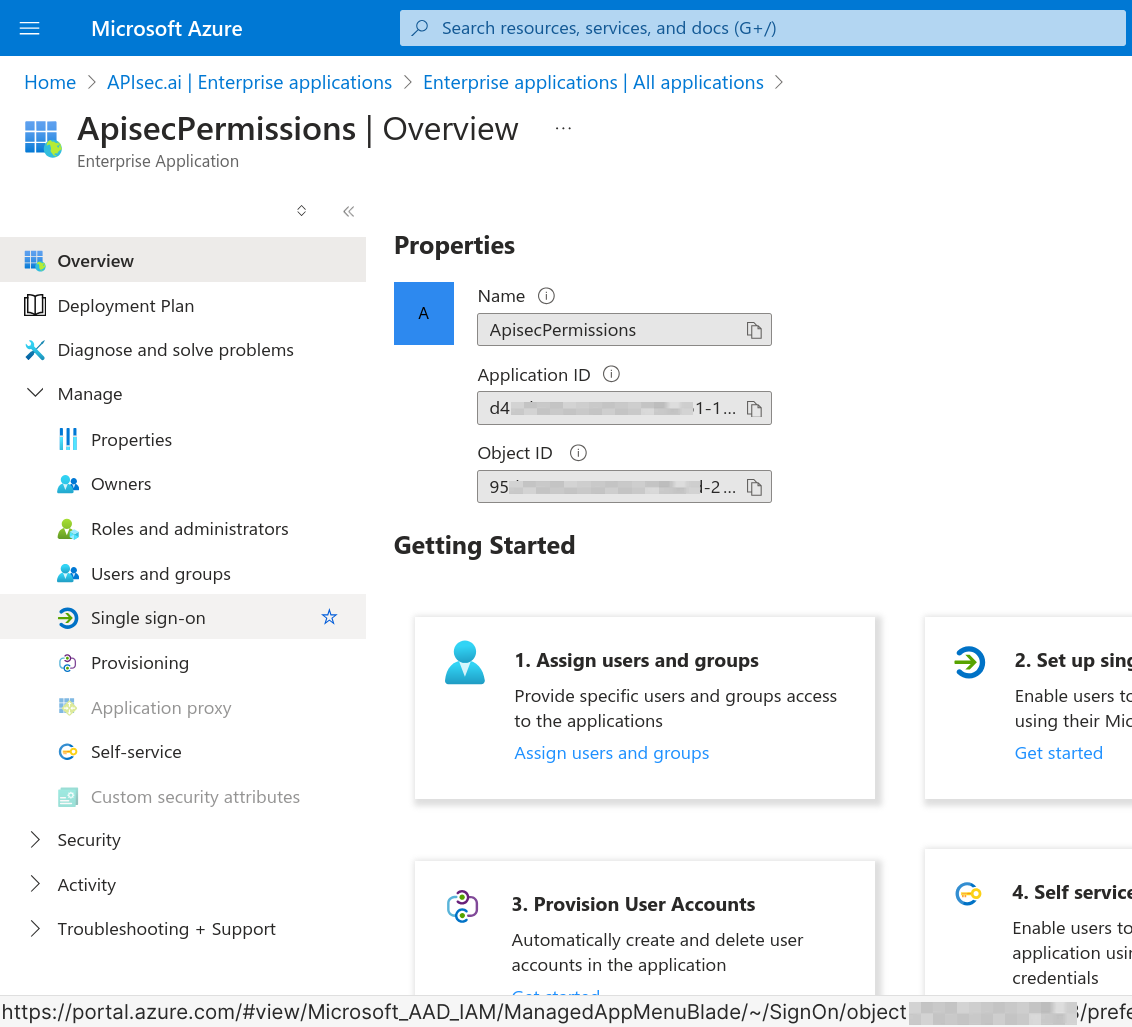
In Section 3 of SAML-based Sign-on, locate the "App Federation Metadata Url"
Use the convenient "Copy to clipboard" link
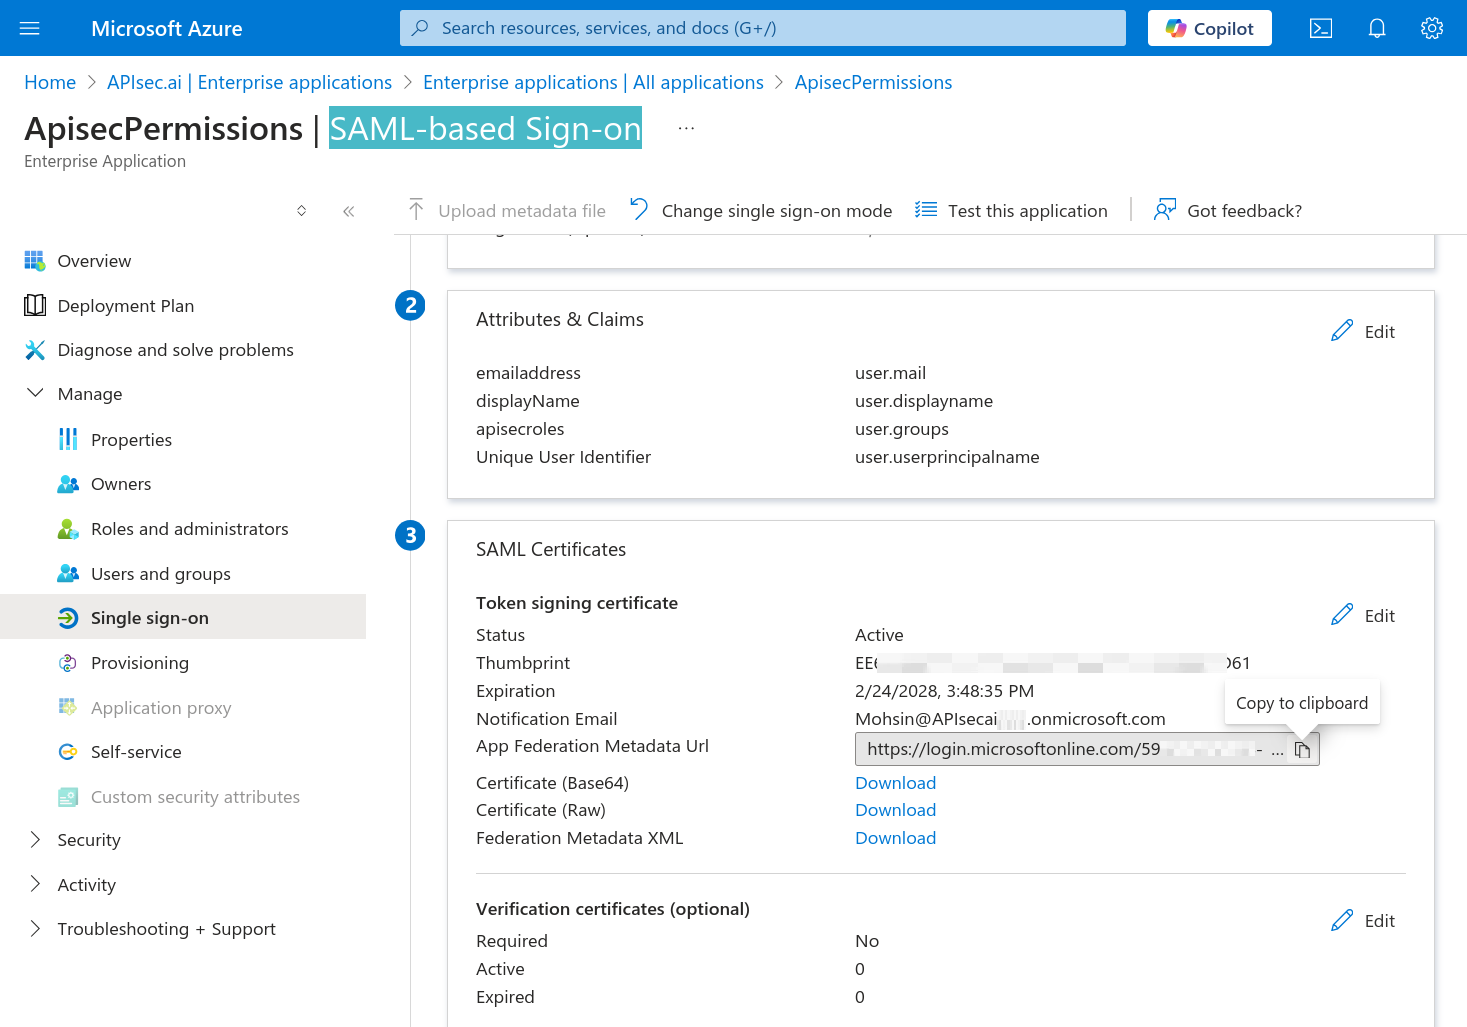
Click "Copy to clipboard"
Switch to the APIsec application and paste into the "Metadata Url" field Click "Complete"
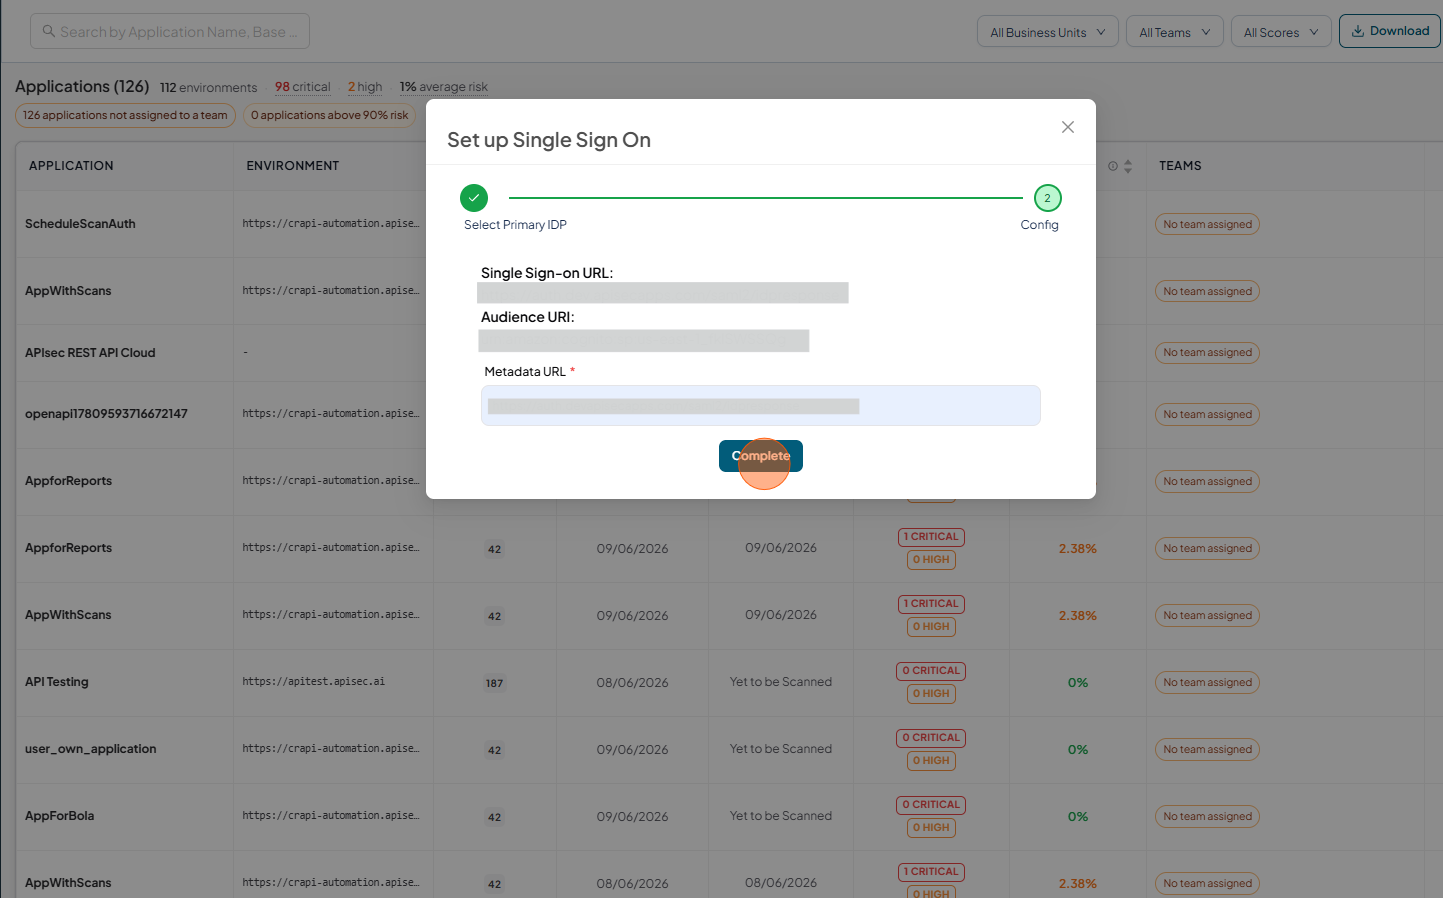
Log out of APIsec.
Test login with an Entra user provisioned to each of your Entra groups.