Manage Headers
Instance-Level Headers
Some APIs require custom non-auth HTTP headers—such as a static cookie, or a unique value like x-base-directory: /foo/bar—on every request. Instance-level headers let you define such a header once at the instance level, instead of attaching it to each authentication (where automated tests can override or remove it) or adding it to every endpoint (error-prone for APIs with hundreds or thousands of endpoints).
Define a header once at the instance level and it's automatically sent with all or selected endpoints, independent of authentication.
You can also enable the "Enable for Reachability Tests" option for a header. This ensures it's included in the very first "base path" check (for example https://api.example.com)—before any endpoint or authentication is used. This is helpful when infrastructure such as load balancers requires a specific header to respond correctly.
Add Header
-
Open your browser and visit: https://<your-tenant>.apisecapps.com
-
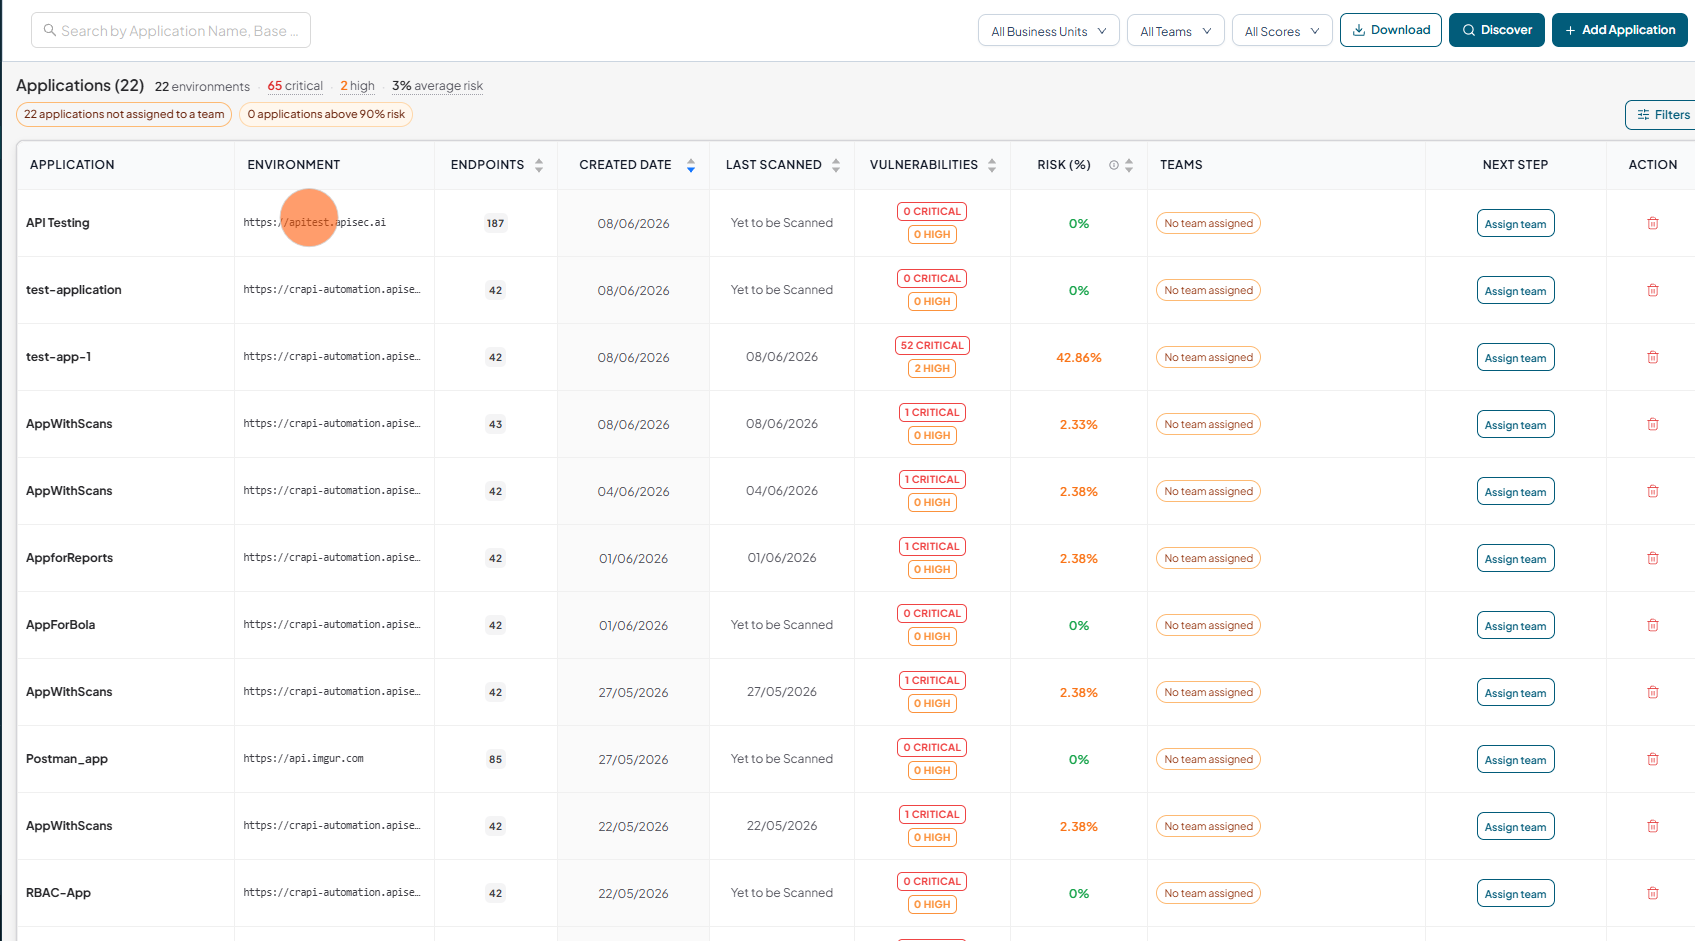
Click the required application.
-
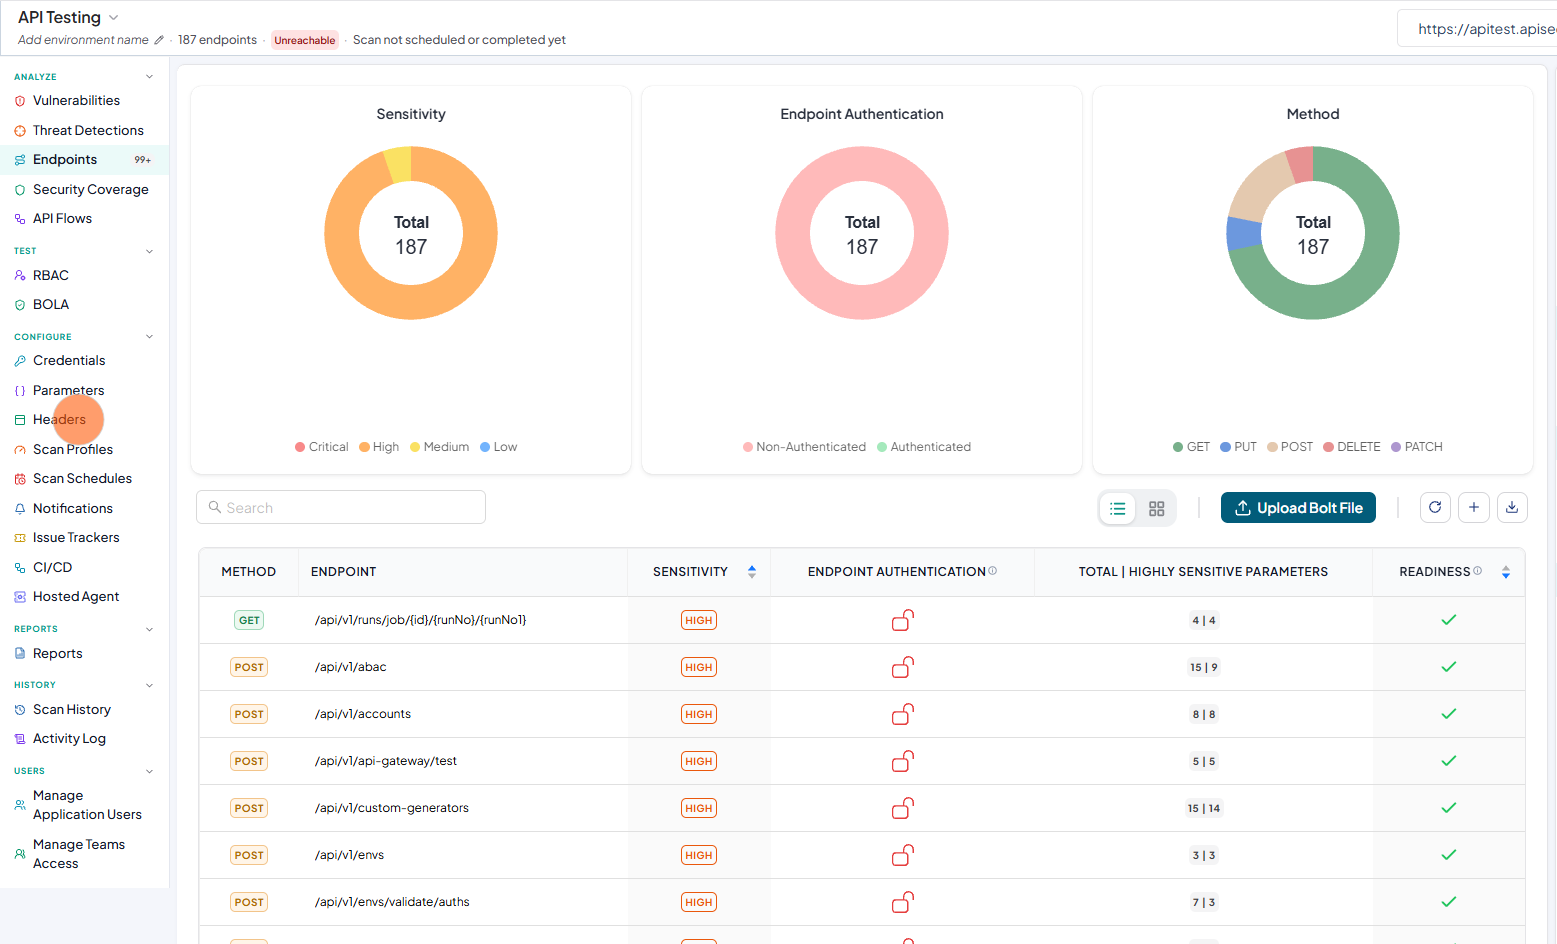
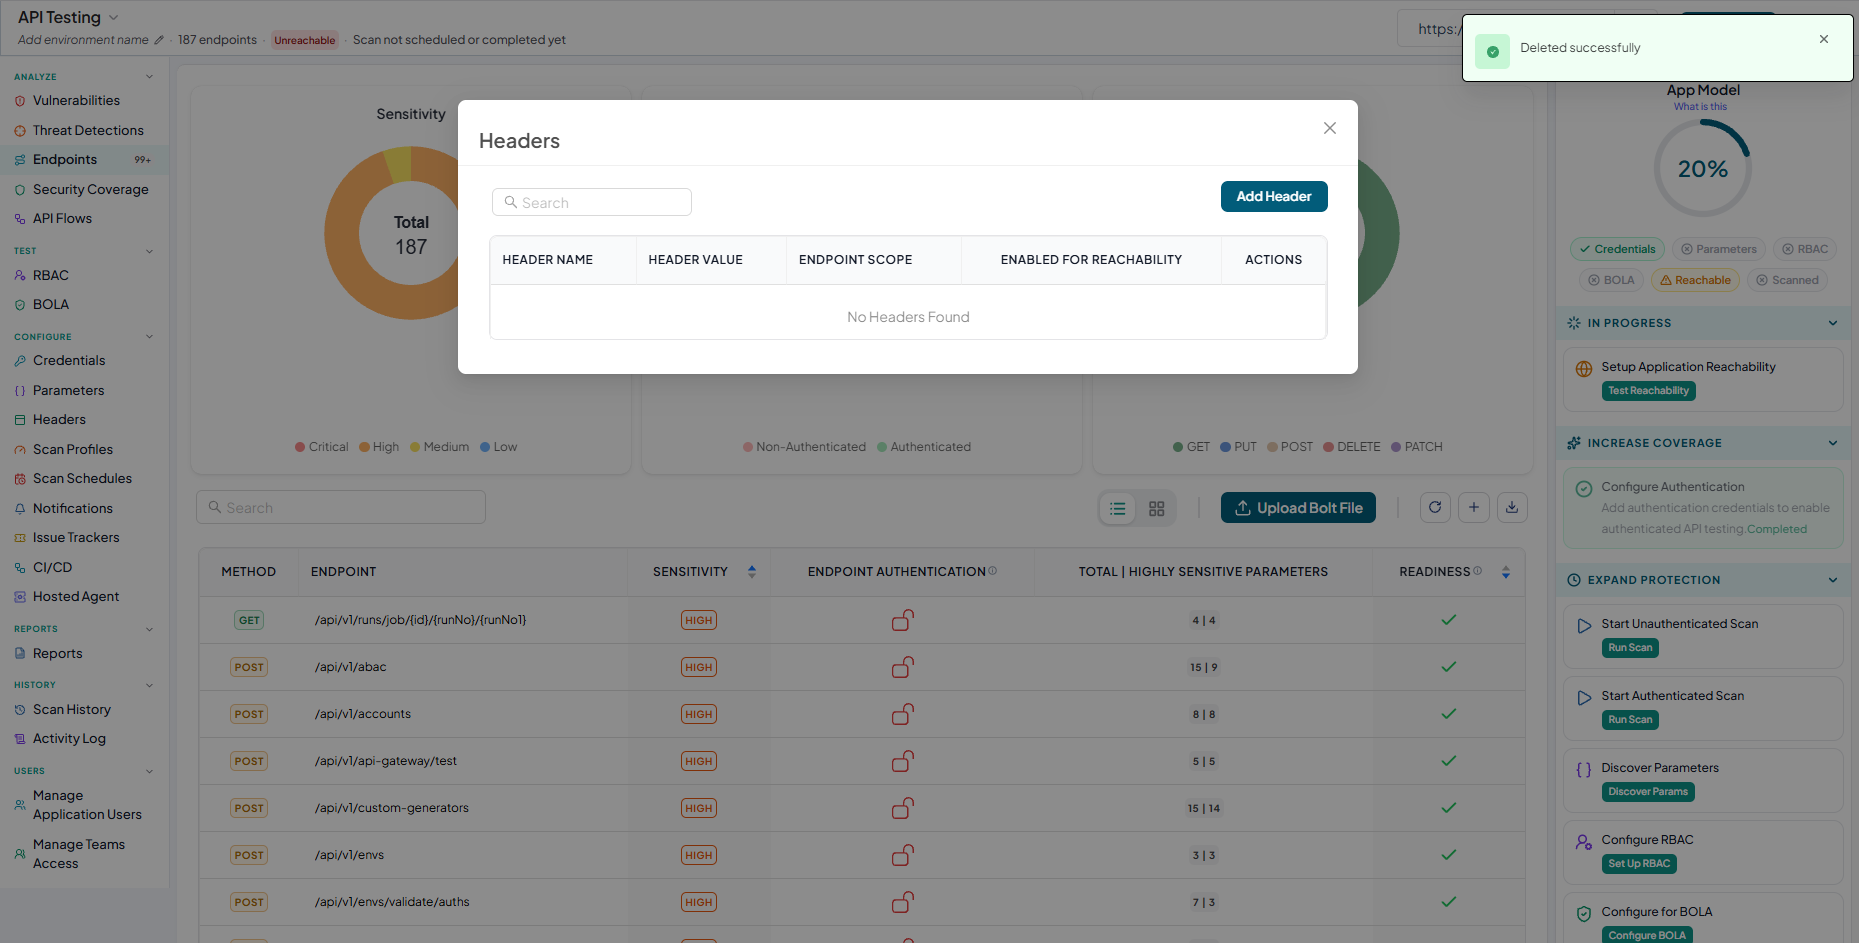
Click Headers.
-
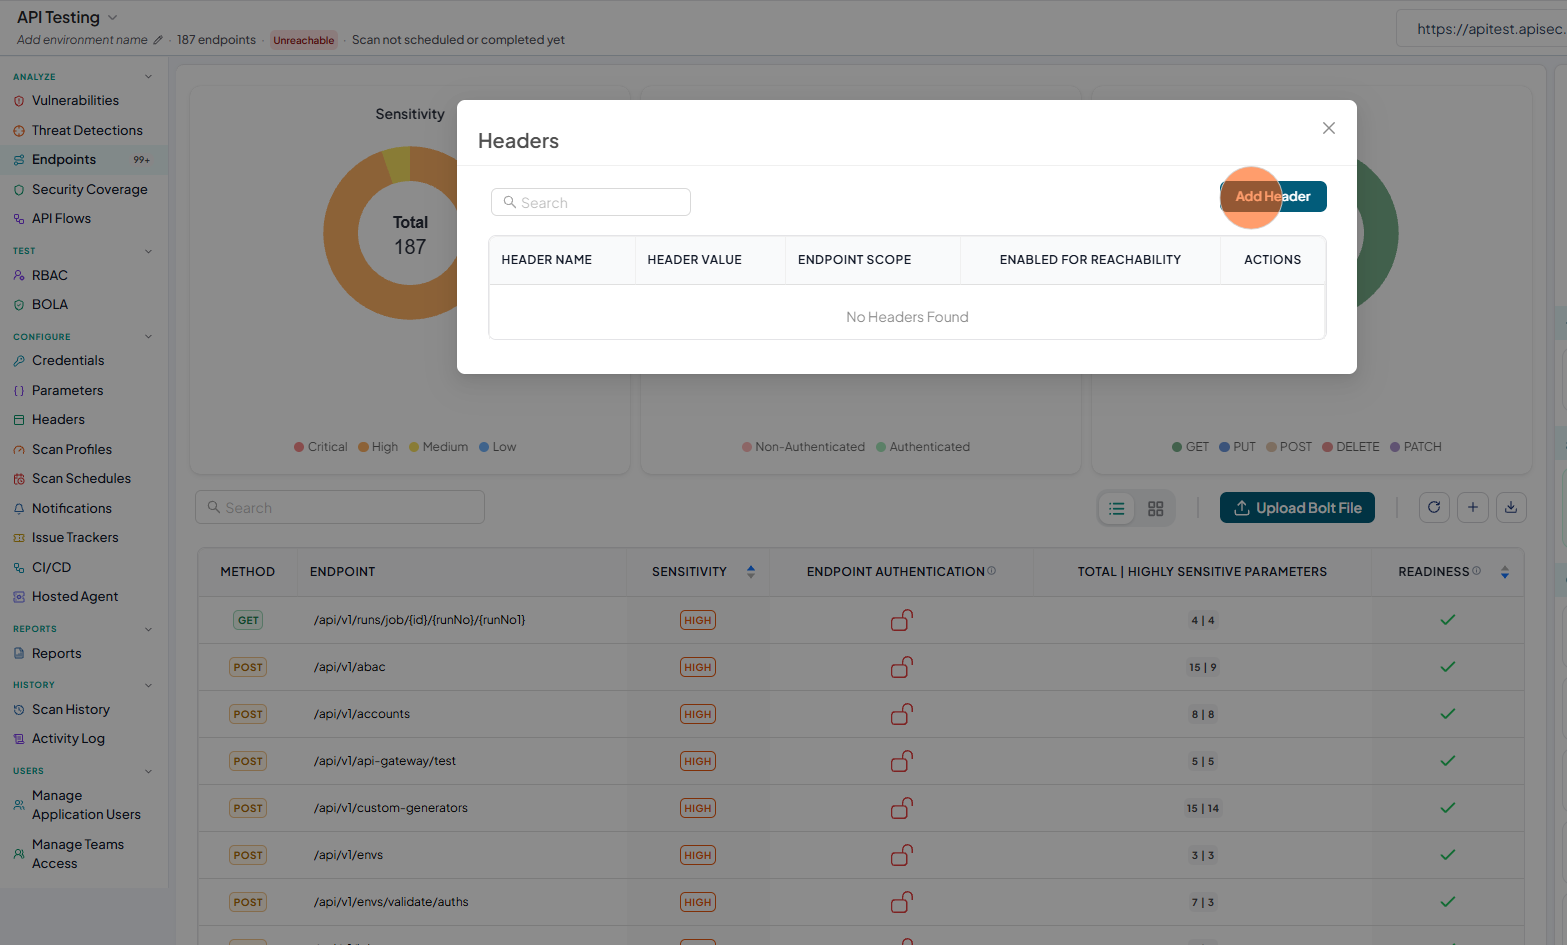
Click Add Headers.
-
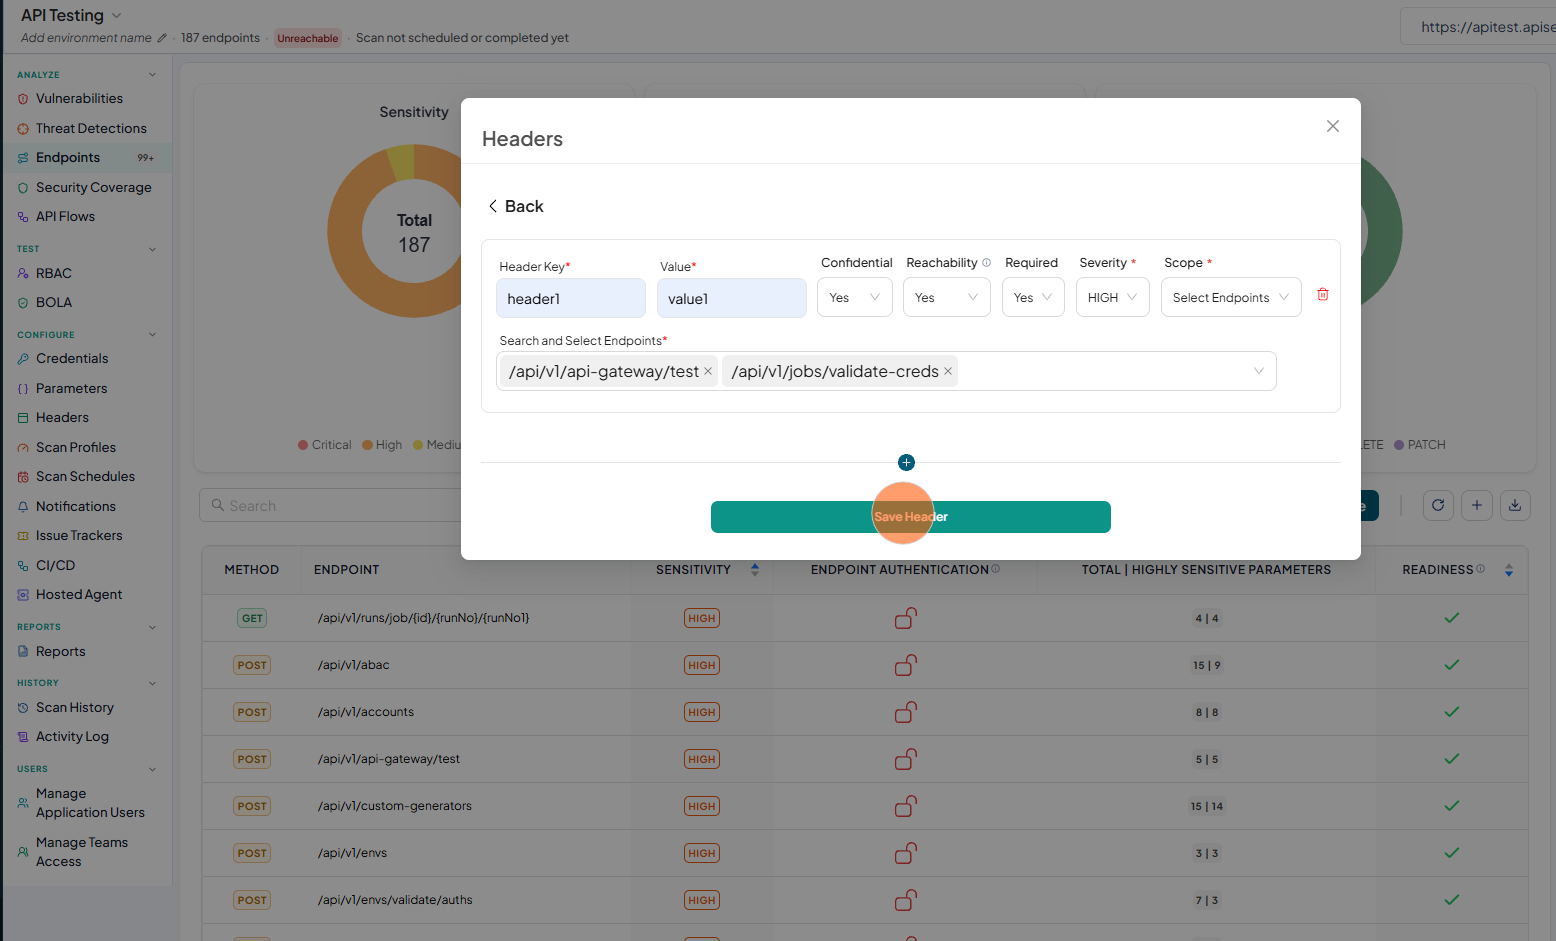
In the form, add the header key and value, select Confidential to hide sensitive values from endpoint details, logs, and other users, set Enable for Reachability to "Yes", select one or more endpoints from the dropdown, and click Save Header.
-
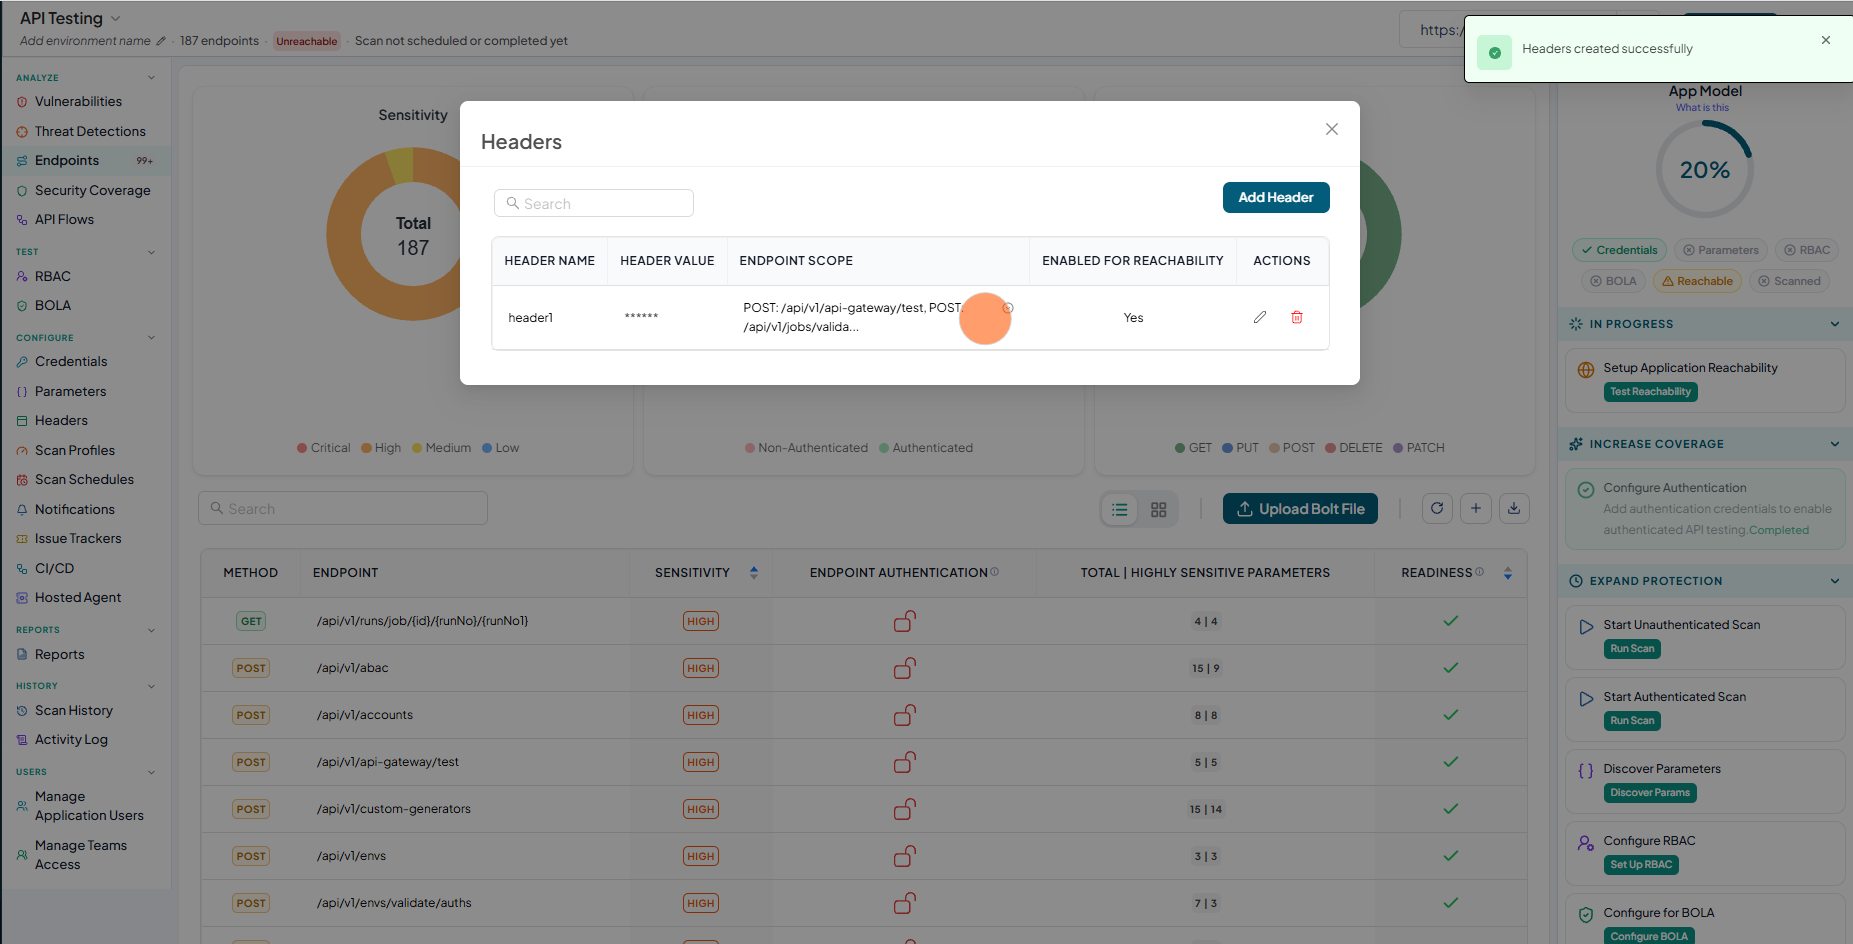
The header is created and appears in the manage headers list.
-
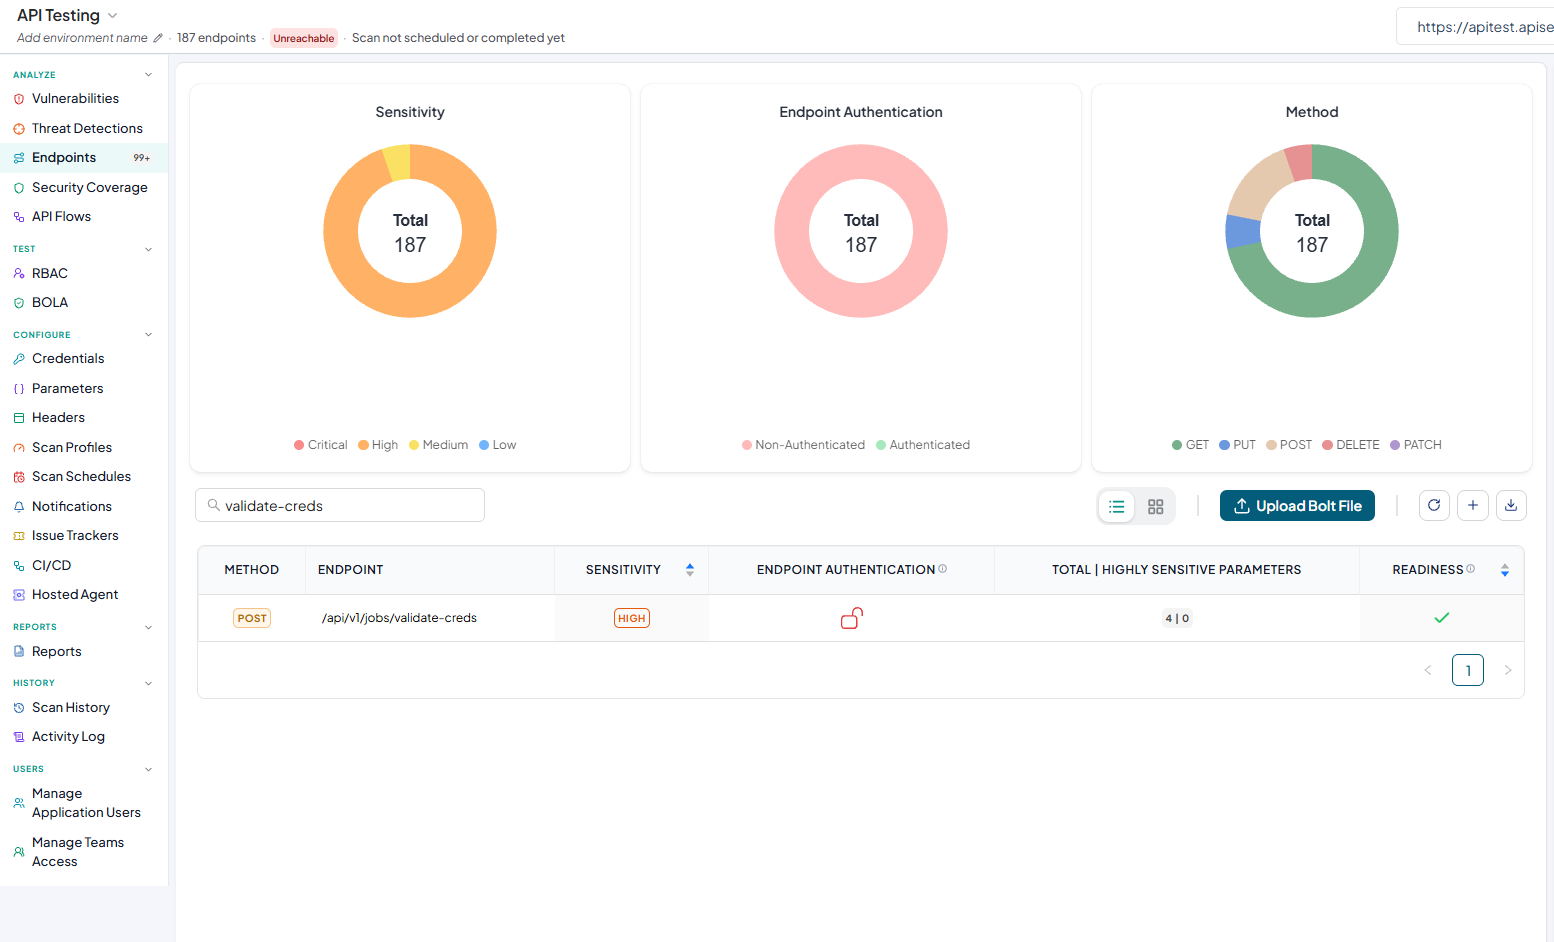
Search for the endpoint in the endpoint search field.
-
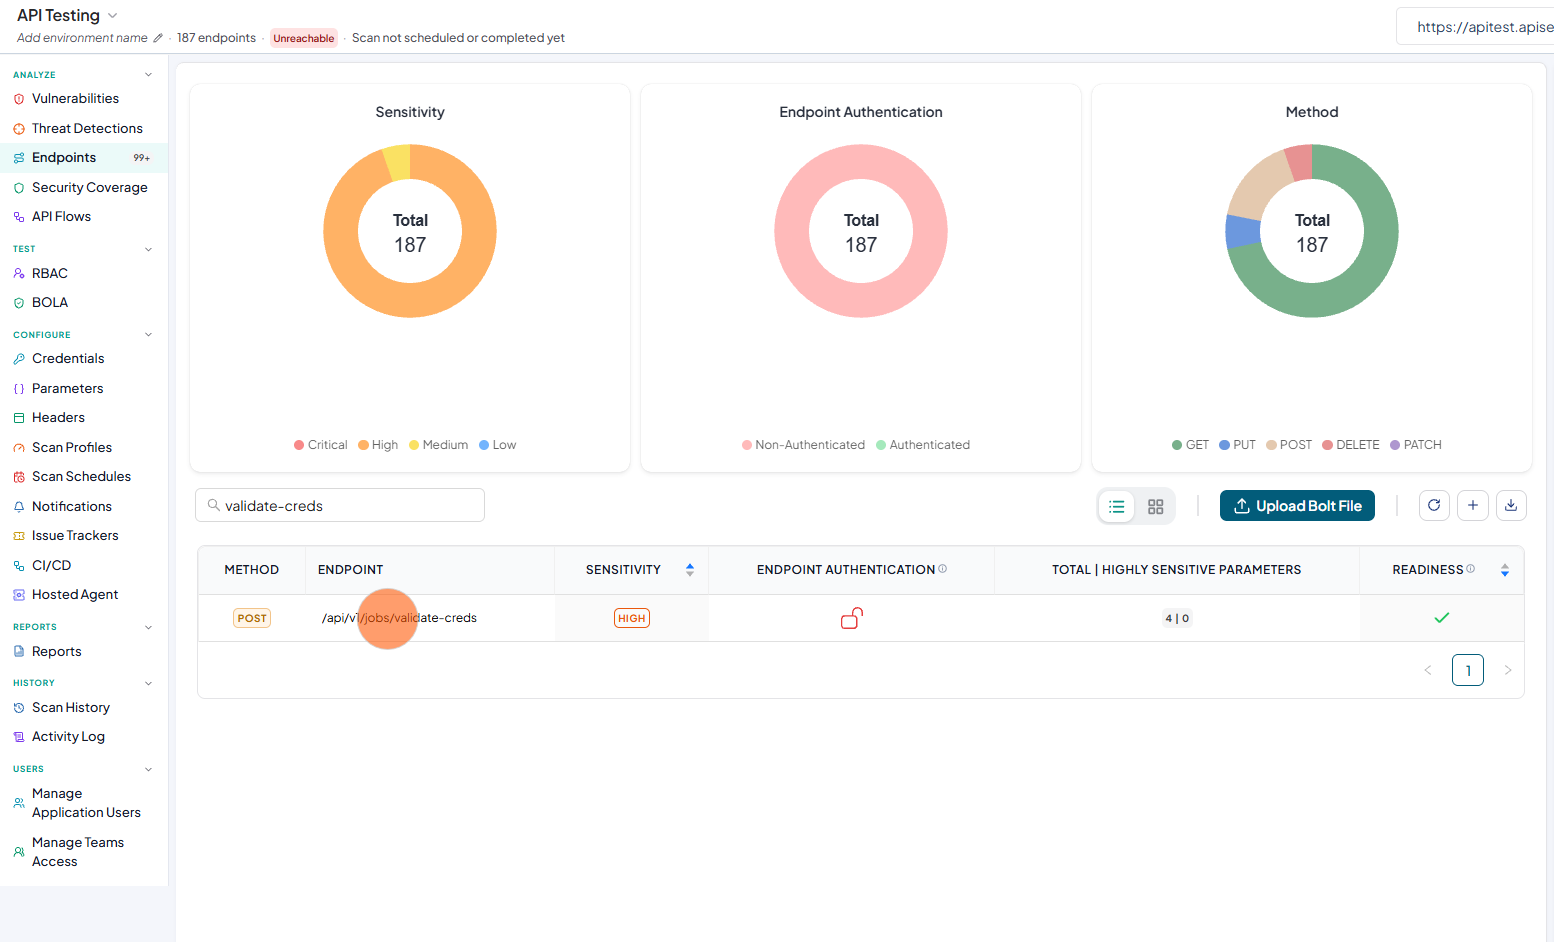
Click an endpoint in the search results to view its details.
-
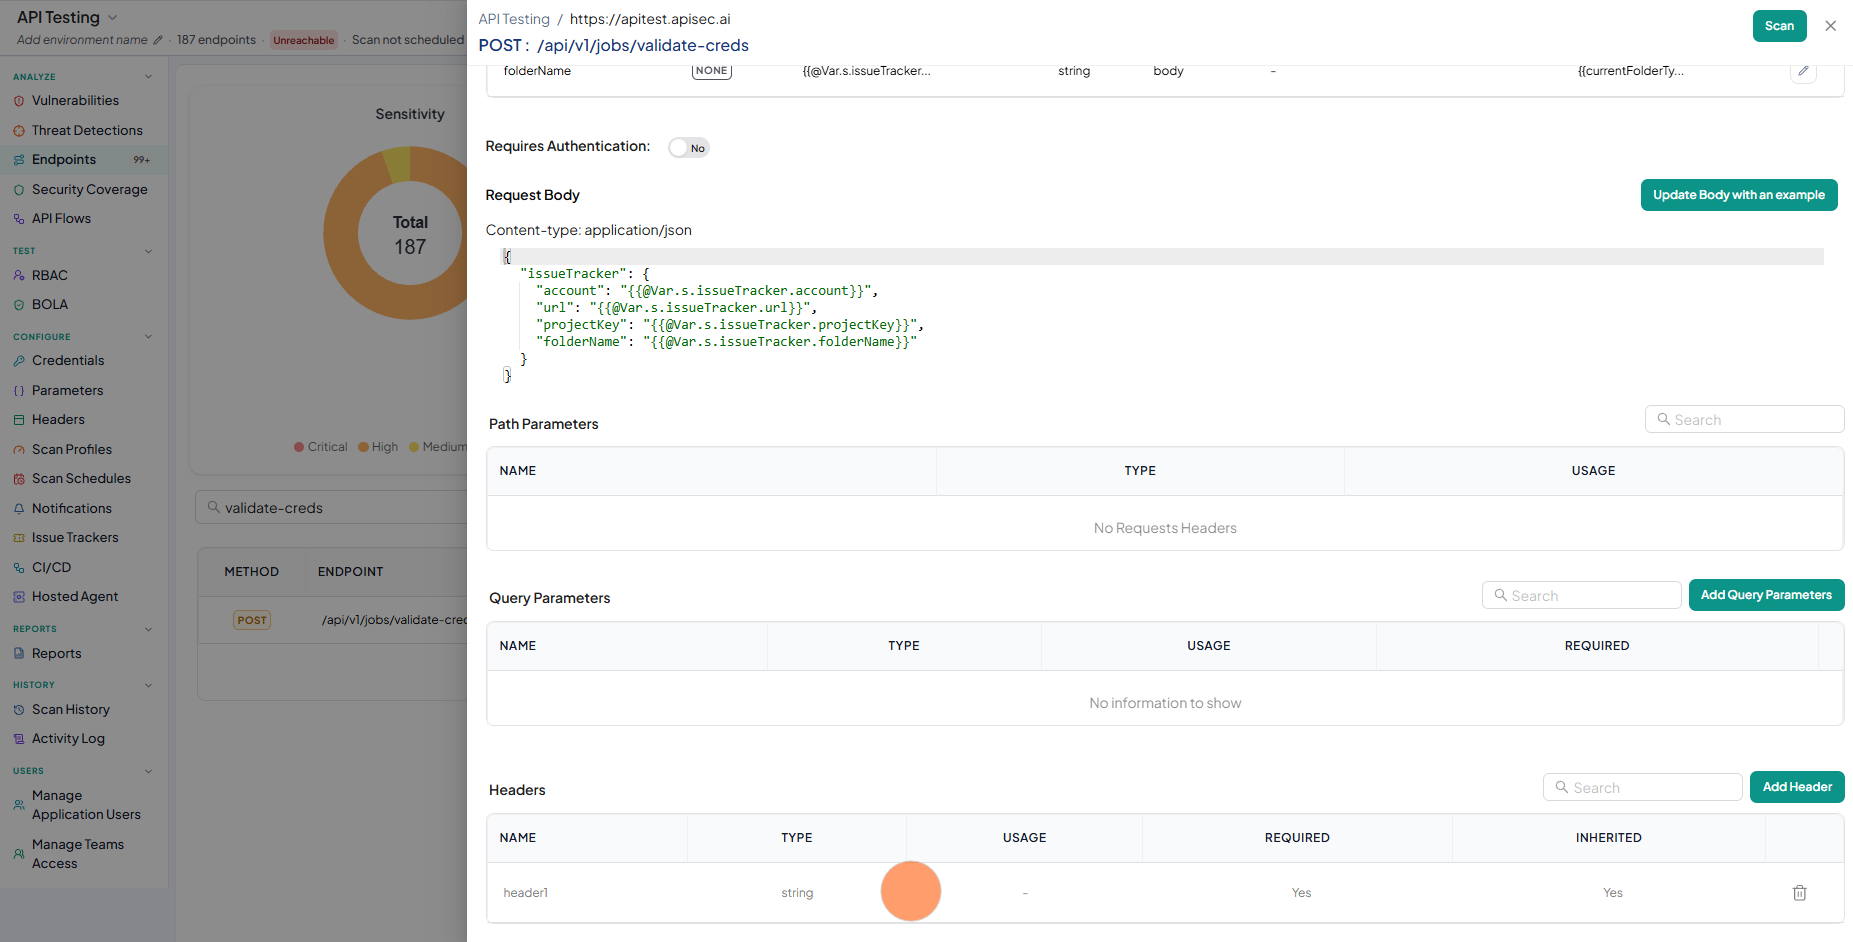
The created header displays in the endpoint details.
-
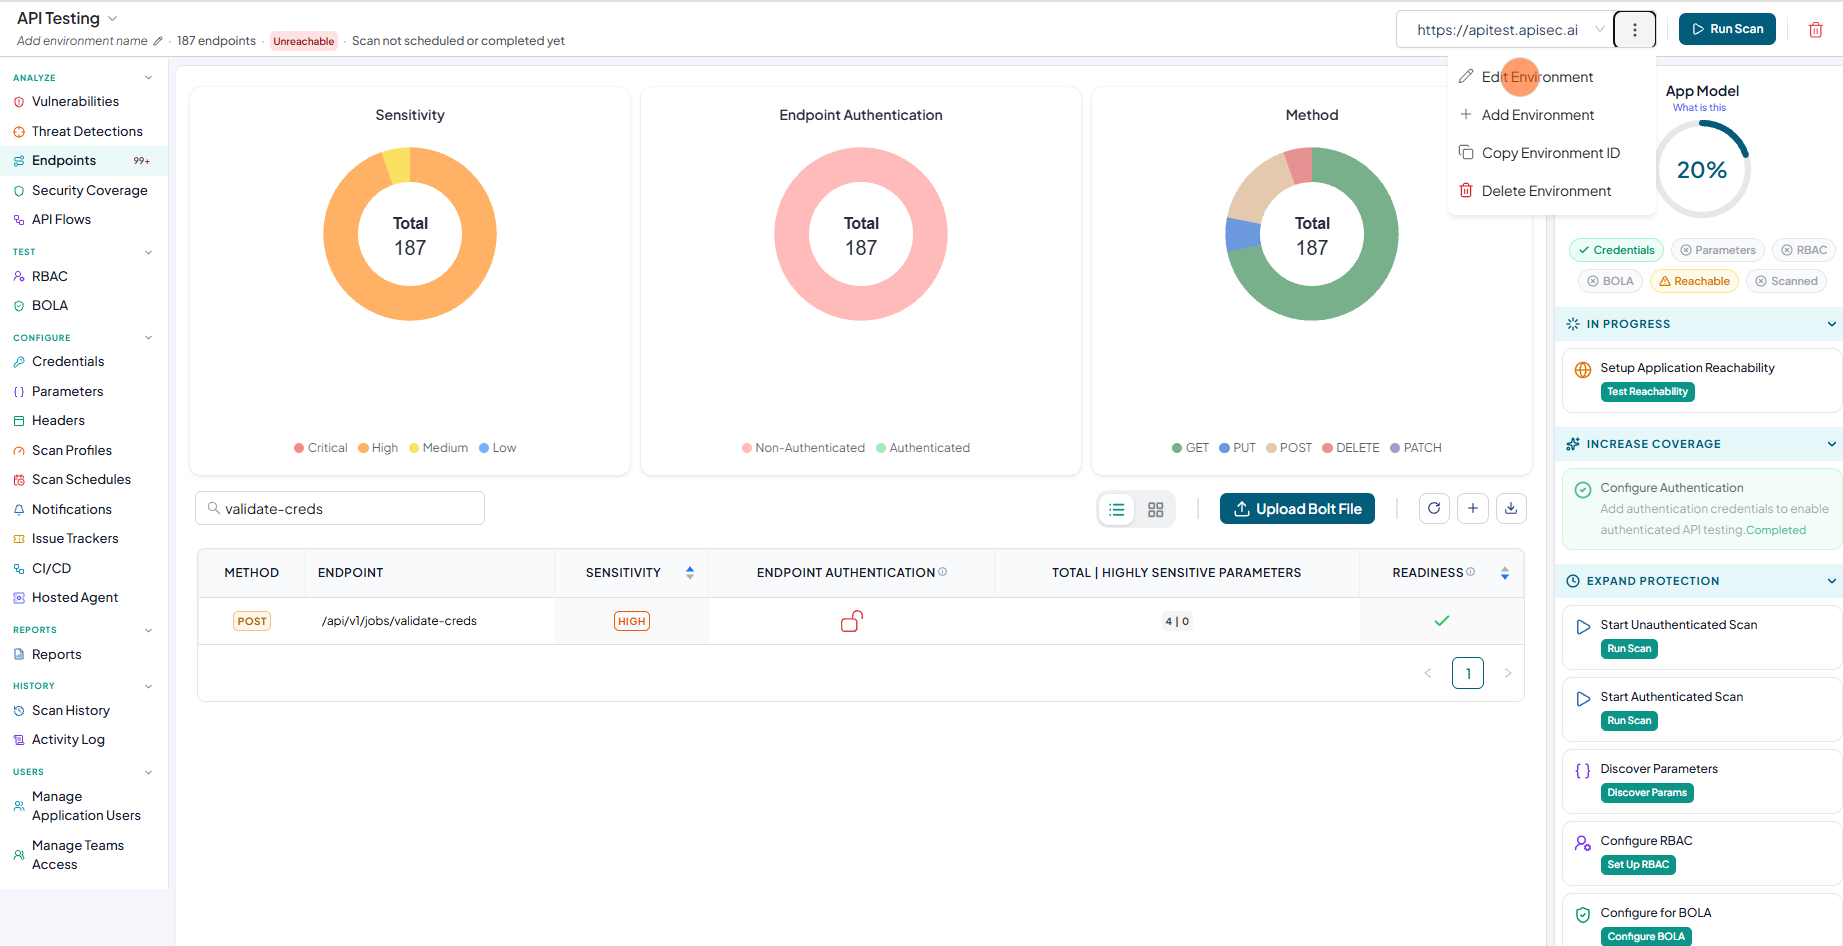
Click the three-dot menu next to the selected environment and choose Edit Environment.
-
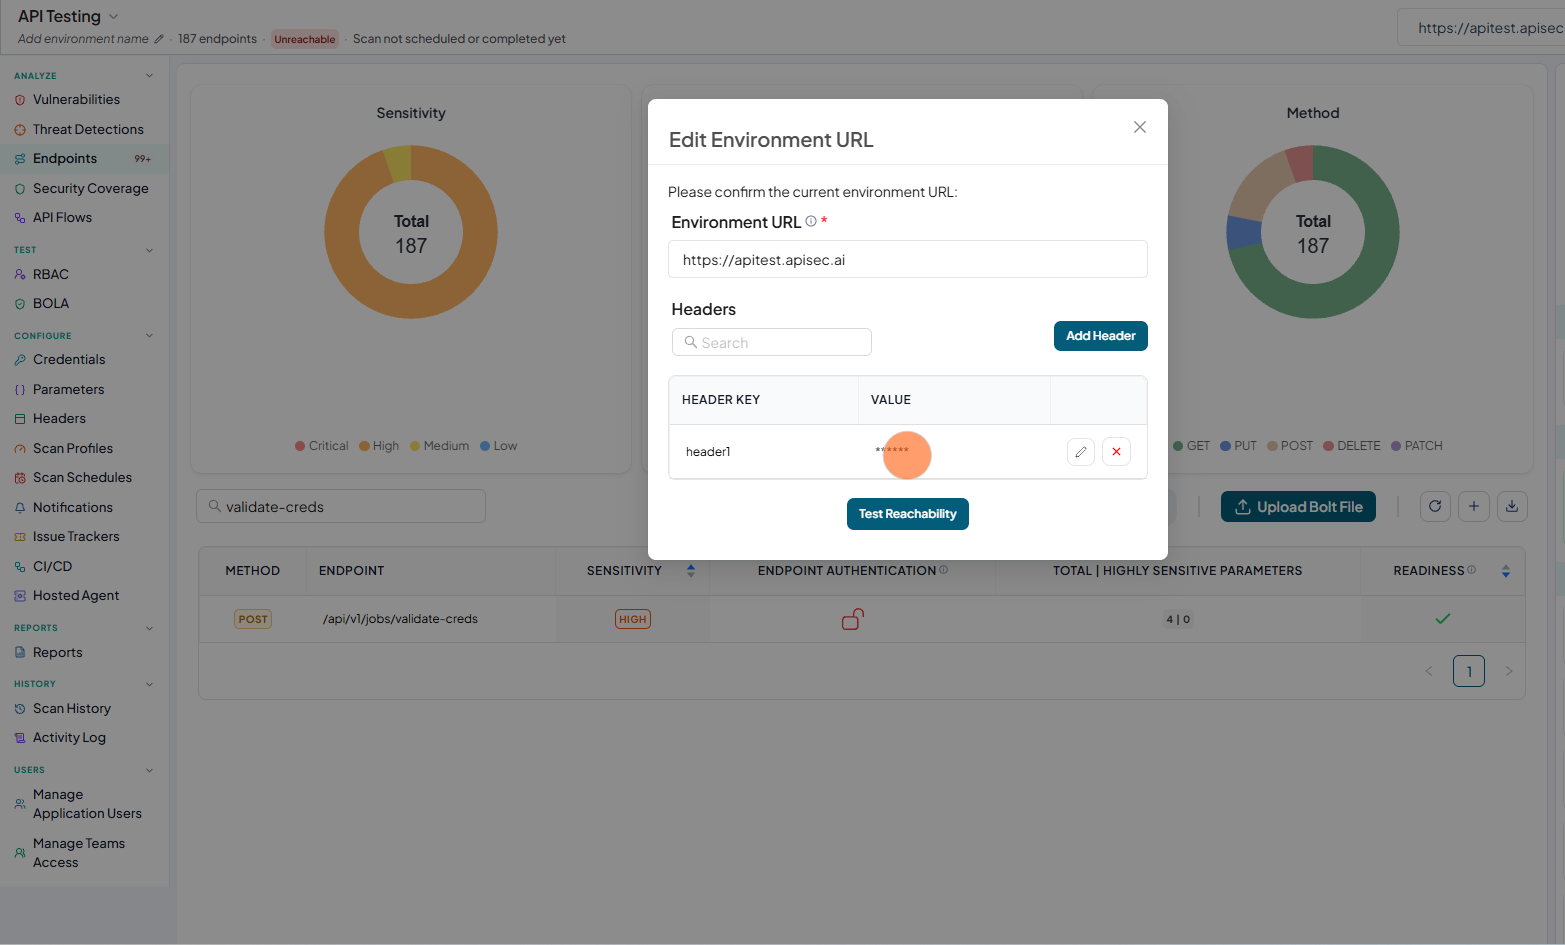
If Enable for Reachability is set to "Yes", the created header displays in the edit instance list.
Edit header
-
Open your browser and visit: https://<your-tenant>.apisecapps.com
-
Click the required application.
-
Click Headers.
-
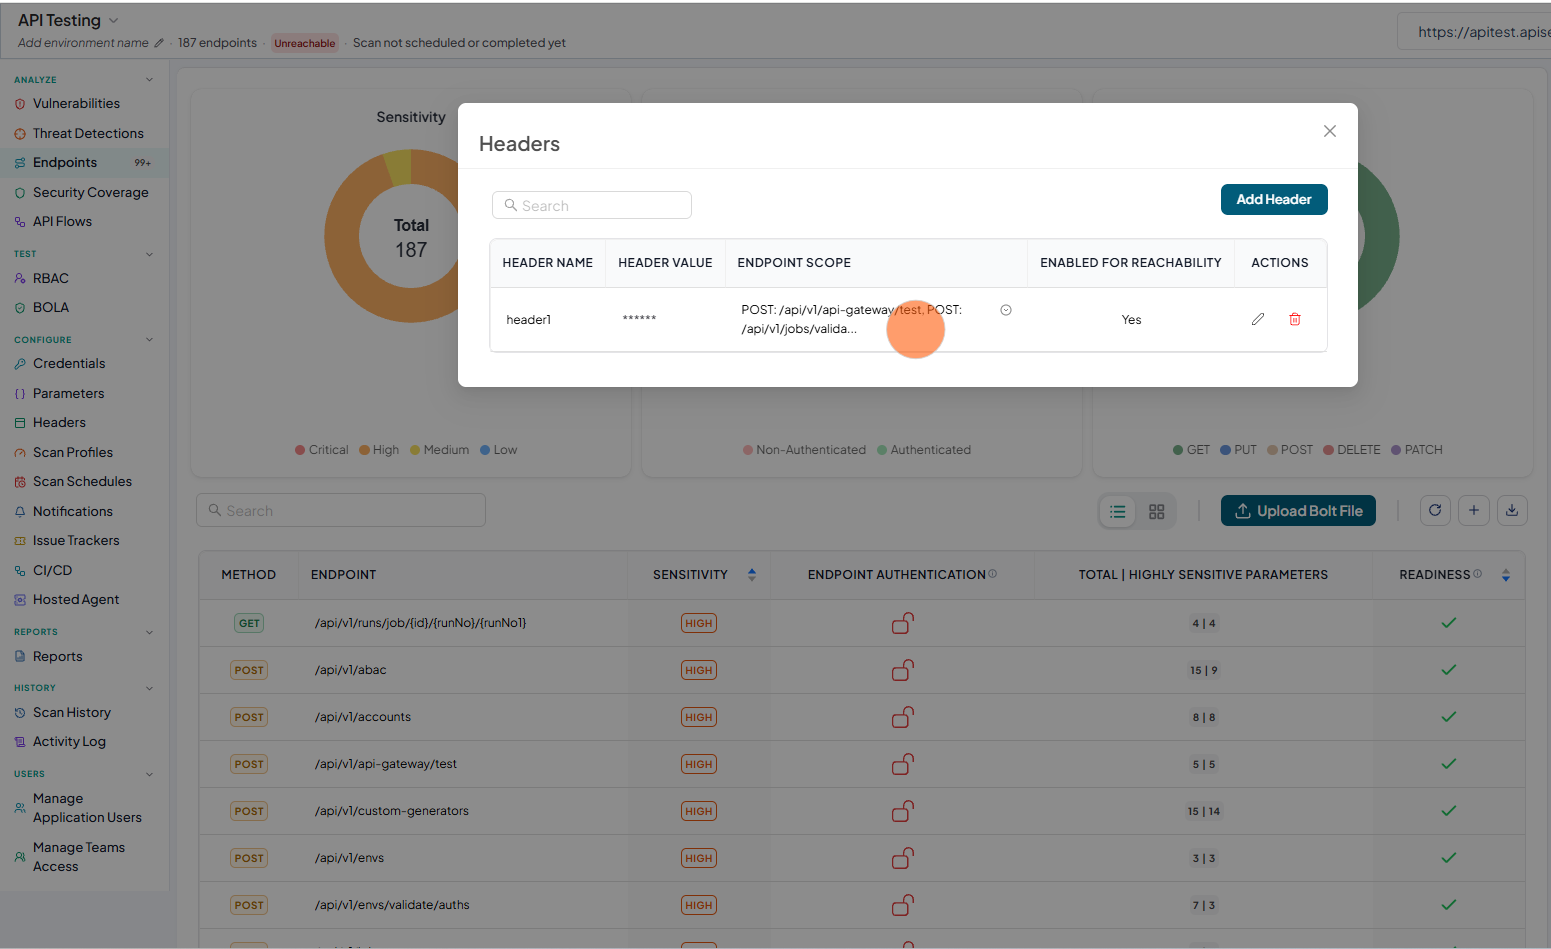
The list of headers displays.
-
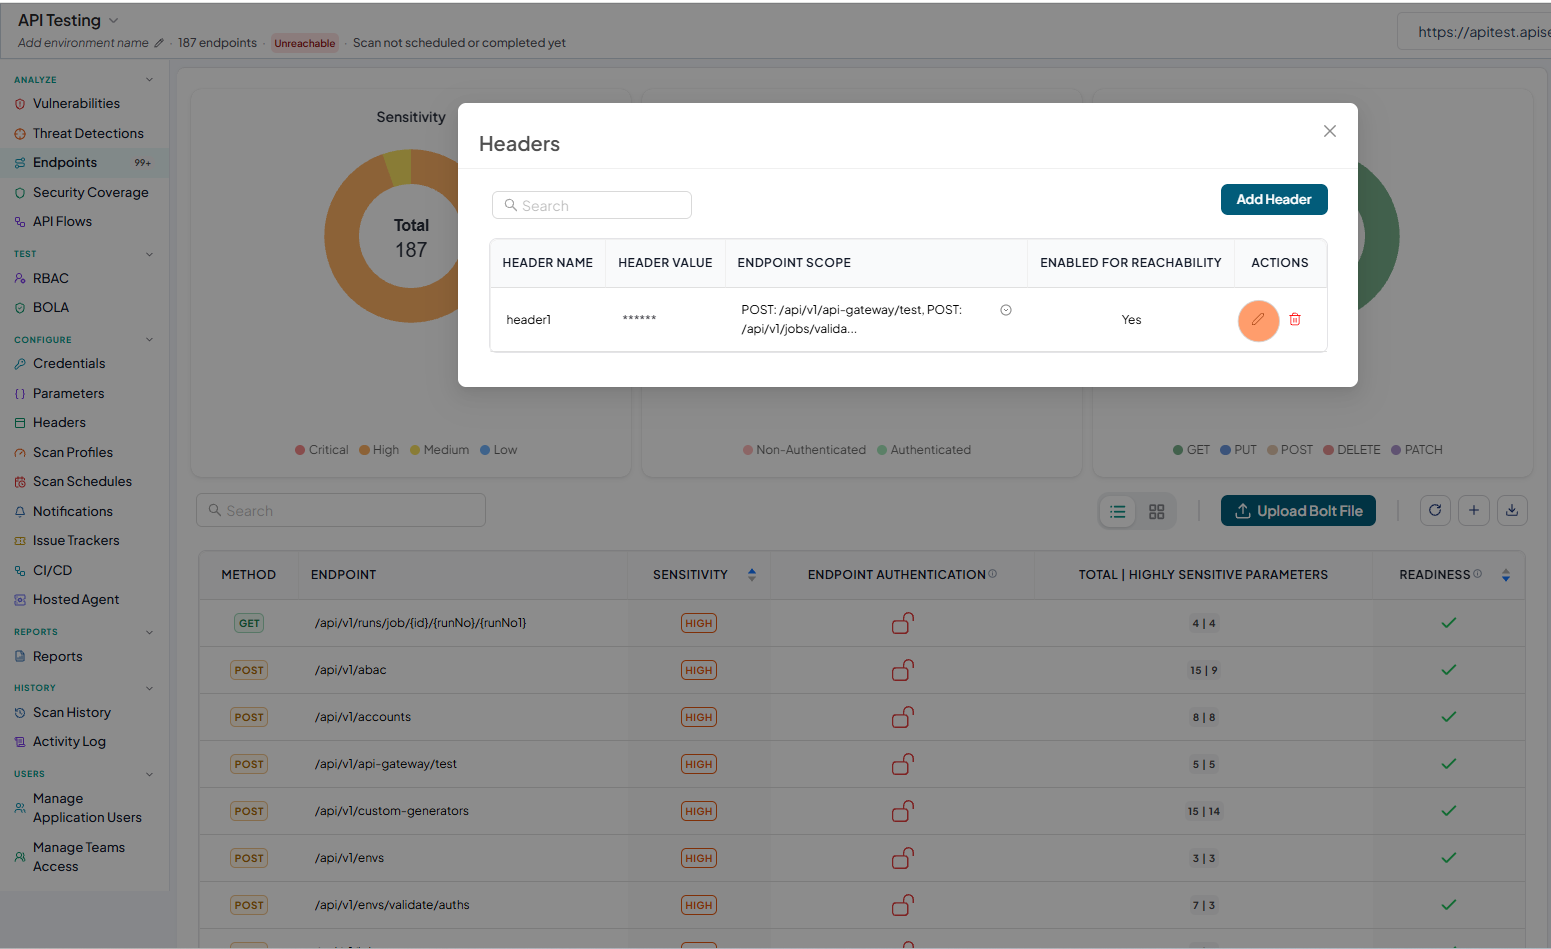
Click the Pencil icon next to the header you want to edit.
-
The header form opens with the header details.
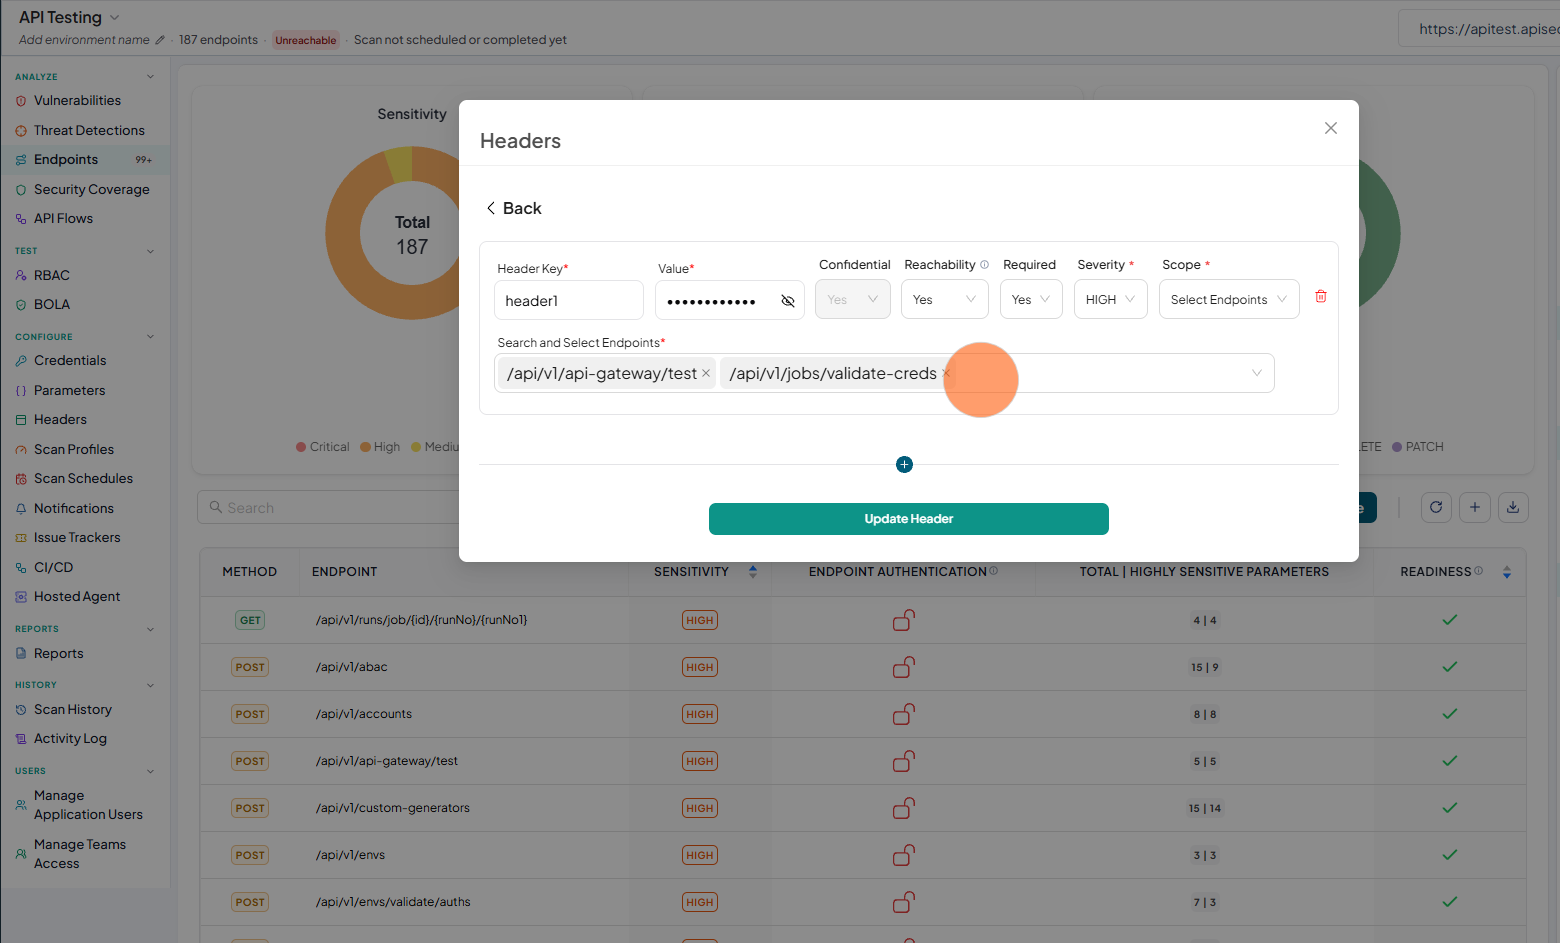
-
Change the Header Key, value, and other fields as needed, then click Update header.
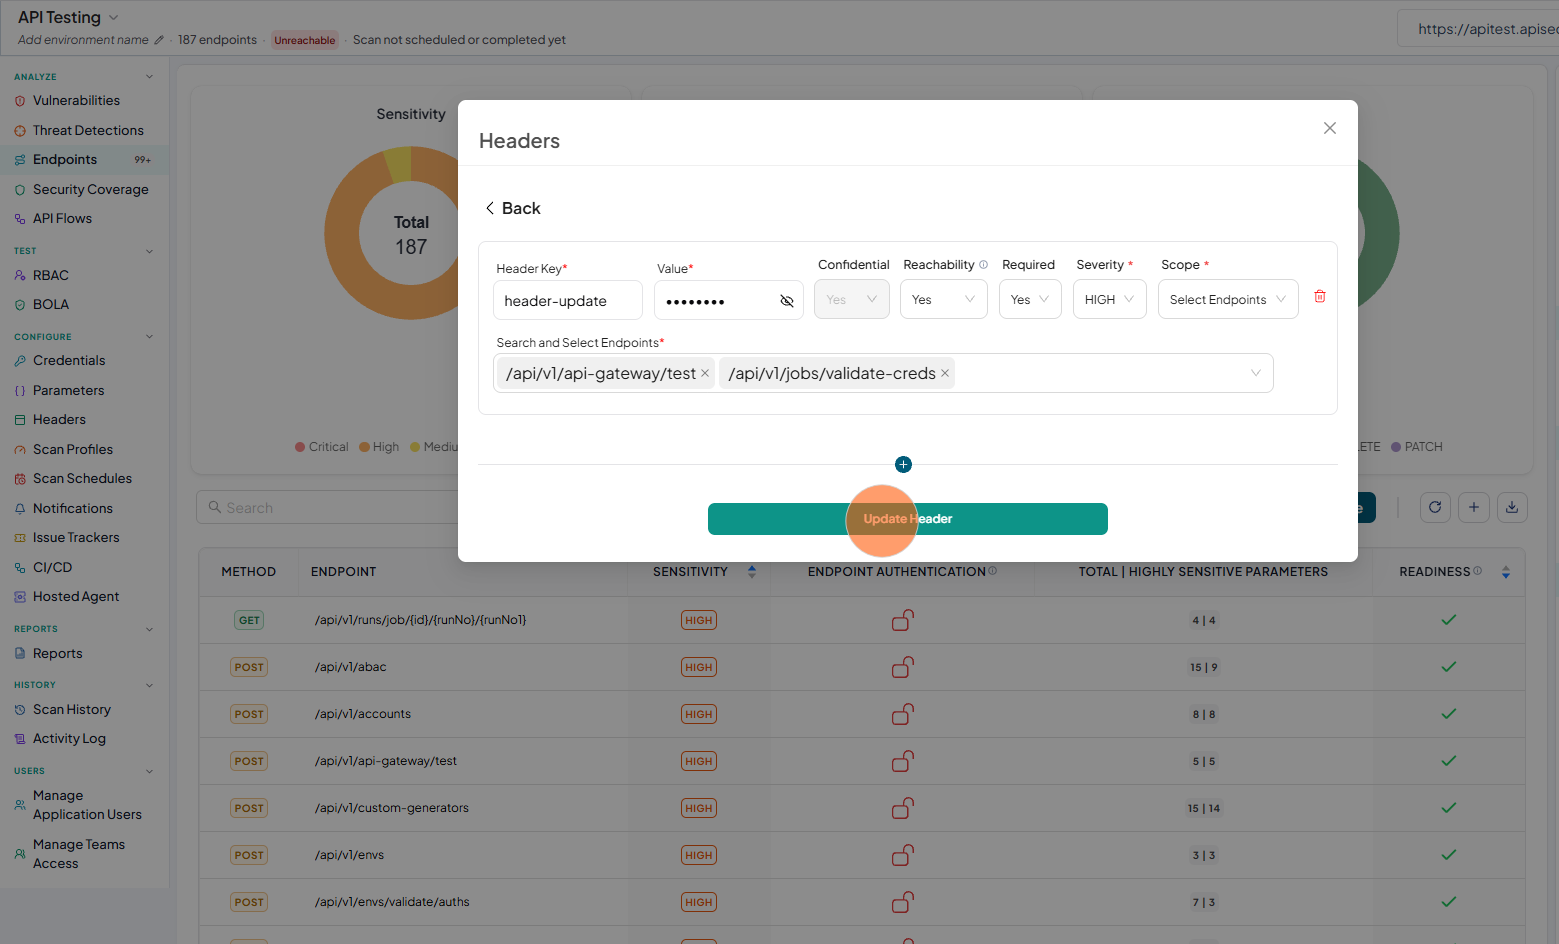
Delete header
-
Open your browser and visit: https://<your-tenant>.apisecapps.com
-
Click the required application.
-
Click Headers.
-
The list of headers displays.
-
Click the Delete icon next to the header you want to delete.
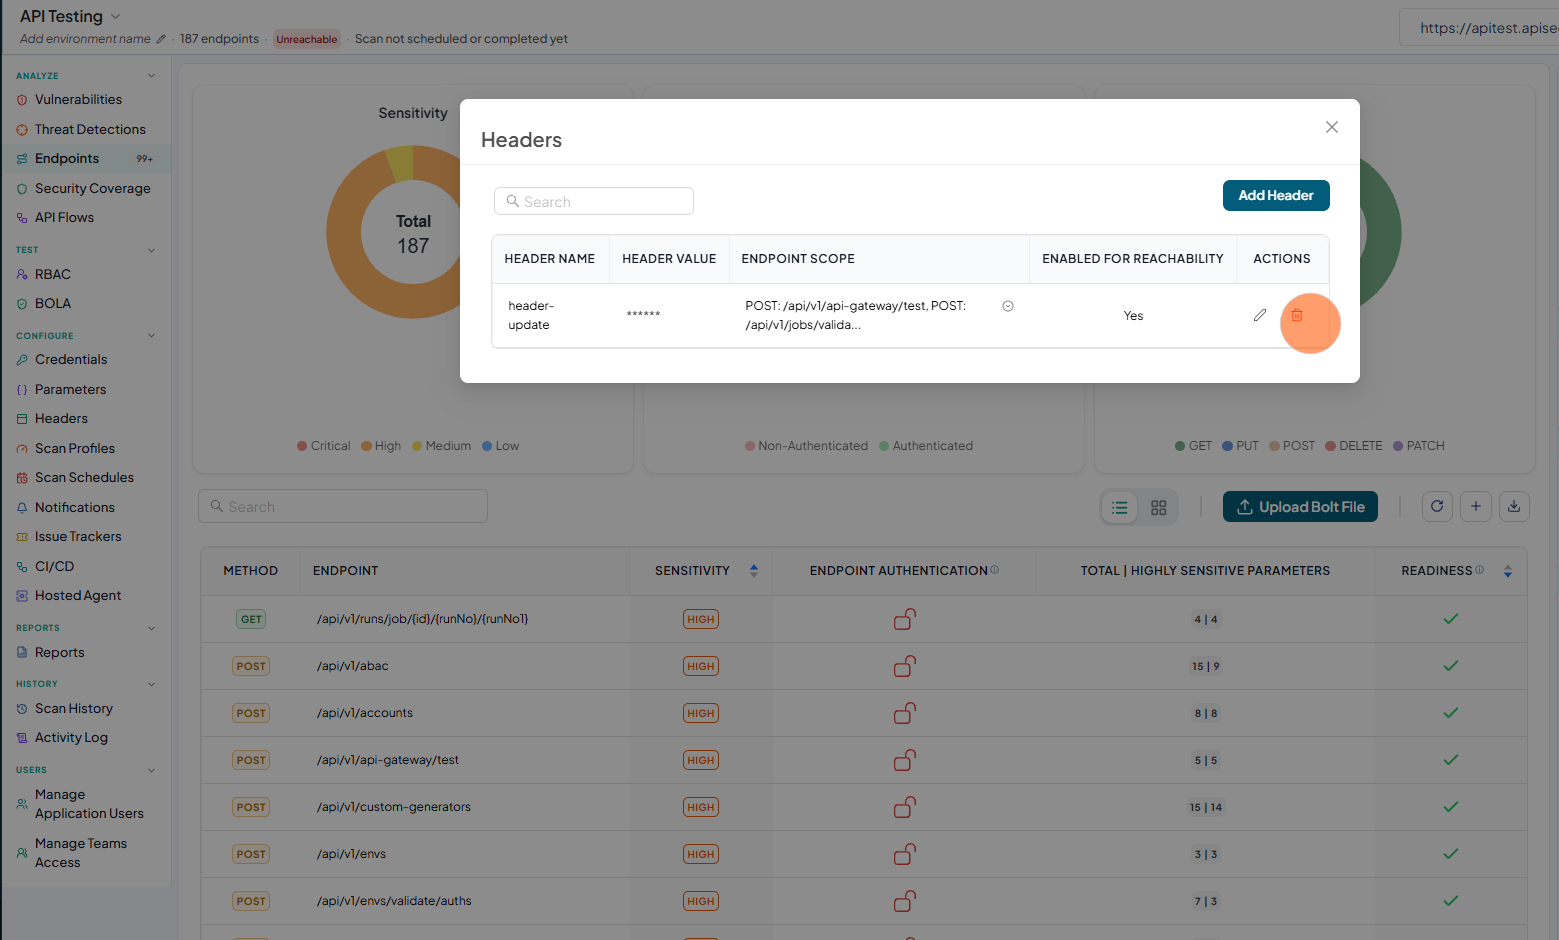
-
Click Delete to confirm.
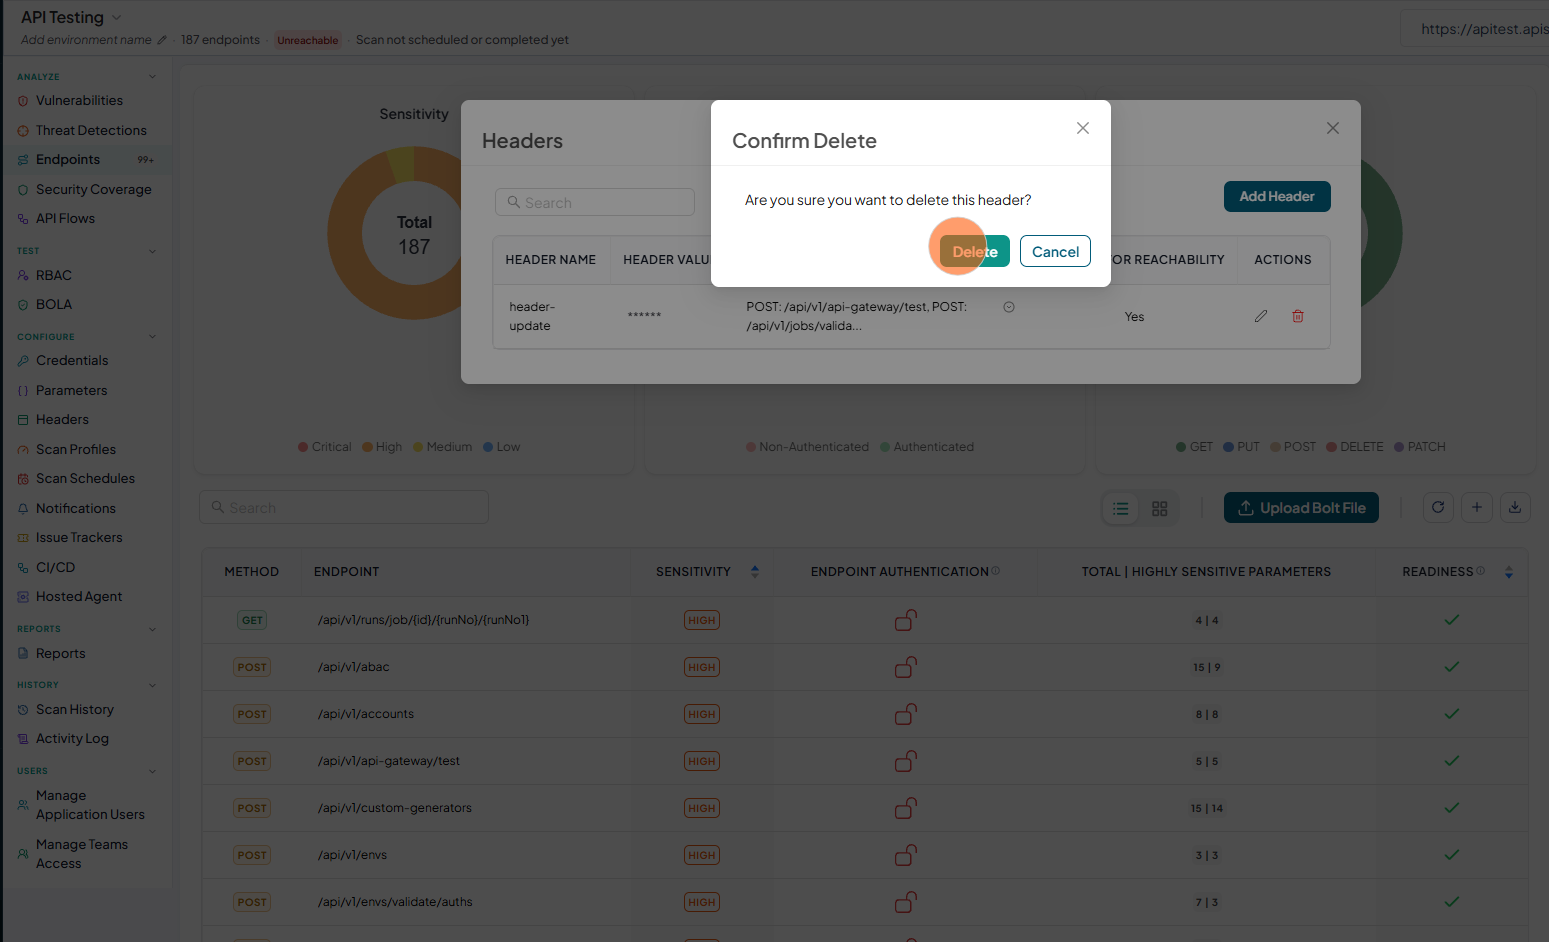
-
The header is deleted.
Users with the View role cannot add, edit, or delete headers in a shared application.