Viewing and understanding vulnerabilities
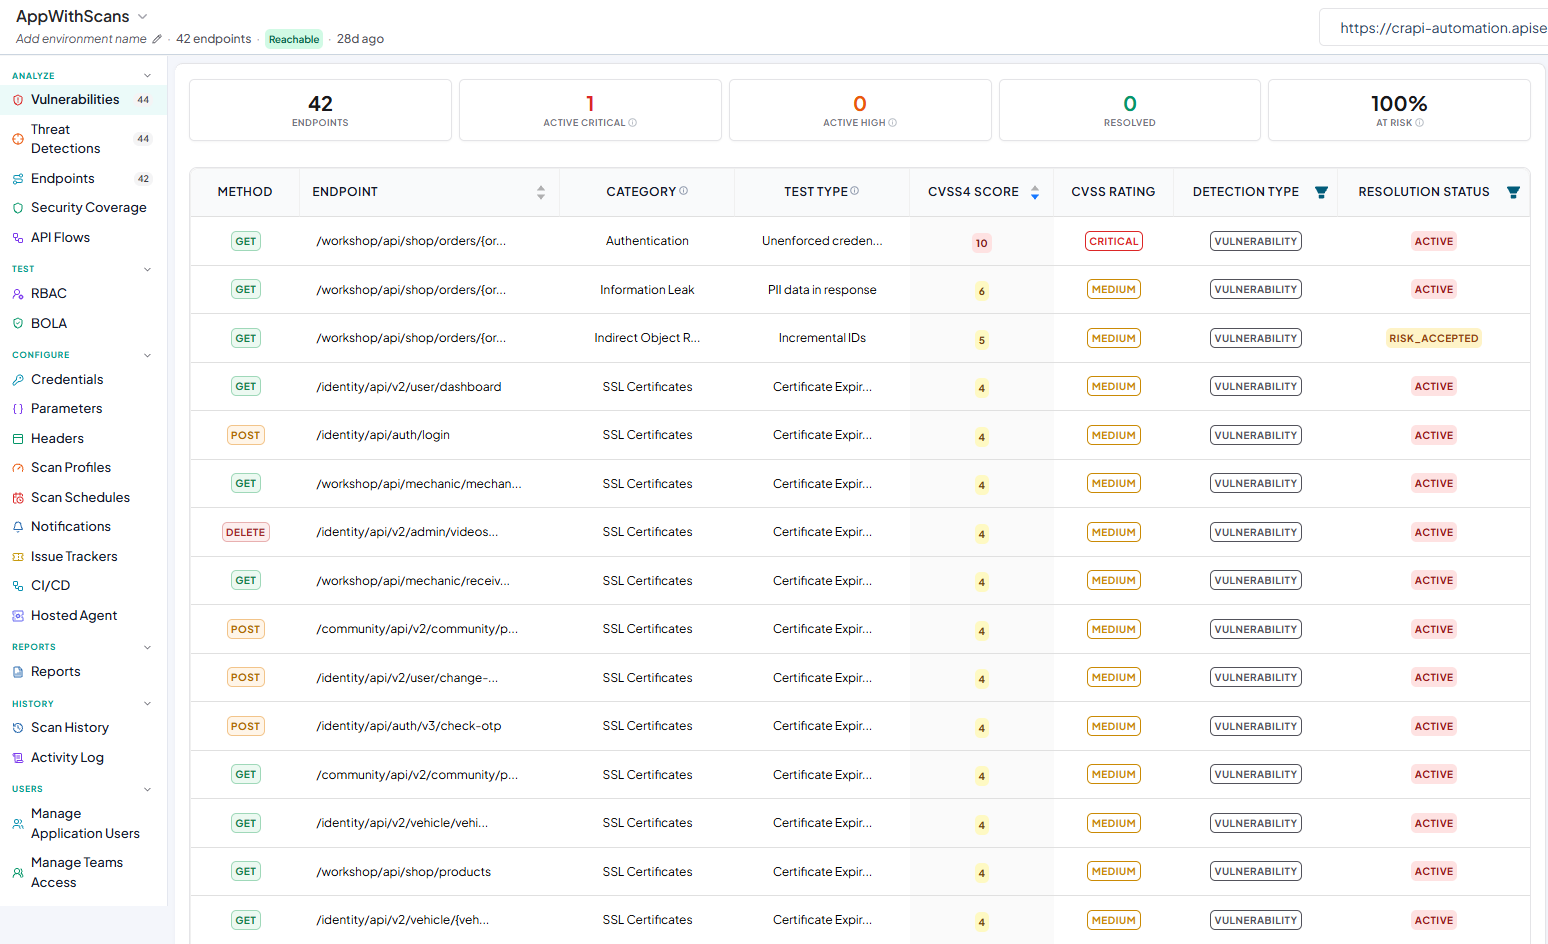
The Vulnerabilities tab shows every security issue an APIsec scan discovers for an application, so you can prioritize remediation by severity and track your security posture over time. Each finding links to the affected endpoint and includes the context you need to reproduce, fix, and verify it — category, test type, CVSS score, and resolution status. Use this page to review findings, drill into their details, and re-scan to confirm a fix.
What's on this page
- Severity charts: Vulnerabilities by Severity categorizes findings as Critical, High, Medium, or Low. Active Vulnerabilities - Daily Trend charts active vulnerabilities over time so you can track posture changes.
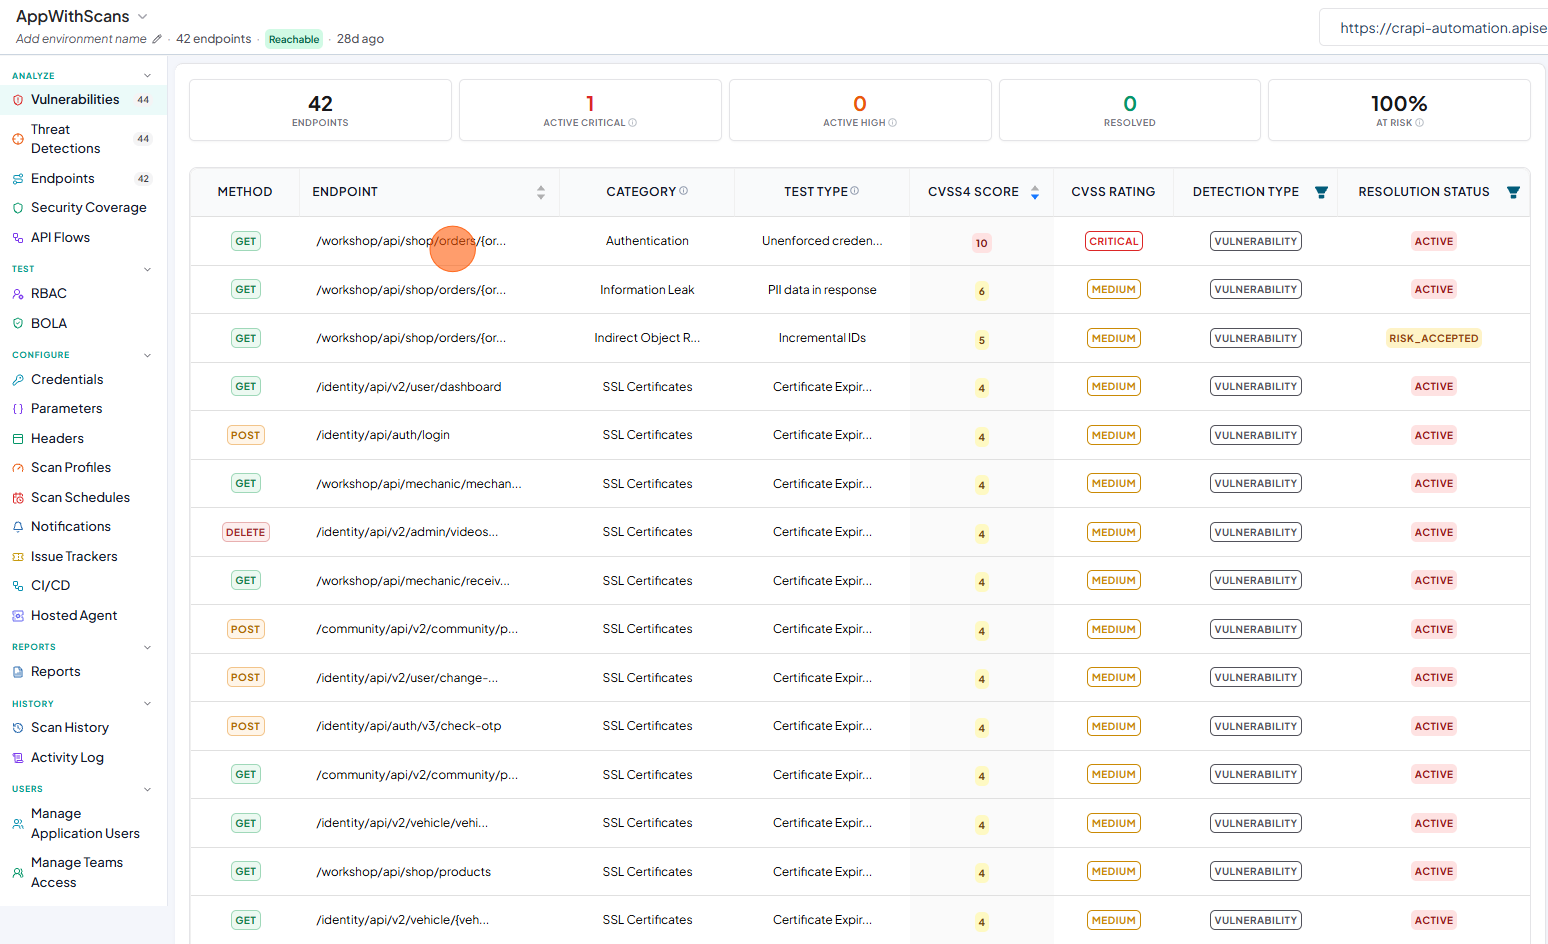
- Vulnerability table: Each row shows the HTTP method and endpoint where the issue exists, a category (such as Authentication, Authorization, Response Headers, or Input Validation), the test type that detected the issue (for example, missing tokens, misconfigured headers, or broken access controls), a CVSS score to guide remediation priority, and the resolution status —
ACTIVE,RESOLVED,FALSE_POSITIVE, orRISK_ACCEPTED.
Review vulnerabilities
This guide assumes you have already set up the app and performed either an Unauthenticated Scan or an Authenticated Scan. The APIsec scan identifies the vulnerabilities for you.
-
In your browser, go to https://<your-tenant>.apisecapps.com.
-
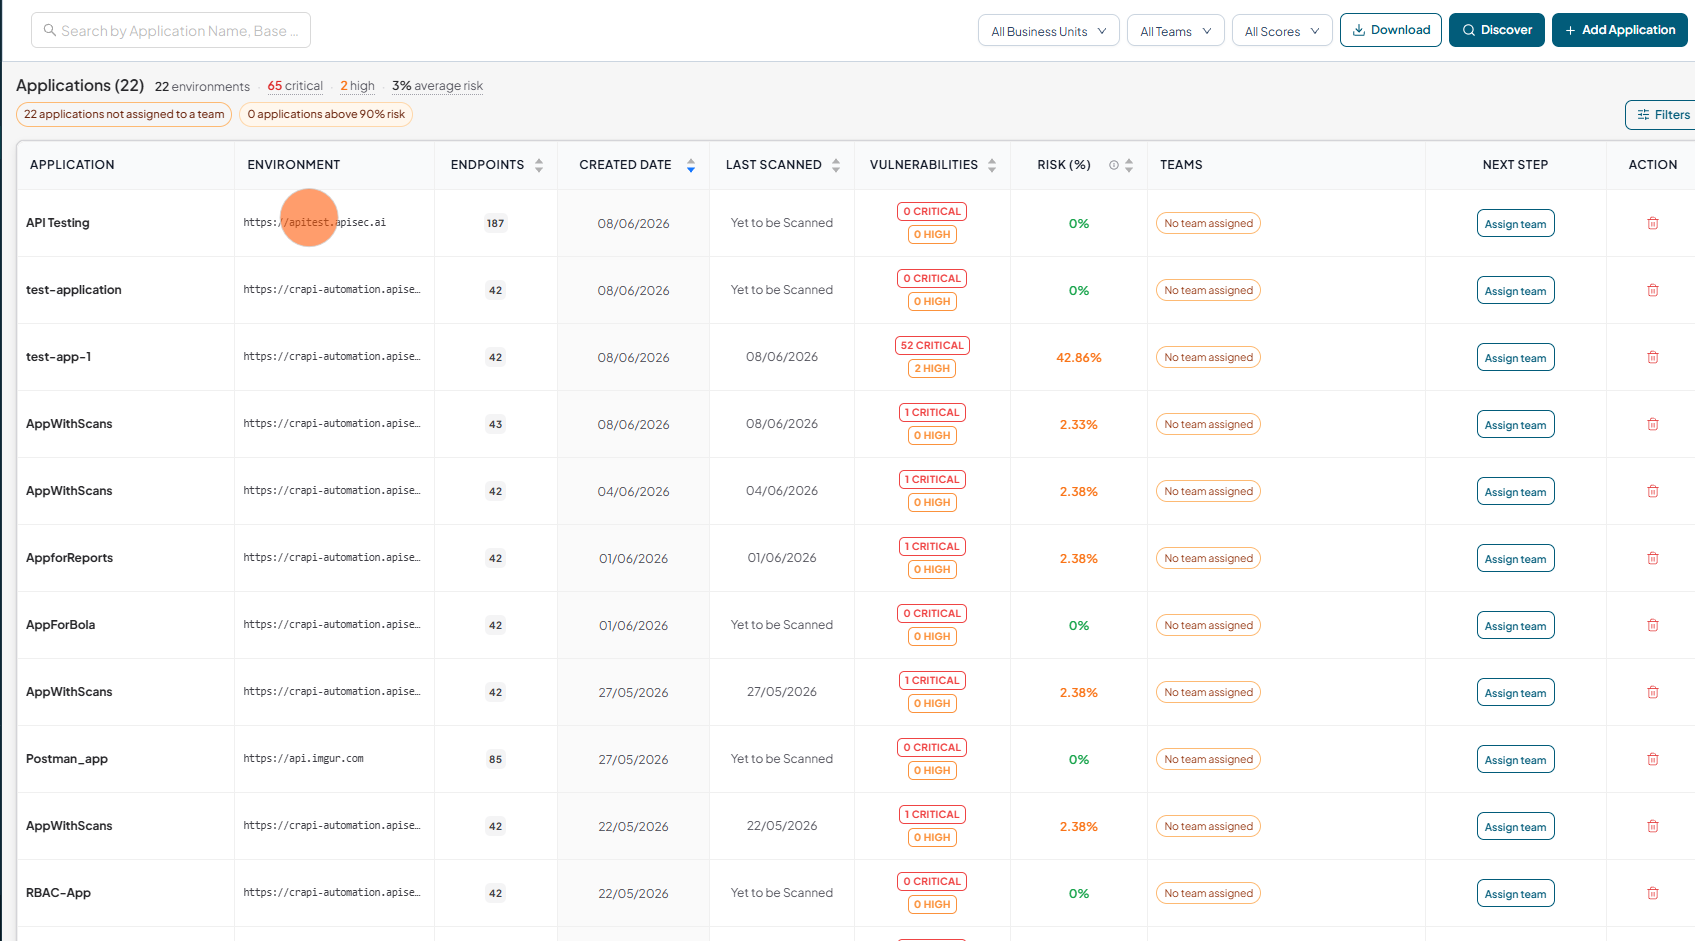
Click the required application.
-
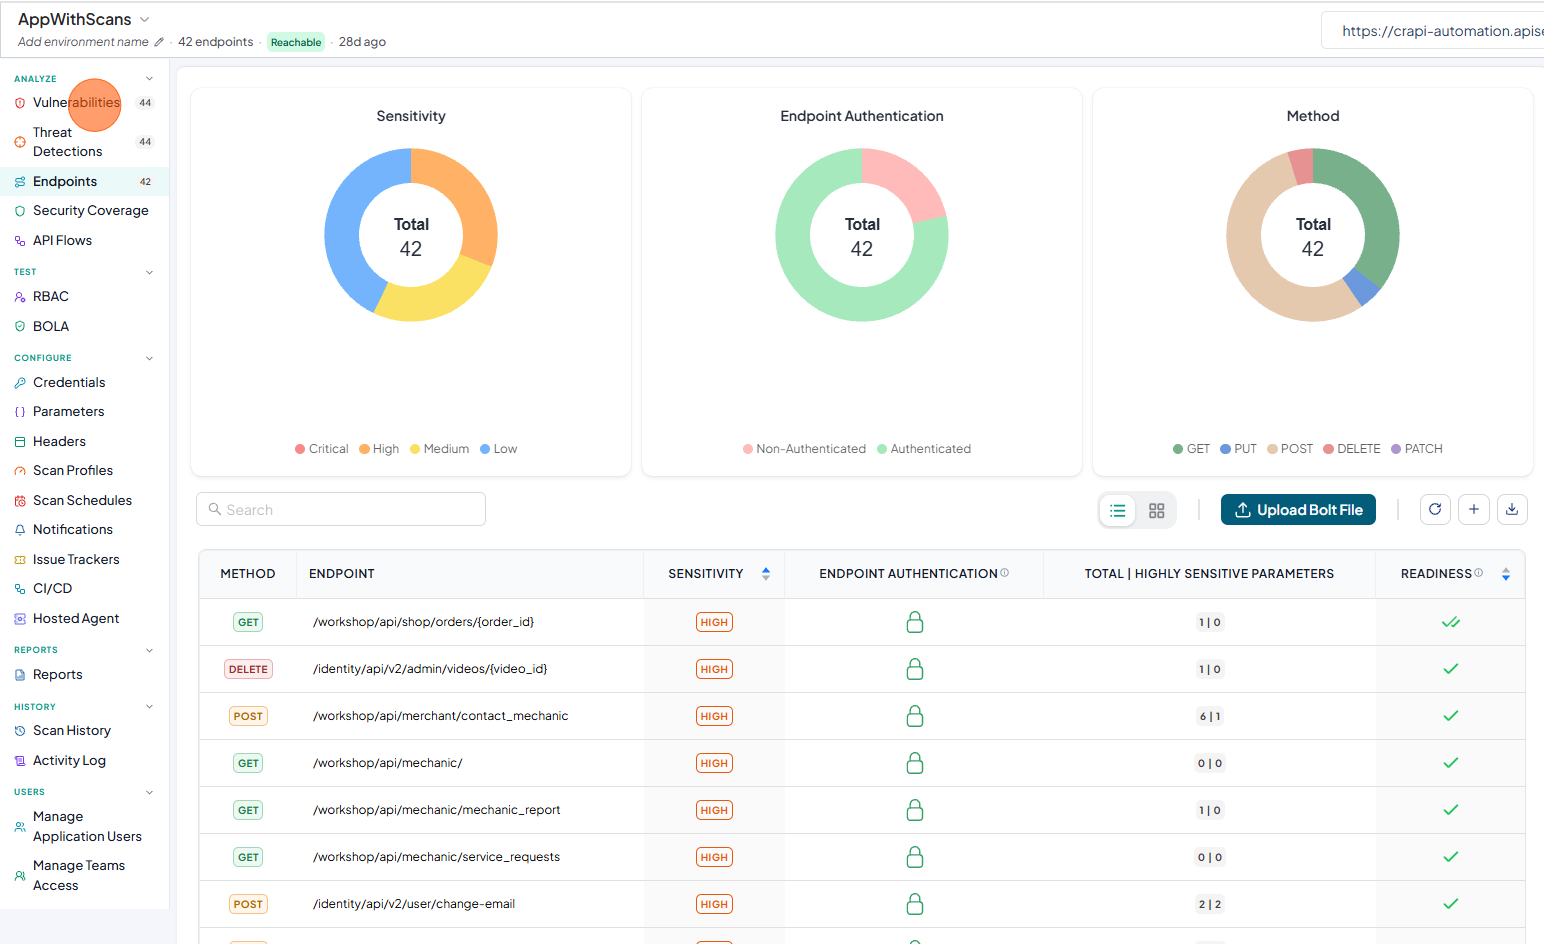
Click the Vulnerabilities tab.
The tab shows the vulnerabilities discovered by the APIsec scan, including the Vulnerabilities by Severity and Active Vulnerabilities - Daily Trend charts comparing Critical, High, Medium, and Low severity vulnerabilities identified during the scan.
View vulnerability details
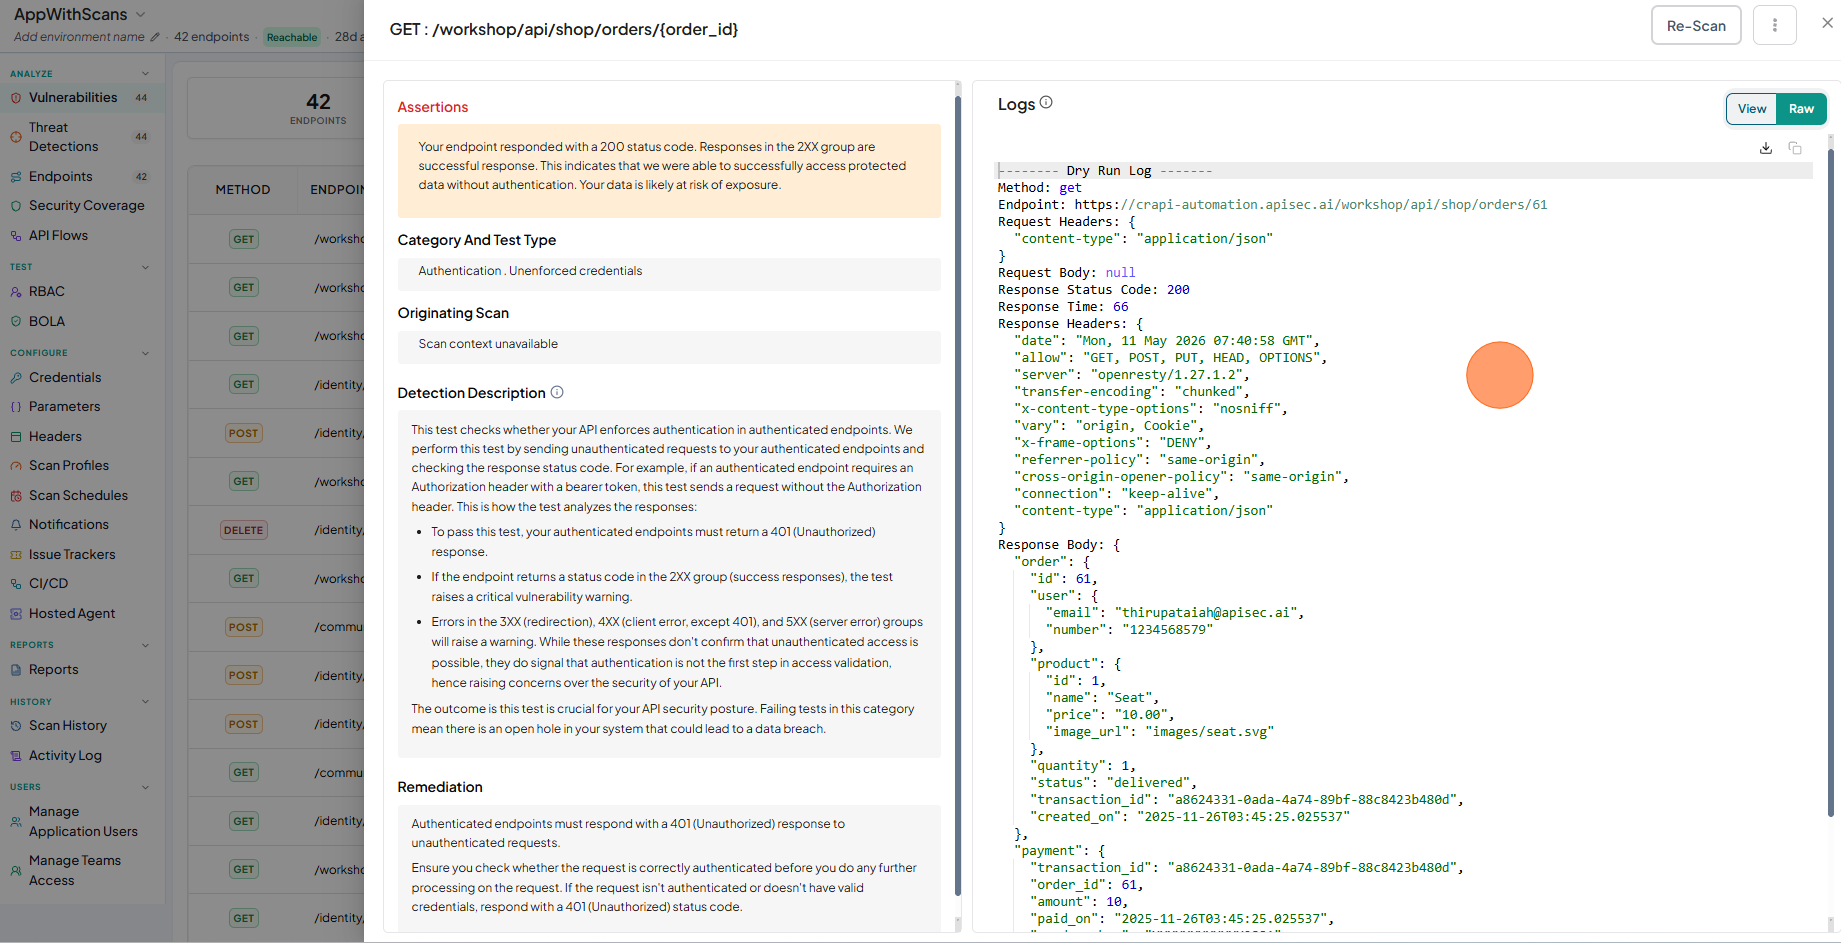
Click a vulnerability row to open its details.
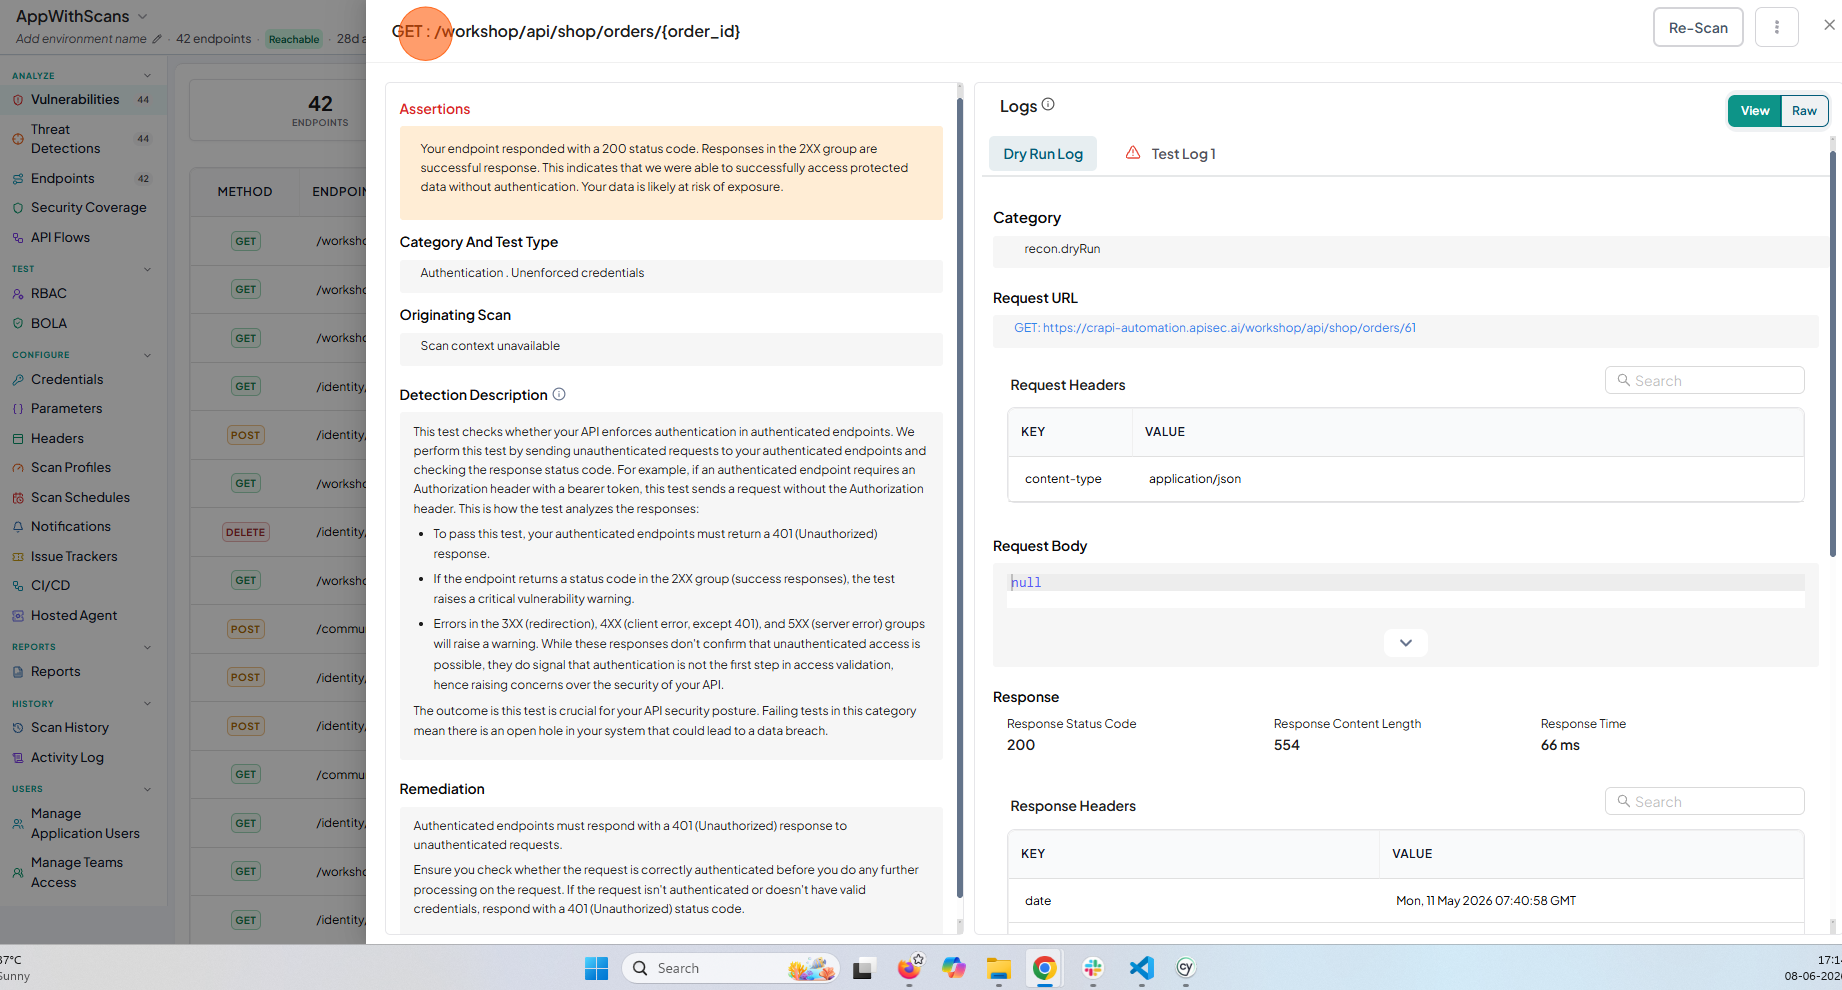
The details page contains the following sections:
-
Header: Shows the Method and URL endpoint of the affected request.
-
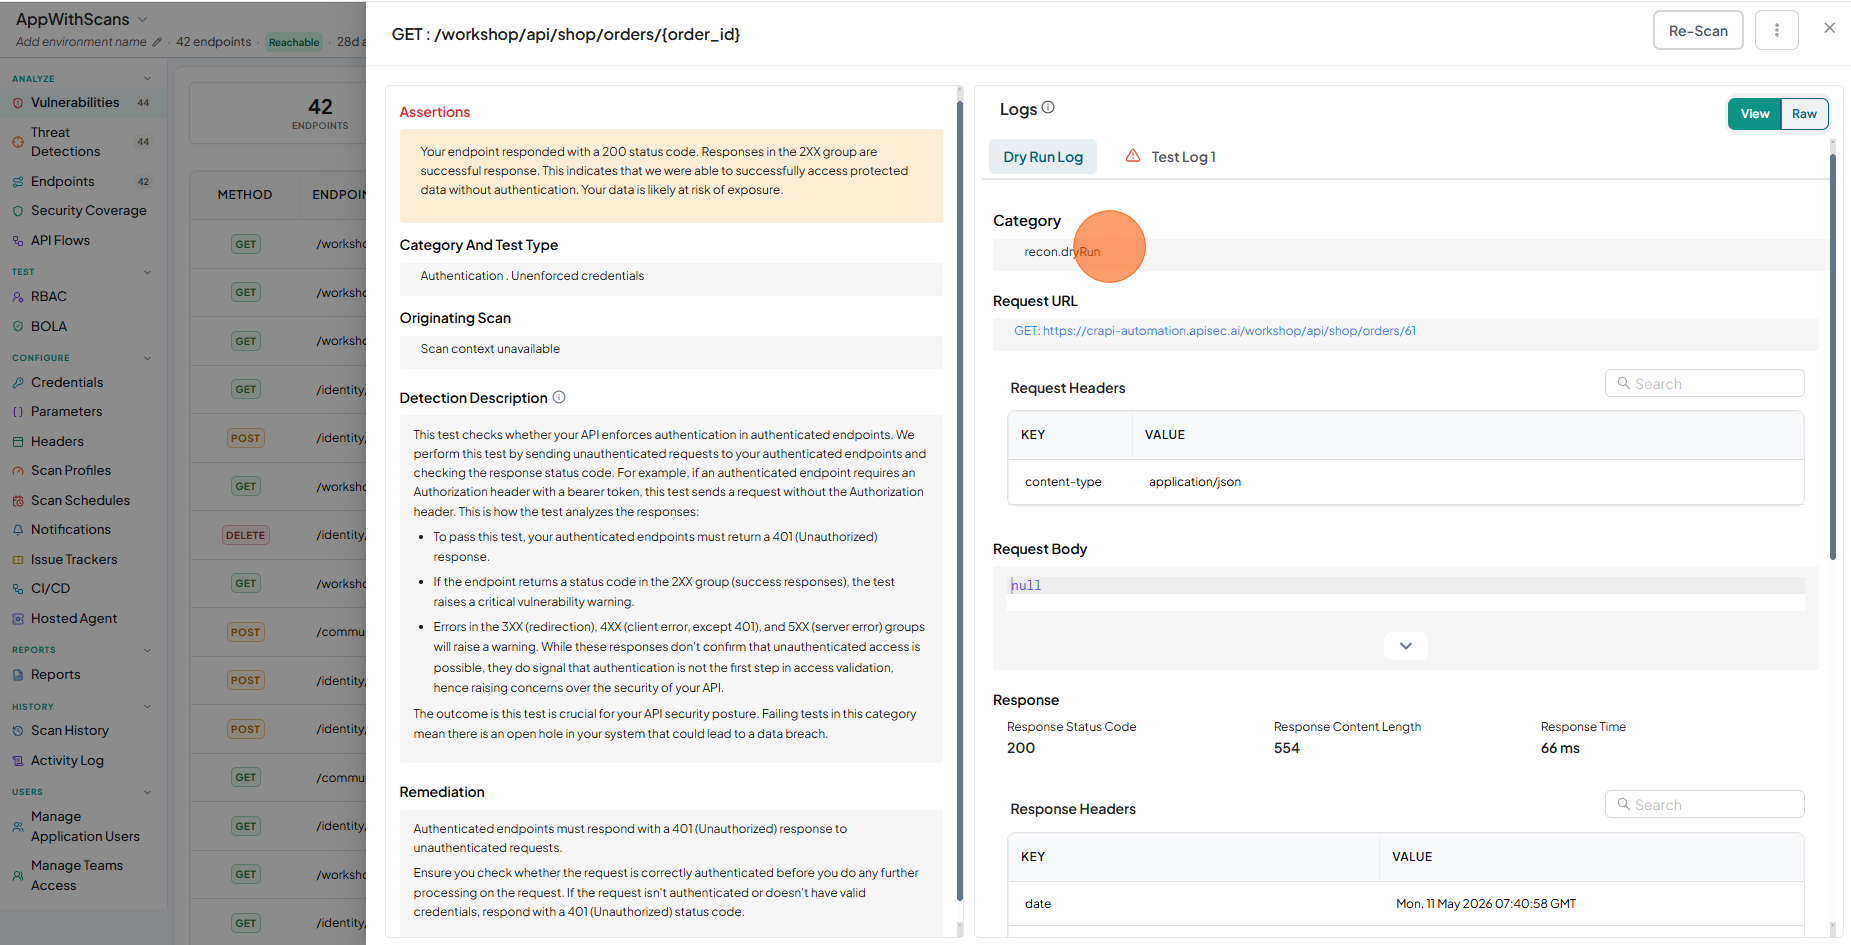
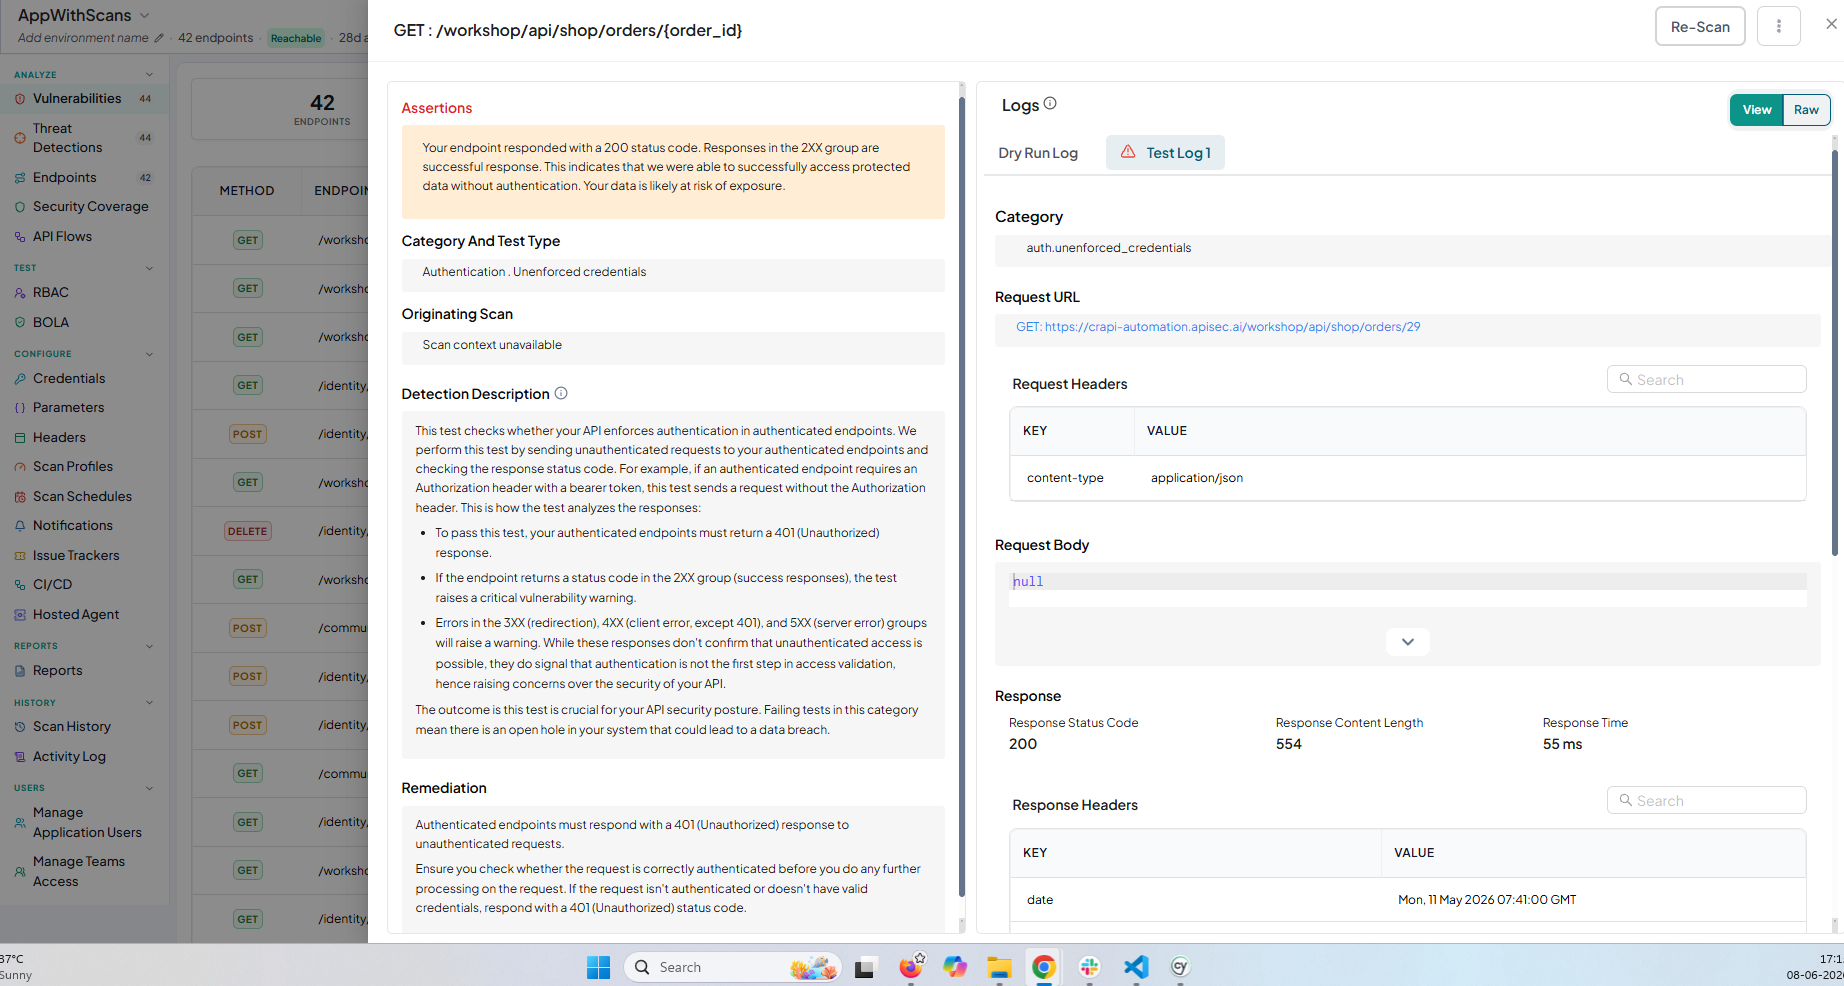
Logs: Shows the detailed logs for each URL endpoint.
-
Raw view: Click Raw to view the logs in raw format.
Re-scan an endpoint
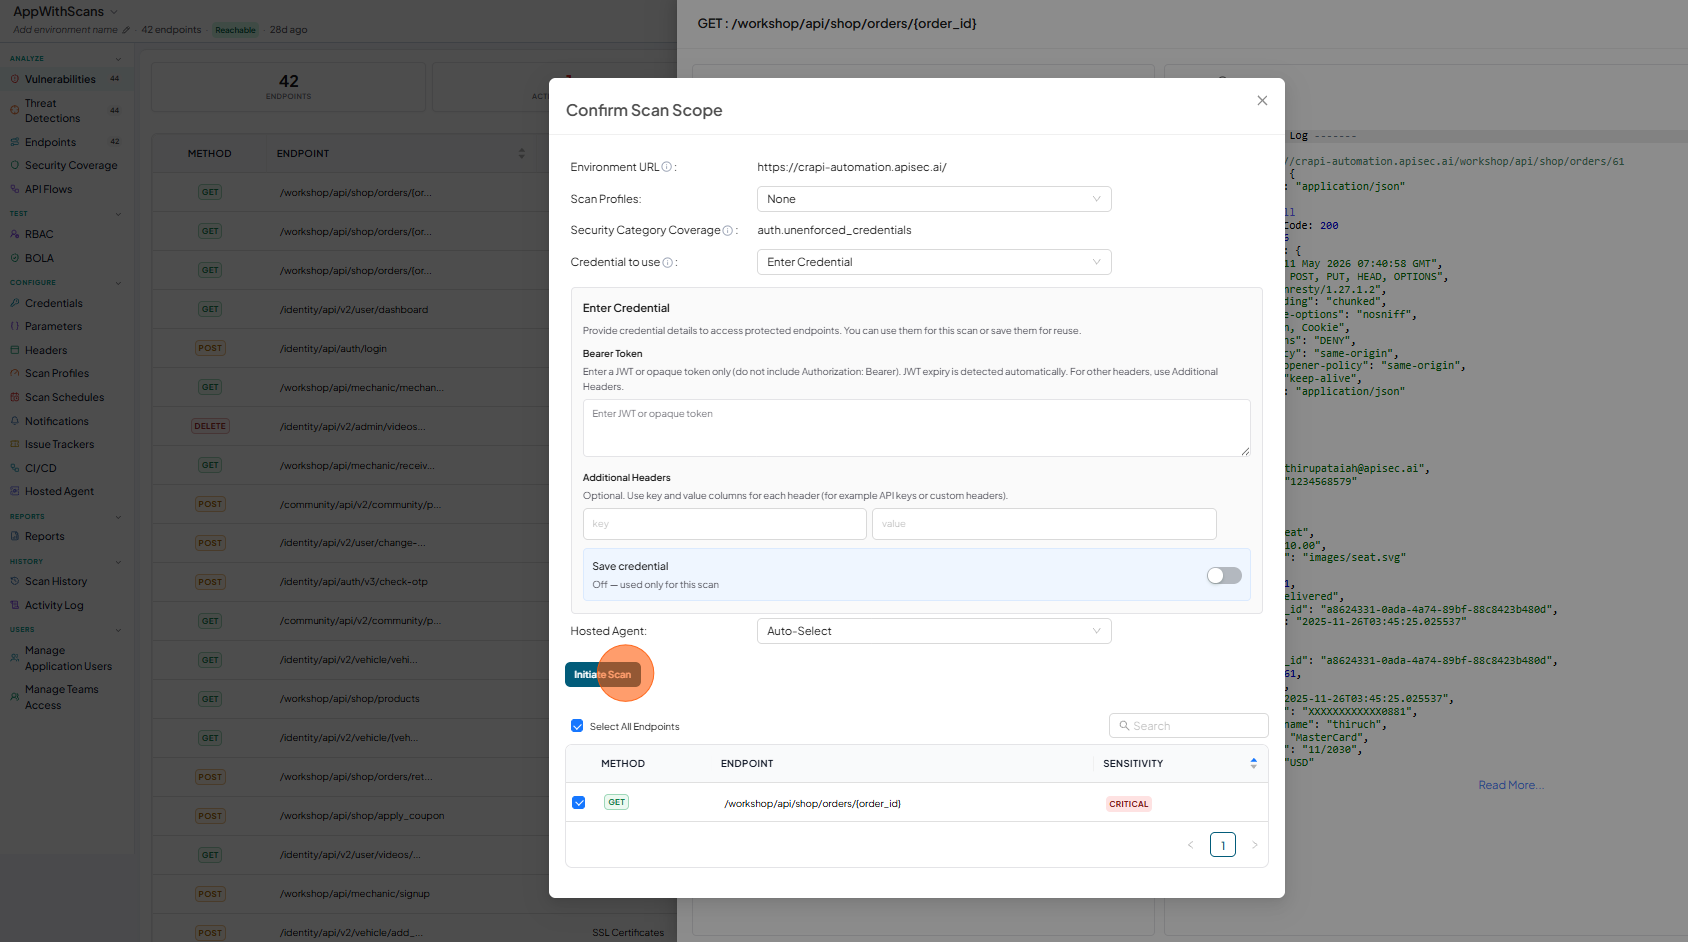
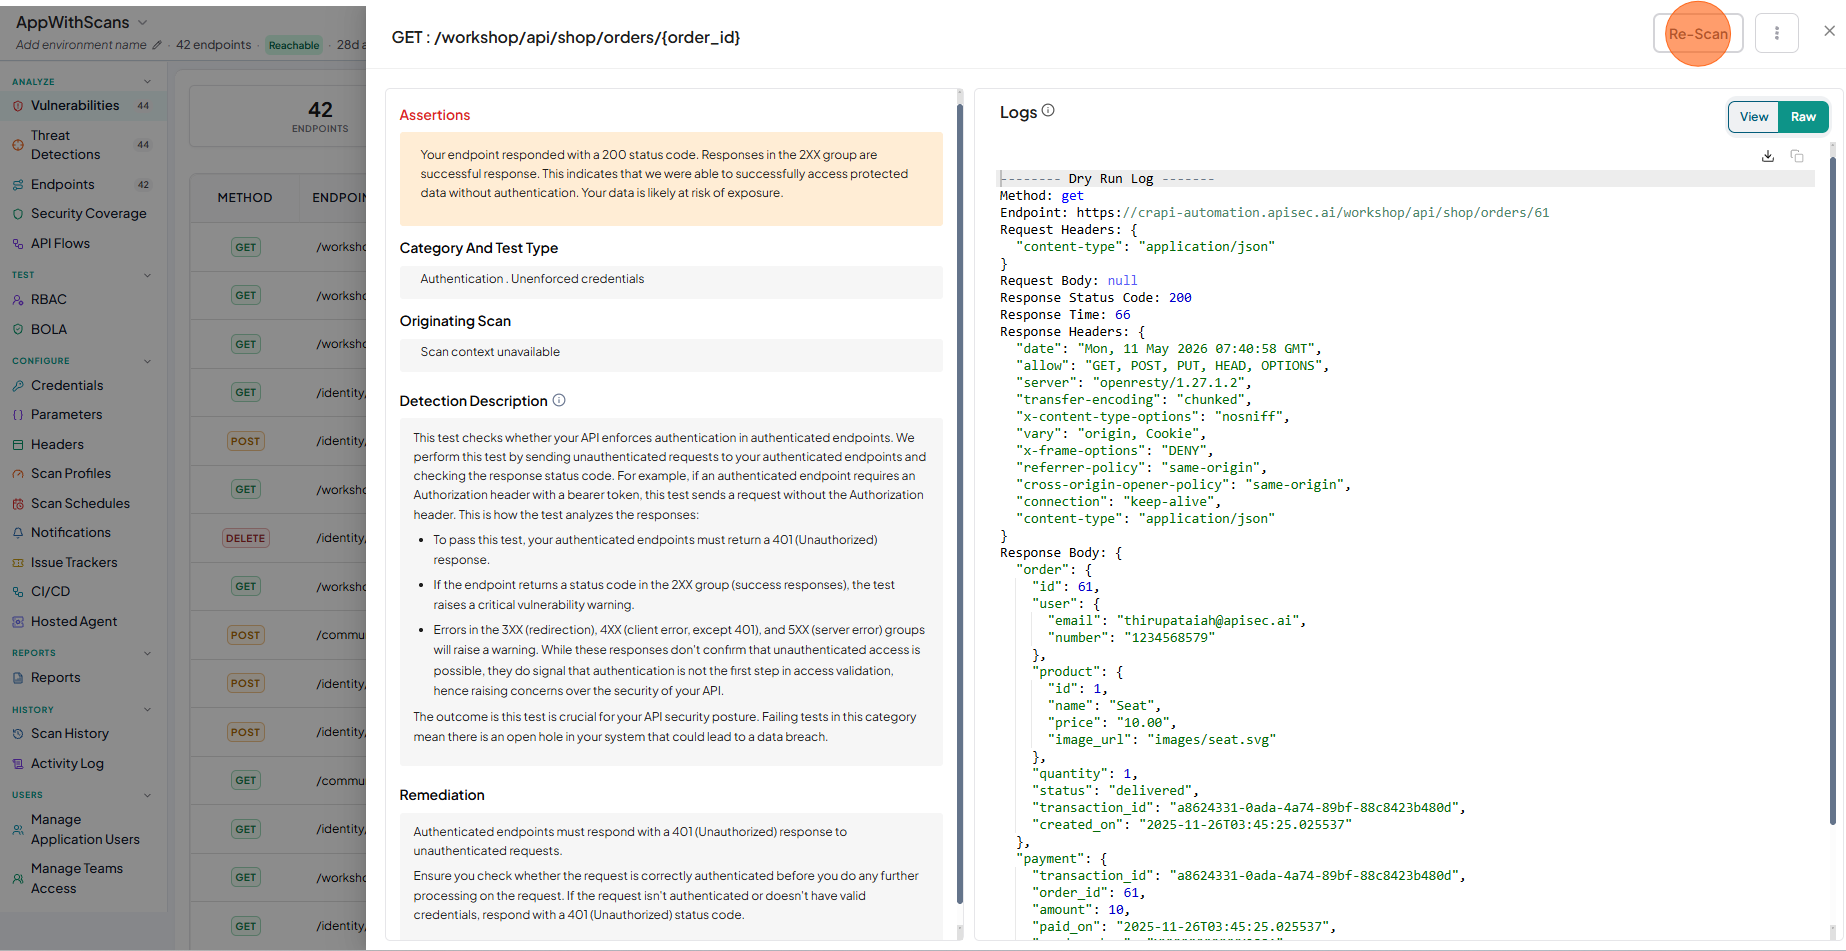
You can initiate a re-scan from the logs section to verify that a vulnerability has been mitigated.
-
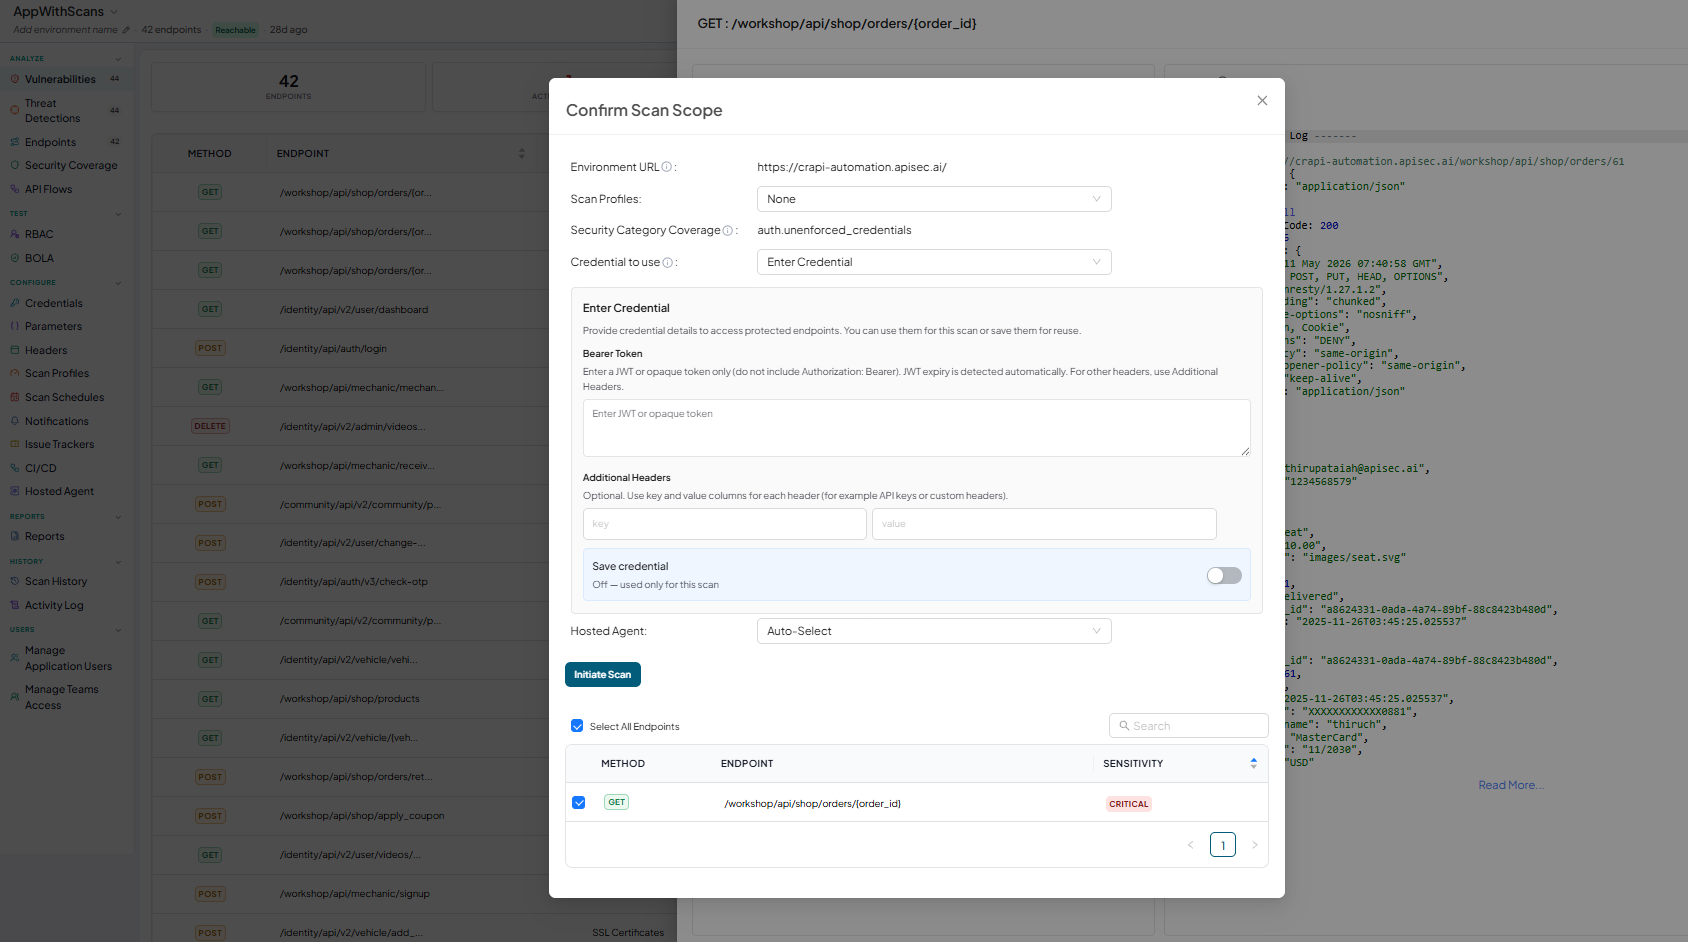
Add or select credentials and click Re-Scan.
-
Confirm the scope.
-
Click Initiate Scan.