Accept the risk of a known vulnerability
Visit Application
-
Open your browser and visit: https://<your-tenant>.apisecapps.com
-
Click on Application
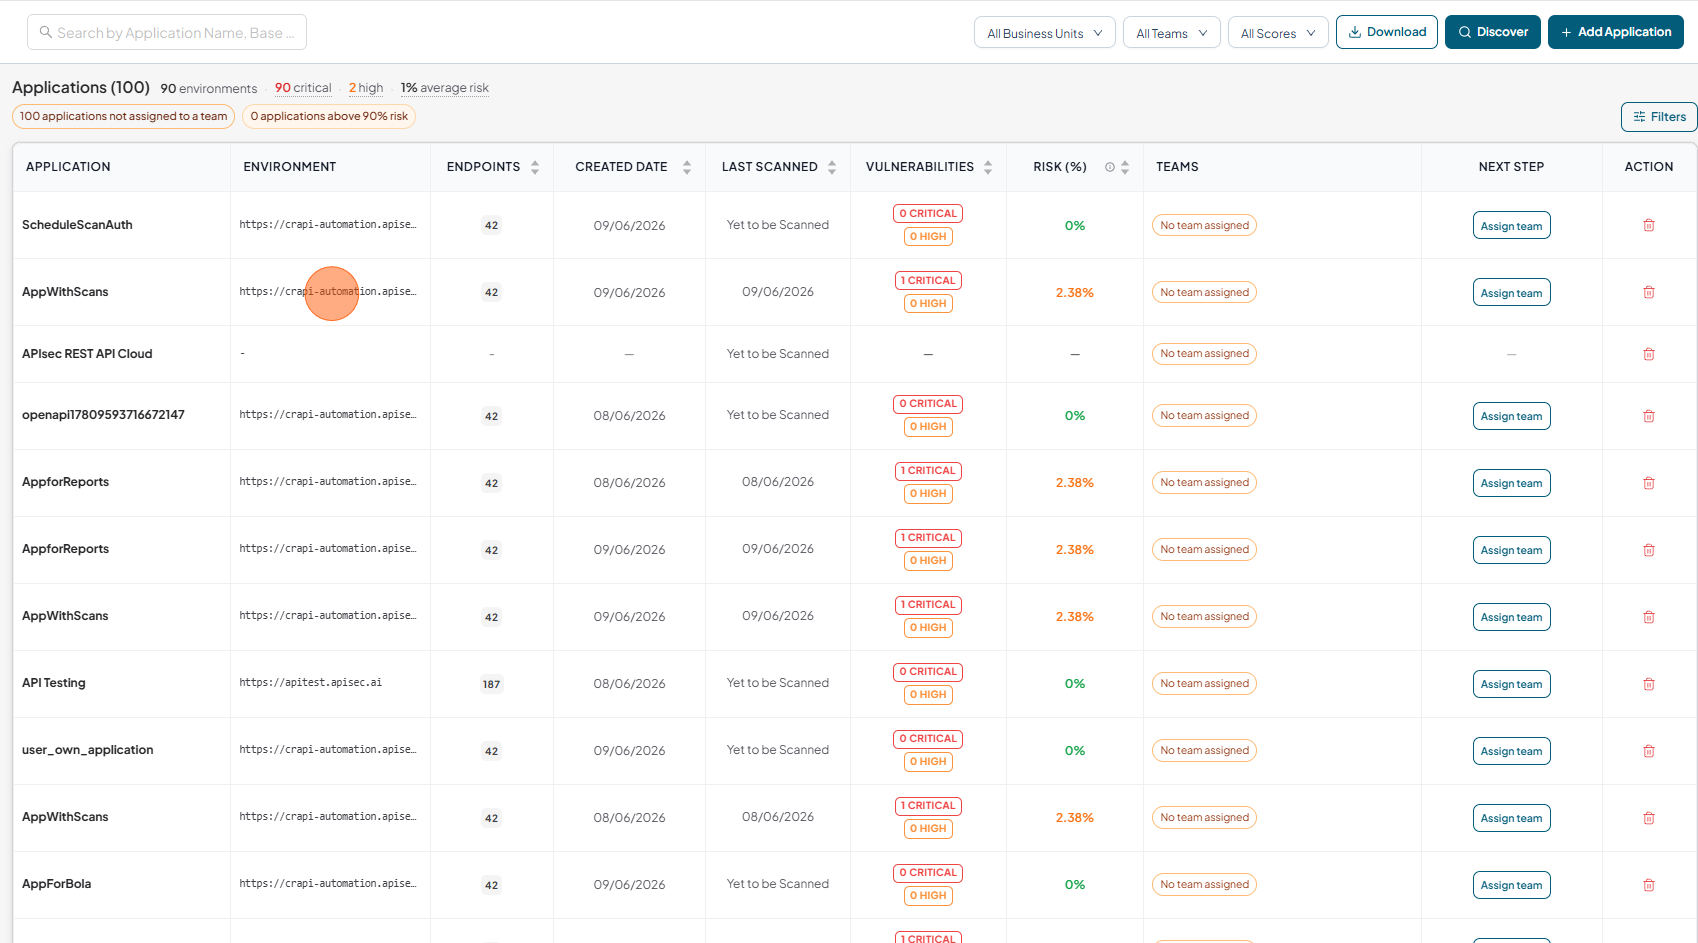
Accept Vulnerability Risk
-
Click "Vulnerabilities" Tab if not selected.
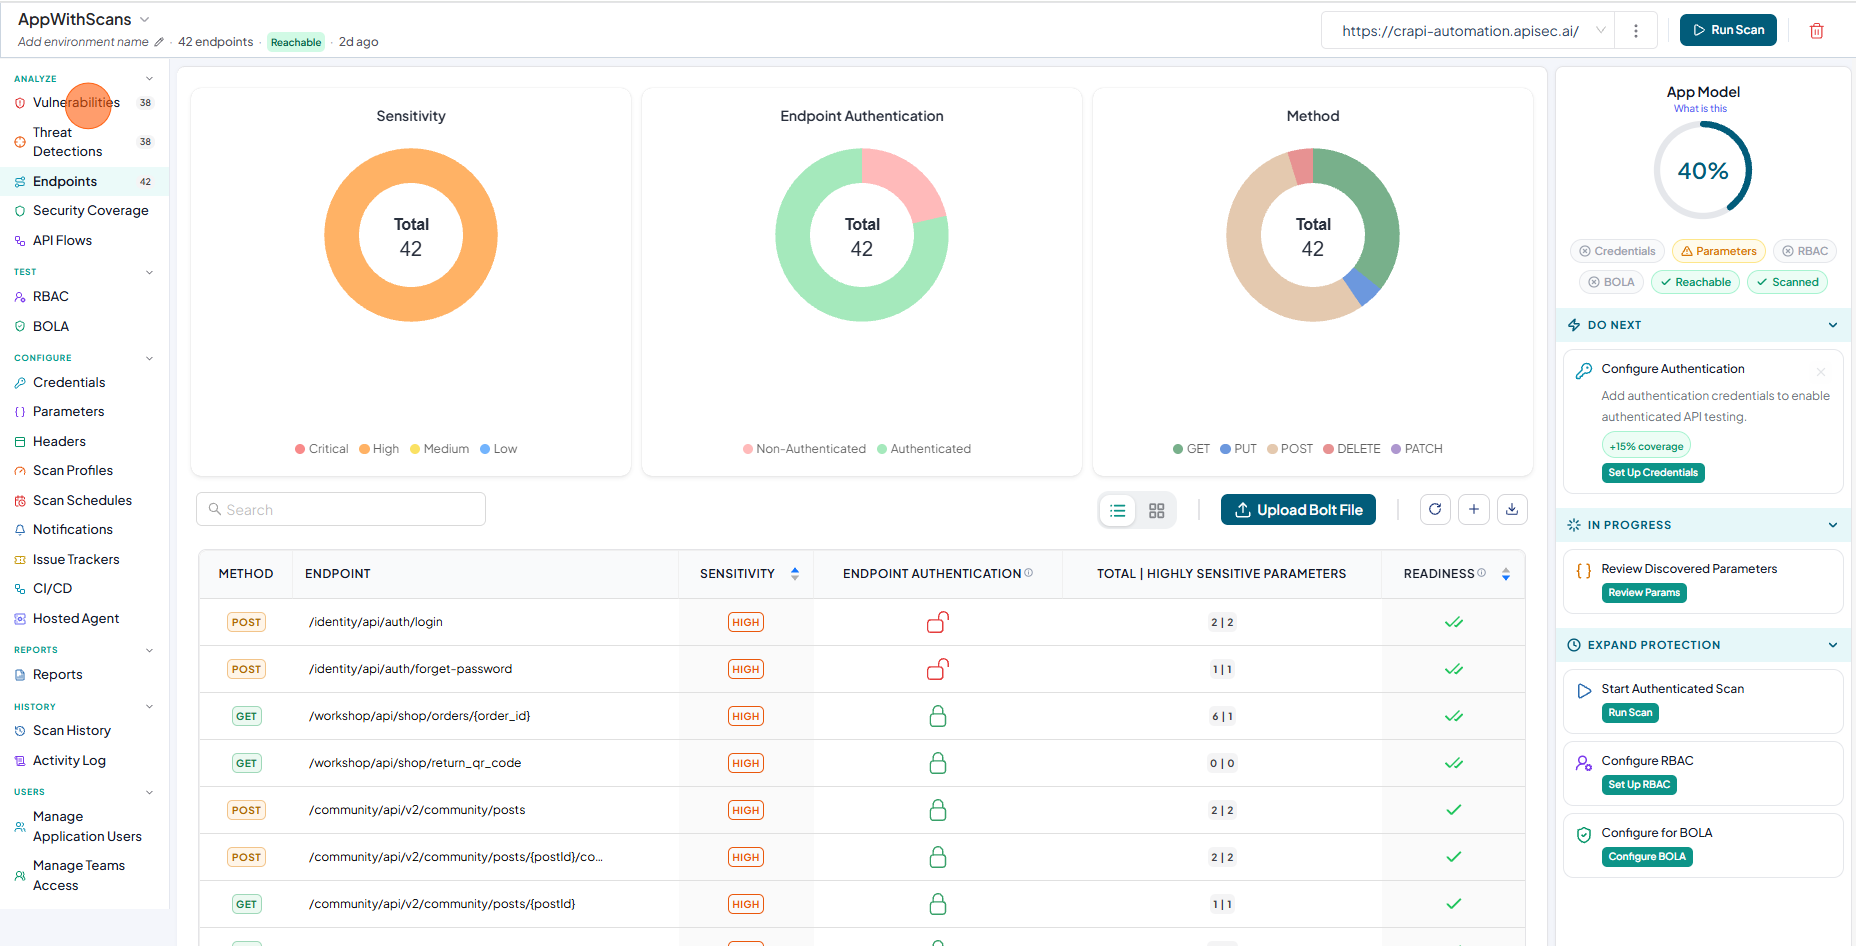
-
The Vulnerabilities page is displayed.
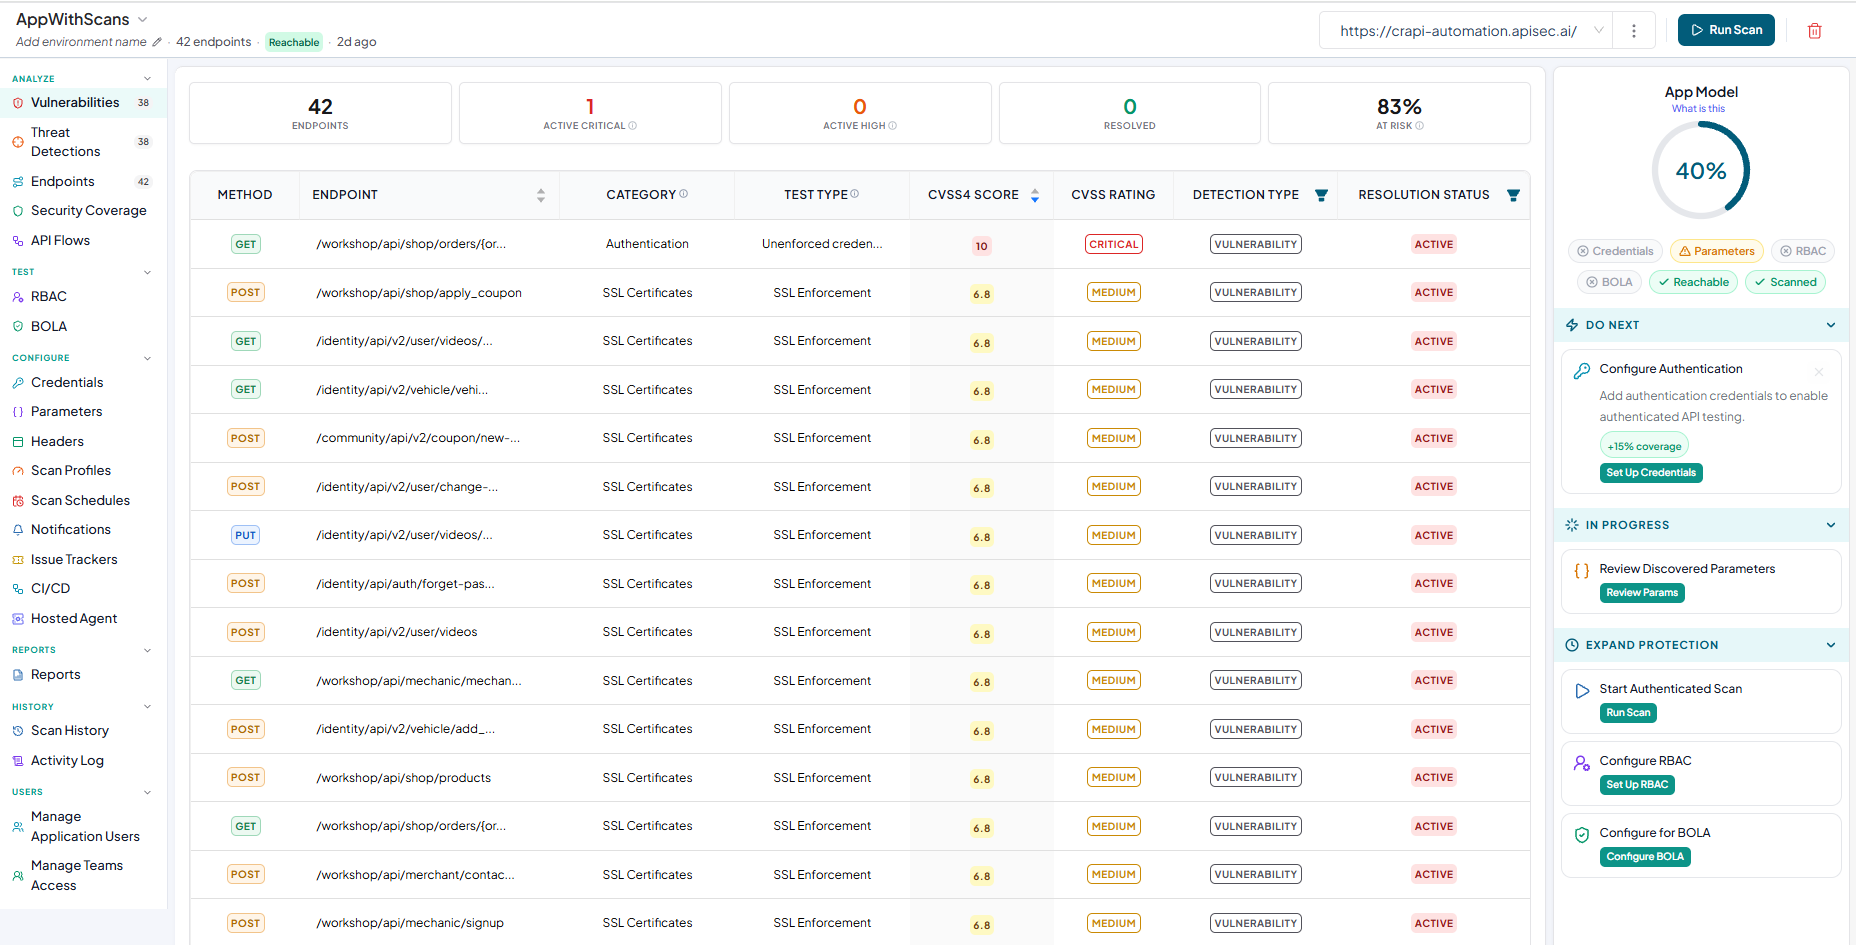
-
Select a vulnerability row to open the Vulnerability Details page.
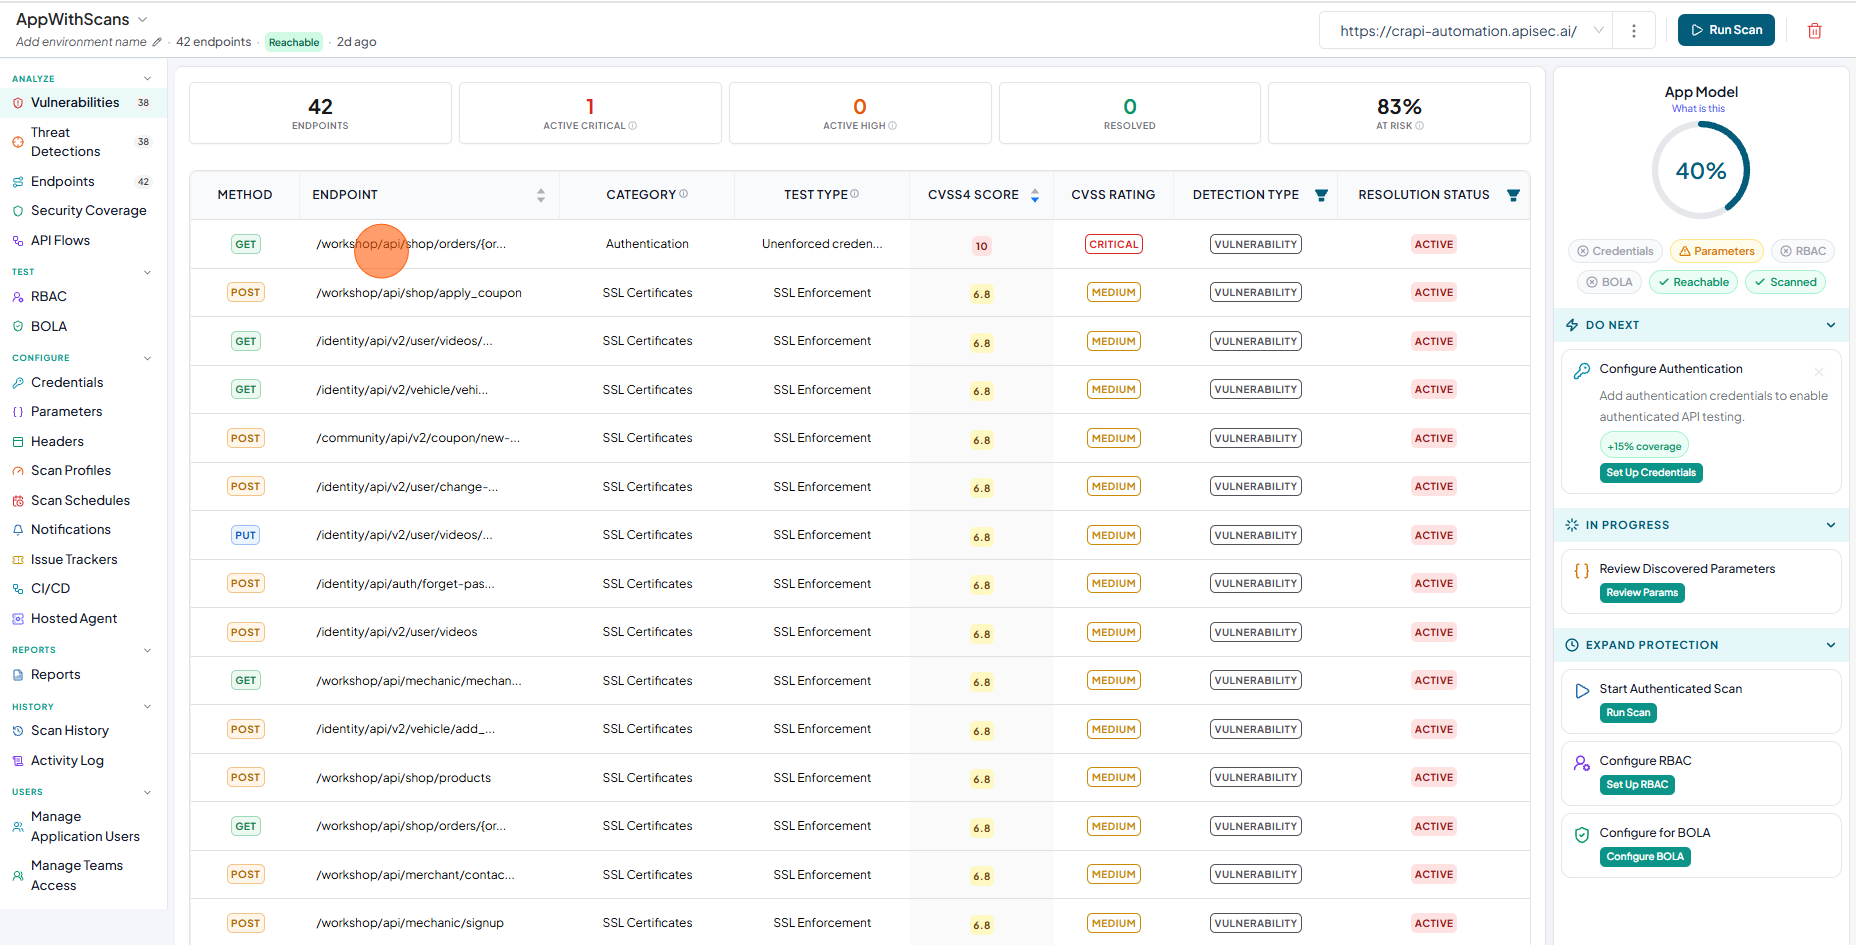
-
Click on the setting dropdown.
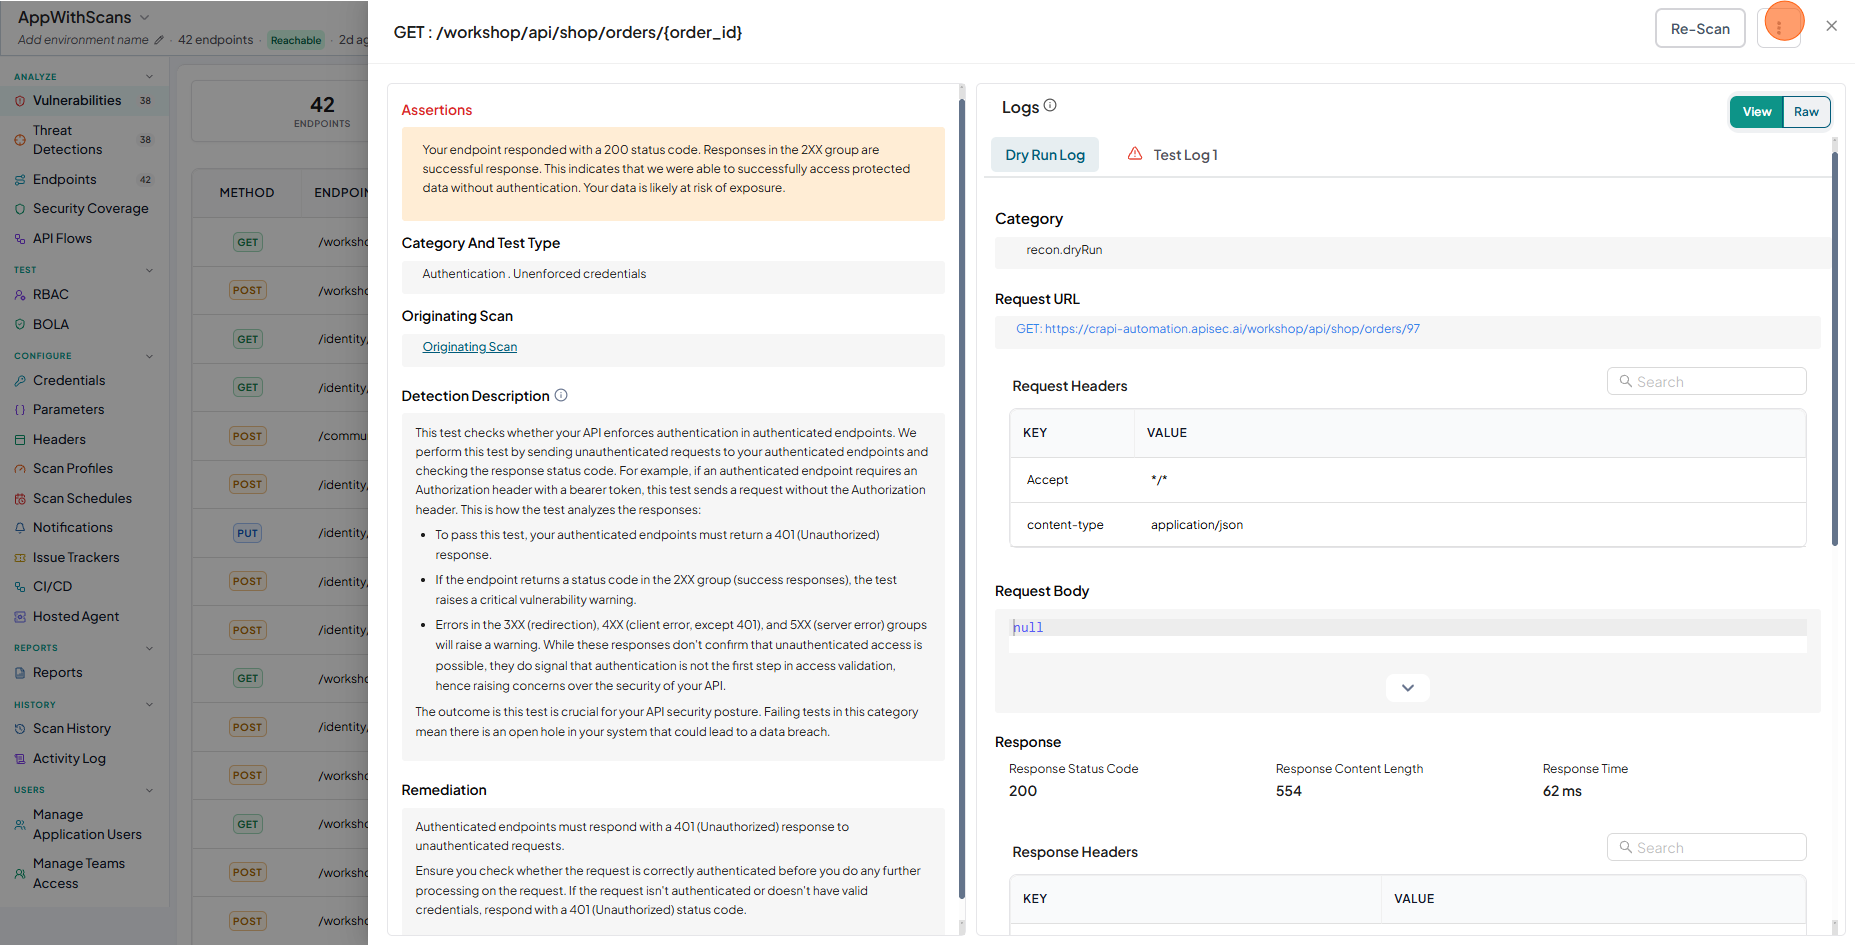
-
Click on the I accept the risk option.
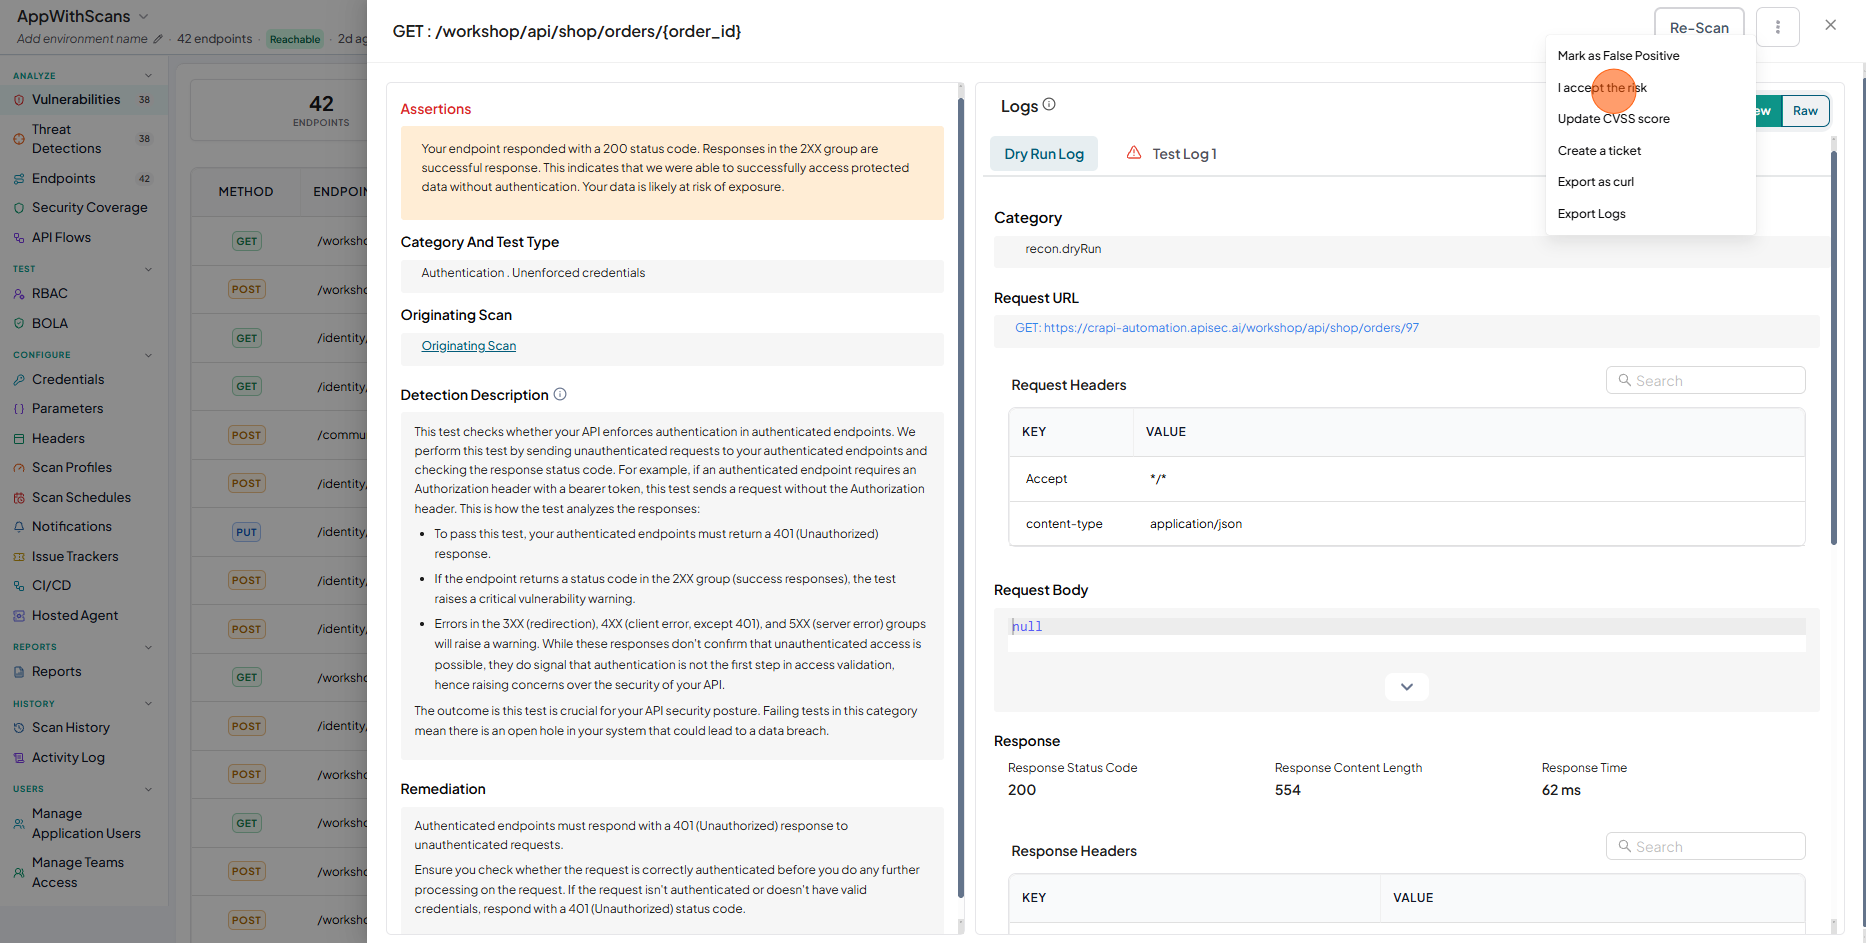
-
Fill the reason and click Yes to confirm
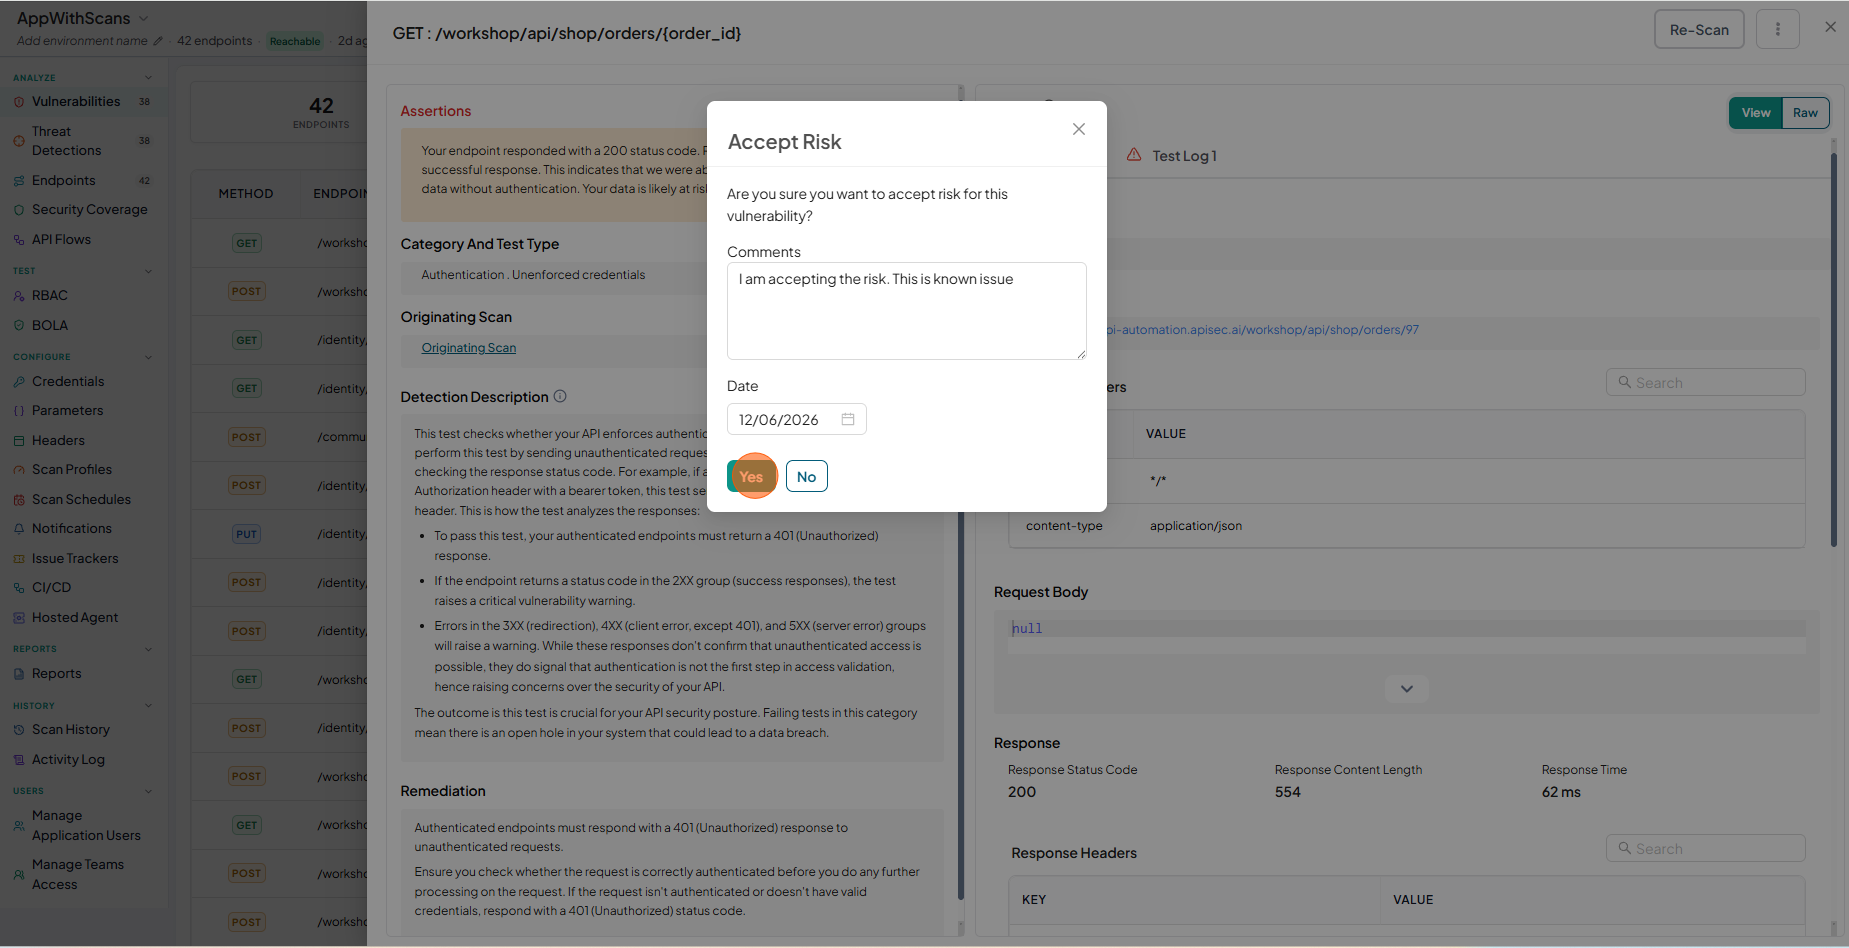
-
Check the Risk Acceptance details in the vulnerability details page
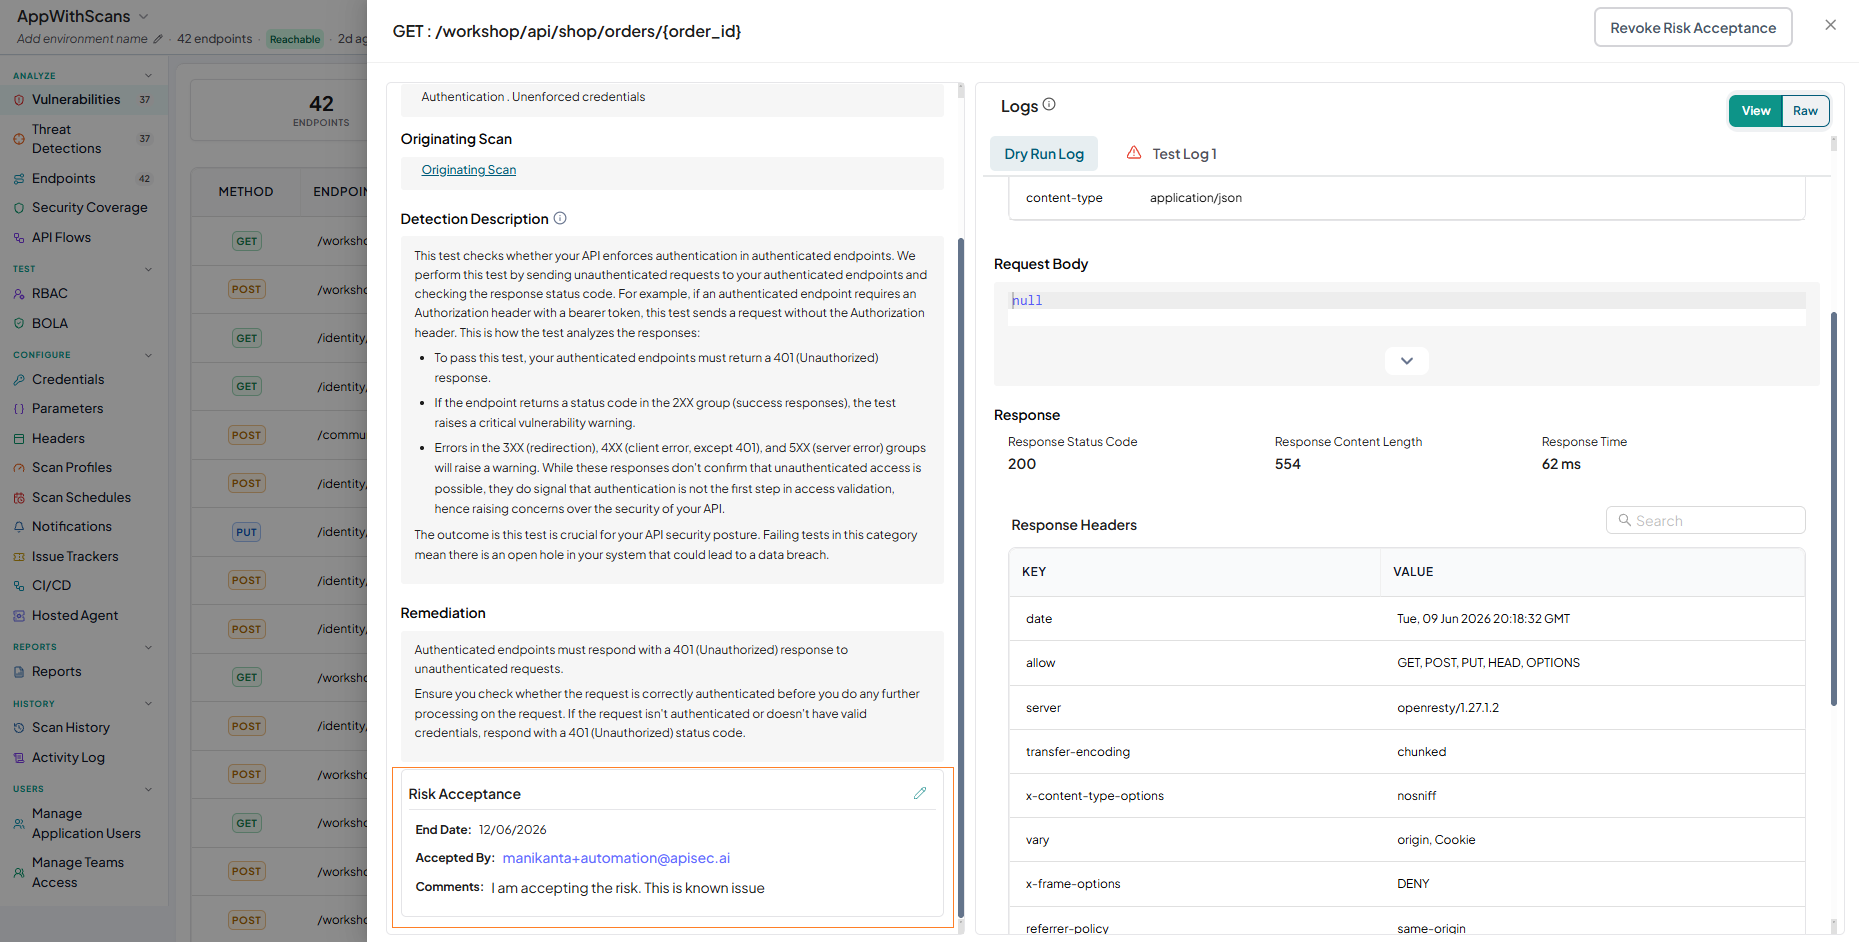
-
Click on close modal
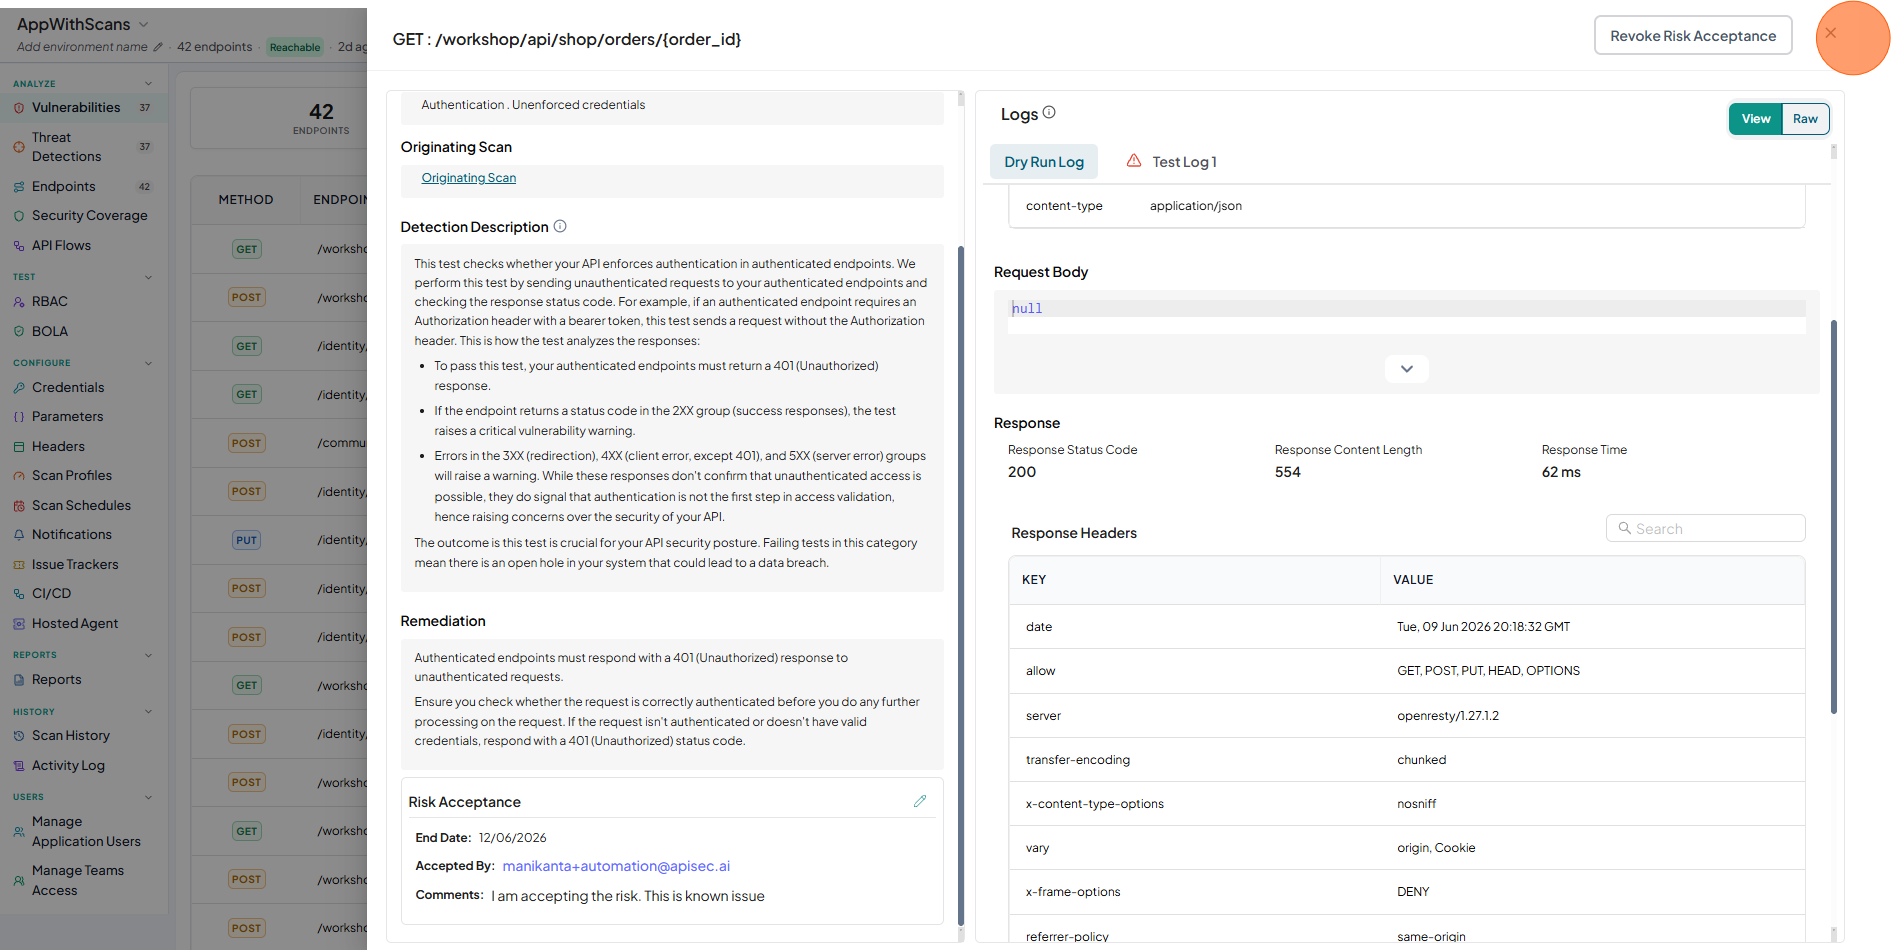
-
Check the Resolution Status of the risk accepted vulnerability, changed to RISK_ACCEPTED
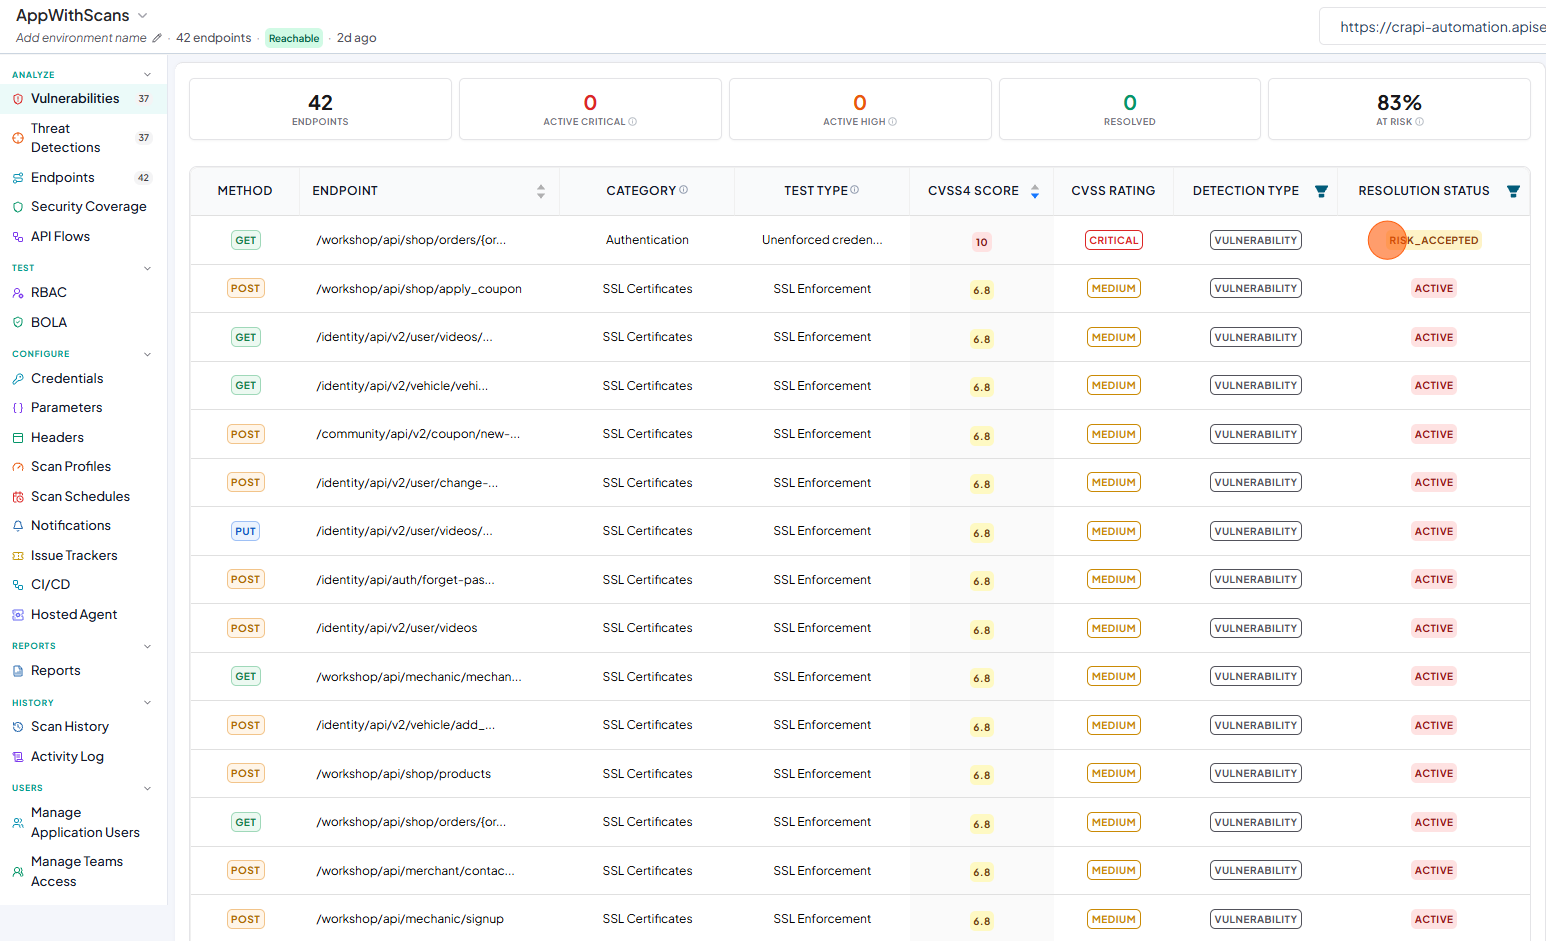 note
Users with the View role cannot accept vulnerability risk in a shared application.
Revoke Accepted Vulnerability Risk
-
Open your browser and visit: https://<your-tenant>.apisecapps.com
-
Click on Application
-
Visit the Vulnerabilities tab and click on the vulnerability which has the Resolution Status as RISK_ACCEPTED
-
Click on the Revoke Risk Acceptance button
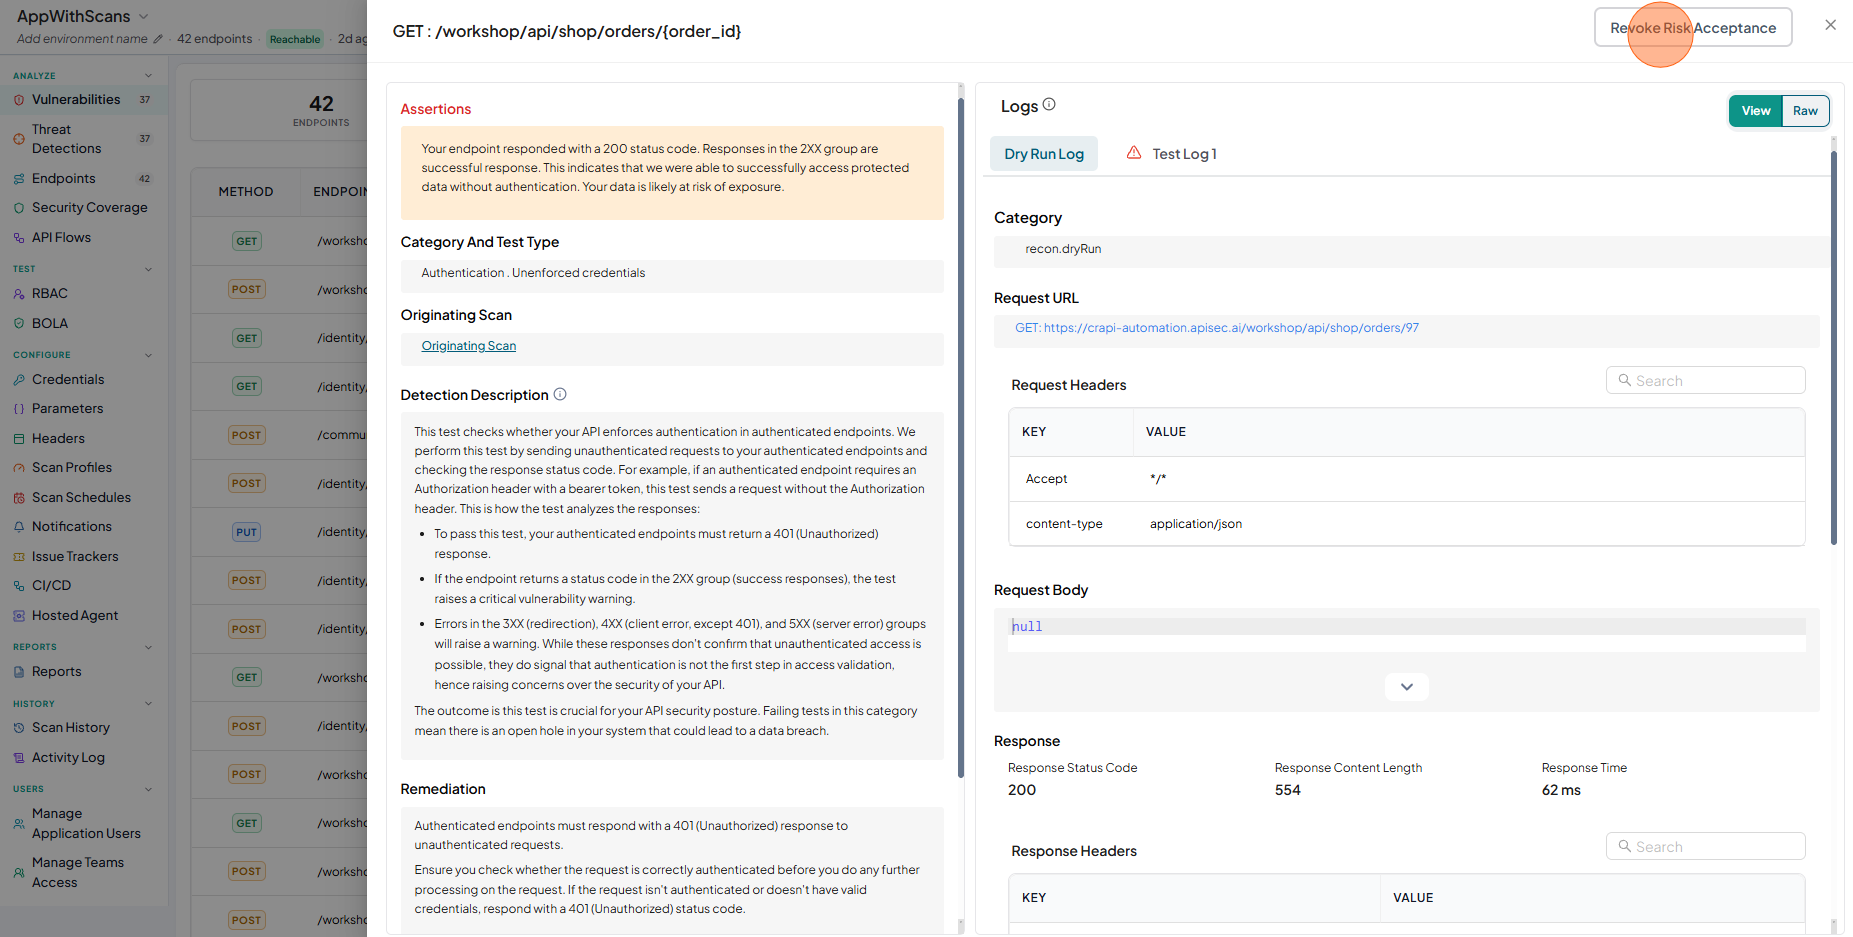
-
The risk acceptance is revoked.
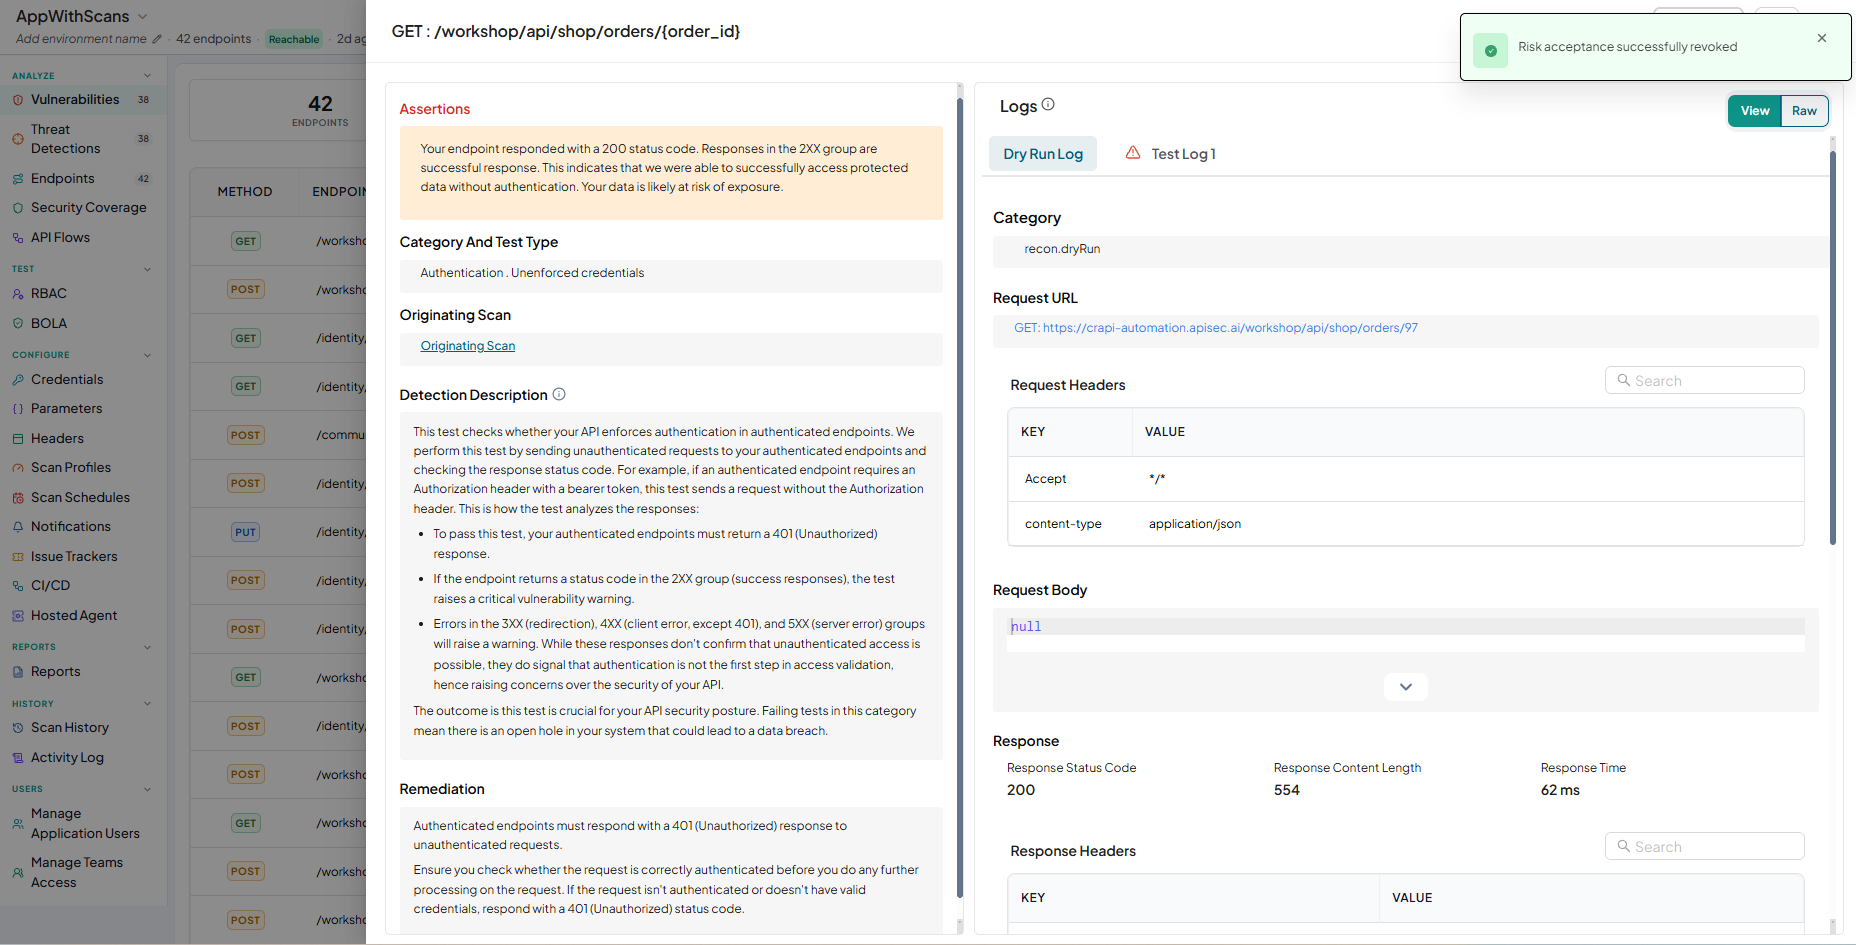
-
Verify that the Resolution Status of the previously risk-accepted vulnerability has changed to Active.
noteUsers with the View role cannot revoke accepted vulnerability risk in a shared application.
Read more about Issue trackers
For additional information, refer to the Issue Trackers FAQ